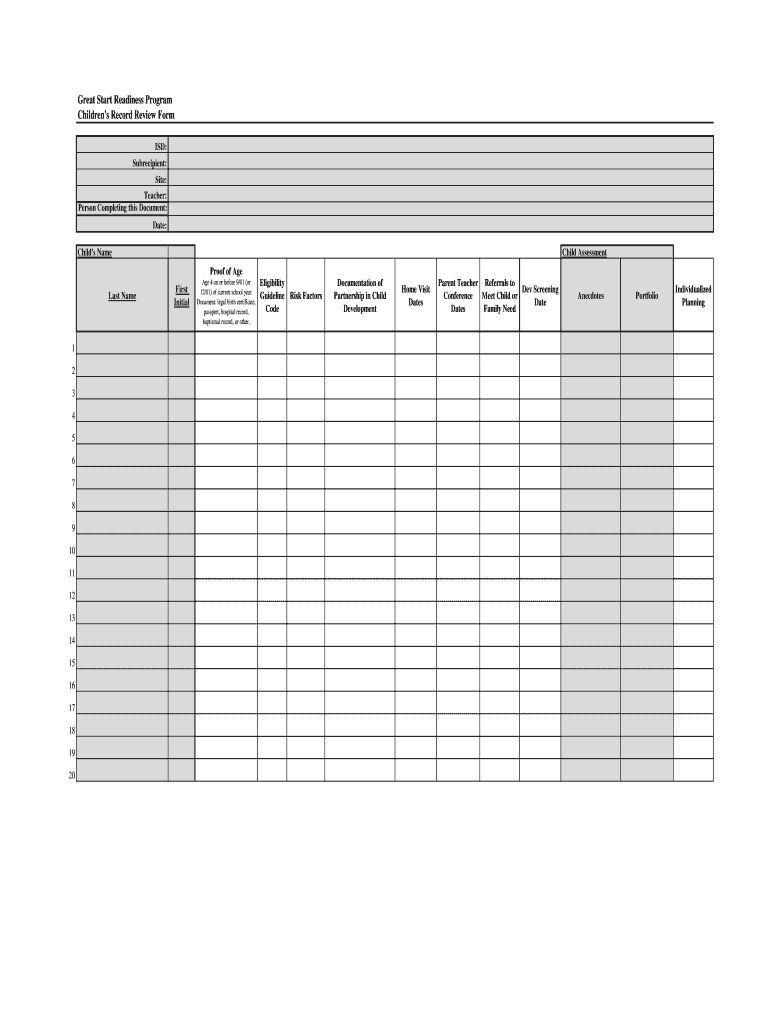
Child Record Review Form Gsrp
Use a Child Record Review Form GSRP template to make your document workflow more streamlined.
What Child Record Review Form Gsrp is
Child Record Review Form Gsrp is a structured record used to document the review of information about a child in a GSRP-related workflow. It gives authorized reviewers a place to record findings, identify the child or case, add dates, and approve the completed review. In signNow, a sender uploads the form, places or confirms fillable fields, assigns each field to the appropriate reviewer, and sends it electronically. Reviewers complete assigned sections, sign where required, and receive a completed copy. The audit trail preserves signer actions, timestamps, and document history for later administrative review.
Who uses this child review form
GSRP educators
Early-childhood teachers and specialists use Child Record Review Form Gsrp to record observations, complete assigned review fields, and confirm their findings with an electronic signature.
Program administrators
Program administrators use the form to coordinate review approvals, verify required information, and retain a consistent record for internal child-service documentation.
Who benefits from child record reviews
Child Record Review Form Gsrp is most useful where several authorized people must review, sign, and retain child-specific information.
A preschool program uses Child Record Review Form Gsrp to document child observations, review decisions, and authorized signatures before updating internal records. A school district office coordinates Child Record Review Form Gsrp reviews across classrooms, preserving consistent approvals and an accessible record of each reviewer’s action. A regional early-childhood provider uses Child Record Review Form Gsrp to route reviews between teachers, specialists, and administrators without exchanging paper copies.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the review workflow works
Child Record Review Form Gsrp moves from document preparation to assigned review, electronic signature, and audit-ready storage.
Upload: Upload the Child Record Review Form Gsrp document. Prepare: Auto-detect or place fields for each reviewer. Route: Send assigned sections in the required order. Complete: Complete signatures and preserve the audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete the form in signNow
Follow the signNow workflow for preparing, routing, completing, and preserving Child Record Review Form Gsrp.
Upload:
Upload the current form file. Add fields:
Confirm or place review fields. Assign:
Assign each field to a reviewer. Send:
Send the form for completion. Archive:
Review signatures and download evidence.
Recommended setup for child record reviews
Use a controlled signing workflow for Child Record Review Form Gsrp records, with verified signers, audit evidence, and policy-based retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Detailed signer action history |
| Document retention | Retain under applicable program policy |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
Security for child review records
Stored data:
Data transfer:
Security reporting:
Information security:
Health information:
Electronic signatures:
How the audit trail records reviews
The audit trail documents the technical events surrounding a Child Record Review Form Gsrp signature, helping administrators reconstruct who acted and when.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident sealing:
Action history:
Audit export:
Privacy pitfalls in child record reviews
Including unnecessary child or family information can expose personal data beyond the purpose of the review and increase access-control obligations. Missing parent or guardian consent language can leave the record unclear about authorization for collecting, reviewing, or sharing child information. Sending the form to an incorrect email address can disclose child information and create an incomplete or disputed review record. Allowing broad template access can let unauthorized staff edit fields or view completed Child Record Review Form Gsrp records.
State rules and document exclusions
State notary rules
Real-estate deed
Wills and codicils
Court orders
Family-law documents
Best practices for child record reviews
A controlled template, clear signer assignments, and preserved audit evidence reduce rework when completing Child Record Review Form Gsrp.
Map every required review field
Match authentication to information sensitivity
Preserve the form and audit evidence
Test the complete review workflow
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting child record reviews
Resolve the specific upload, signer, authentication, compliance, and record-integrity issues that can interrupt a Child Record Review Form Gsrp workflow.
Upload the original Child Record Review Form Gsrp file again and confirm that the document opens correctly before adding fields. If field detection misses a printed line, place the required field manually and test the resulting document before sending it.
Check the recipient address, spam filtering, and signing order first. signNow can send the form by email or through a signing link, but the recipient still needs access to the correct address and assigned fields.
A Business plan includes legally binding eSignatures, audit trails, templates, mobile apps, ISO 27001, SOC 2, and GDPR support. HIPAA workflows require signNow’s HIPAA-compliant configuration and a BAA where applicable.
Use SMS OTP or another available authentication control when the child record requires stronger signer verification. Authentication should match organizational policy, the data involved, and any applicable FERPA or HIPAA obligations.
Review the completed document and audit trail together rather than relying only on the visible signature. The audit trail records signing activity and timestamps, supporting attribution and reproducibility under ESIGN and UETA.
Use a shared template with assigned roles and required fields, then limit editing permissions to authorized administrators. A completed form should be corrected through a documented process, not silently replaced after signing.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.