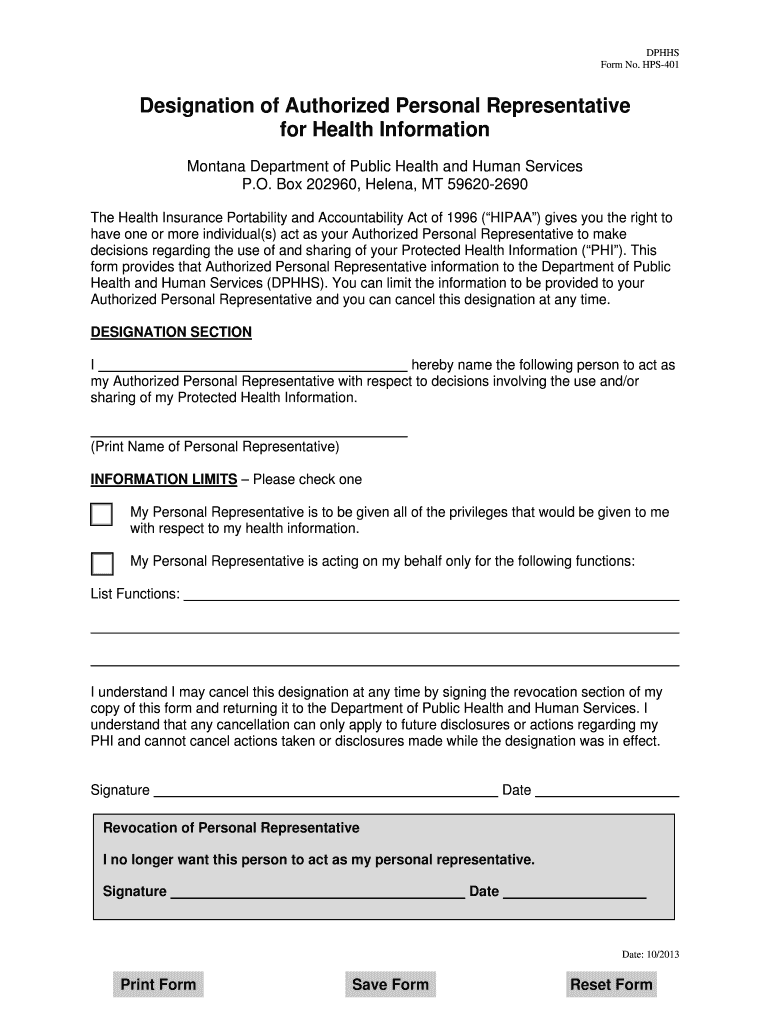
Authorization For The Use And Disclosure Of Health Dphhs Form
Use a Authorization For The Use And Disclosure Of Health Dphhs template to make your document workflow more streamlined.
What this health authorization does
The Authorization For The Use And Disclosure Of Health Dphhs Form records a person’s permission for a named party to use or disclose specified health information. The signer reviews the information categories, recipient, purpose, and any expiration or revocation terms stated on the form, then signs and dates the authorization. A digital workflow can capture intent, signer identity, timestamps, and a reproducible copy. HIPAA requirements may apply when protected health information is involved, while ESIGN and UETA address electronic signing without replacing issuer instructions or state-specific rules.
Legal standing and document limits
An authorization is generally admissible when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains accurate and reproducible under ESIGN and applicable state law. These rules do not override exclusions for wills, codicils, testamentary trusts, court orders, or official court filings.

How the authorization workflow works
The signNow workflow moves the health authorization from an uploaded document to a signed, traceable electronic record.
Upload the form: Upload the completed authorization and confirm its page structure. Check fields: Review detected fields and add missing signature or date fields. Request signatures: Send the authorization to the patient or representative for signing. Archive records: Store the executed form with its audit trail and completion certificate.
Who benefits from this authorization
Healthcare administrators use the authorization to collect patient permissions before releasing protected health information to named recipients. They can route the form electronically, apply signer authentication, and preserve the completed record for HIPAA-governed operations when a business associate agreement is required by the workflow and parties involved. There is no signNow customer story specifically identifying this form, so this profile remains role-based and factual. Housing and human-services agencies use signed authorizations when clients permit disclosure to an identified organization or representative. A controlled template helps staff capture the permitted information, recipient, purpose, and signature without recreating the document for every case. The audit trail supports later review without replacing the agency’s retention policy or state requirements. They should confirm the form’s originating agency instructions before deployment. Patient-service teams and records departments use the form when a person authorizes disclosure of health information to a named third party. signNow can collect signatures remotely, document the signing event, and make the final authorization available to authorized staff. The workflow must still follow the form issuer’s instructions and applicable HIPAA requirements.
Who uses this health authorization
Healthcare records
Healthcare records departments use the authorization for patient-directed disclosure requests, recipient permissions, and consent records. Staff should verify that the form identifies the information, recipient, purpose, and signer before routing it through a HIPAA-governed process.
Public services
Human-services and public-sector offices can use the form when a client authorizes disclosure to a named person or organization. The office should preserve the executed copy, audit history, and any issuer-specific instructions alongside the case record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Pitfalls when completing the authorization
Leaving the recipient, purpose, or categories of health information incomplete can make the authorization difficult to process or apply. Sending protected health information through the wrong access path can expose sensitive data beyond the authorization’s stated recipient. A missing signature date or unclear signer identity can weaken the record’s evidentiary value during later review. Using an electronic workflow without required consumer disclosures can create an ESIGN consent problem for consumer-facing records.
Best practices for completing the form
Accurate fields, deliberate consent, and controlled records help keep this health-information authorization usable after signing.
Complete recipient and purpose fields
Confirm the information scope
Match authentication to disclosure risk
Preserve the audit trail
Recommended authorization workflow setup
Configure the signing process around signer identity, protected health information, evidence preservation, and the retention rule that governs the completed authorization.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enabled with completion certificate |
| Document retention | Six years when HIPAA applies |
| Encryption | TLS 1.2/1.3 and AES-256 at rest |
Quick steps for this authorization
Use the original authorization, verify every disclosure field, and preserve the signed document with its completion evidence.
Upload document:
Upload the exact DPHHS authorization file. Review fields:
Check detected fields against the printed form. Add signer:
Add the signer and required authentication. Complete workflow:
Send, monitor, and download the completed record.
What the audit trail records
The audit trail separates signer activity from the authorization’s substantive terms and creates a reviewable history for the completed health-information record.
Authenticate signer:
Capture timestamp:
Record document hash:
Seal document:
Create certificate:
Export audit trail:



Ways to send and sign the authorization
- Use the signNow web app when staff need to upload the DPHHS authorization, place fields, and manage recipients from a desktop workflow.
- Use the signNow mobile app when authorized staff need to review or sign the form from an iOS or Android device.
- Use kiosk mode when a supervised office process requires a person to sign on a shared device without changing the authorization’s stated scope.
- Use a shareable signing link when the approved recipient needs controlled access without a separate email invitation.
Retention rules for authorization records
Retention depends on the record’s role, the health-information rules involved, and any longer state or legal-hold requirement.
Six years for HIPAA records
IRS period depends on record
State schedule may extend retention
Legal hold overrides deletion
Retain the audit record
Troubleshooting this authorization workflow
These answers address field detection, electronic consent, PHI safeguards, signer access, plan selection, and preservation of the completed authorization.
Upload the authorization as a PDF or supported document, then review signNow’s detected fields. Add signature, date, and required text fields manually when automatic detection does not identify the form’s blanks. Confirm the final field placement against the issuer’s original instructions before sending.
The Business plan includes templates, audit trails, mobile apps, and legally binding eSignatures at $8 per user per month with annual billing. Business Premium is $15 and adds bulk send. Select the plan based on workflow volume and required controls, not solely on this form.
HIPAA compliance is available when the required business associate agreement is in place and the workflow is configured appropriately. signNow states that its HIPAA offering protects private health information with a BAA required. Review organizational safeguards and the disclosure form’s instructions before sending.
For a consumer-facing electronic record, ESIGN requires disclosure of the right to receive paper, access to the electronic format, and procedures for withdrawing consent under 15 U.S.C. §7001(c). Capture that consent separately when the transaction falls within the consumer-disclosure rule.
If the signer cannot complete the form, verify the email or signing link, resend the request, or use an approved authentication method. signNow’s mobile apps support signing, while the sender should avoid changing the authorization’s substantive scope after consent begins.
Use signNow’s audit trail and completion record to show timestamps, signer activity, and the final document. Store both with controlled access. The audit trail supports evidence but does not determine the retention period; HIPAA, state law, issuer policy, or a legal hold may control.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.