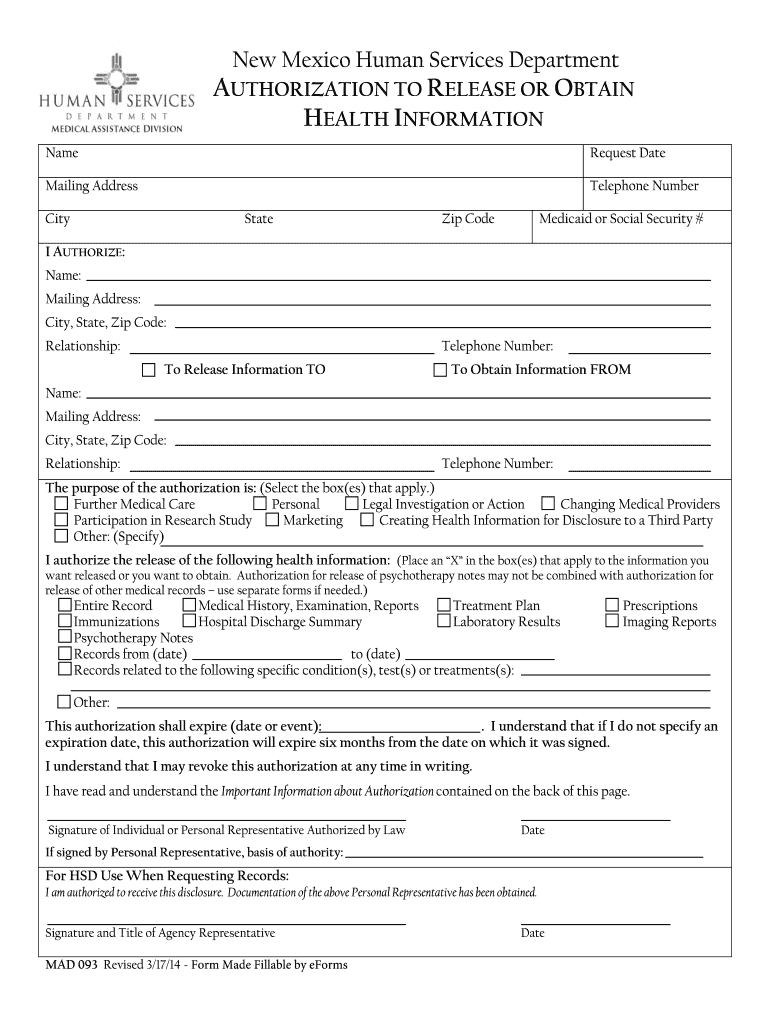
New Mexico HIPAA Release Form
Use a New Mexico HIPAA Release Form template to make your document workflow more streamlined.
What is a New Mexico HIPAA release form?
A New Mexico HIPAA Release Form is a written authorization allowing a covered health care provider or plan to disclose specified protected health information to named people or organizations. It identifies the patient, the information authorized for release, the recipient, the purpose, and an expiration or revocation condition. HIPAA’s Privacy Rule requires authorization language to be specific and understandable; New Mexico law may add protections for particular records. The completed authorization can be signed electronically when the parties satisfy ESIGN, UETA, and applicable HIPAA documentation requirements.
Who uses this release form?
Healthcare providers
Healthcare providers use the form to document a patient’s permission before releasing specified records to another provider, attorney, insurer, family member, or organization. The workflow should identify the patient, recipient, purpose, information categories, expiration, signature, and date so staff can evaluate the authorization before disclosure.
Patients and representatives
Patients and representatives use the form to direct protected health information to named recipients. Medical practices, health plans, and release-of-information teams can send the authorization through signNow, capture the signature, and retain an auditable copy without changing the disclosure scope.
Business types that use this form
The form serves healthcare organizations that need documented patient permission before disclosing specified protected health information.
Solo behavioral-health practices can send a narrowly scoped patient authorization, collect the patient’s signature remotely, and retain the completed release with its audit trail. Regional medical groups can standardize authorization templates for records teams while routing each New Mexico release to the correct patient and recipient. Enterprise health systems can connect release workflows with business systems, apply signer authentication, and preserve authorization records under their HIPAA retention policy.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Key features for this authorization
signNow combines document preparation, controlled signing, signer verification, and audit evidence for New Mexico HIPAA Release Form workflows.
Field detection
Upload the New Mexico authorization, then review detected fields before adding signature, date, and recipient controls.
Remote signing
Send a patient-specific signing request by email or a controlled signing link without rewriting the authorization.
Audit trail
Capture signer actions, timestamps, and completion evidence alongside the signed release for later review.
Signer verification
Use SMS-based verification when the release contains sensitive protected health information and stronger attribution is needed.
Secure retention
Retain a reproducible copy of the authorization and completion record under the applicable HIPAA policy.
System connections
Connect the workflow to healthcare operations through supported CRM, ERP, and cloud-storage integrations.
How the release form works
The New Mexico authorization moves from document preparation to verified consent and controlled retention in four steps.
Upload form: Upload the New Mexico authorization and confirm its patient, recipient, purpose, and expiration fields. Check fields: Review detected fields and add missing signature, date, and authorization controls. Send for signing: Send the authorization to the patient or representative through a verified signing request. Store record: Store the signed release with its certificate of completion and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete the form in signNow
Use this sequence to prepare, sign, and preserve a New Mexico HIPAA Release Form without changing its disclosure limits.
Upload form:
Upload the completed New Mexico HIPAA Release Form. Review details:
Check patient, recipient, purpose, and expiration details. Add fields:
Place signature, date, and consent fields. Send request:
Send the release to the named signer. Save record:
Download the signed authorization and audit trail.
Recommended workflow setup
Configure the authorization around named recipients, limited disclosures, verified signers, and a reproducible record of consent.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP address, and actions |
| Document retention | Keep six years under HIPAA 45 CFR 164.530(j) |
| Encryption | Use TLS 1.2/1.3 and AES-256 protection |



Platform requirements for signing
A New Mexico HIPAA Release Form can be prepared in signNow using Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow mobile apps support iOS and Android, while secure connections use TLS 1.2/1.3.
Browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Secure connection TLS 1.2/1.3 connection required
Healthcare organizations should manage access through approved devices and accounts, confirm that signers can open and reproduce the electronic record, and configure authentication appropriate to protected health information. API, SSO, and certificate requirements depend on the organization’s deployment and selected signNow plan.
Security and data protection
HIPAA safeguards:
Transit encryption:
Stored encryption:
Security assurance:
Security certification:
Privacy controls:
What the audit trail records
A signNow audit trail documents the technical evidence surrounding this authorization without expanding the information the patient permitted the recipient to receive.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Log events:
Export evidence:
Privacy and disclosure pitfalls
Including an entire medical record instead of narrowly identifying the information authorized for disclosure creates unnecessary privacy exposure. Leaving the recipient, purpose, or expiration date unclear can prevent a covered entity from confirming valid authorization. Sending a release through an unverified address can weaken evidence that the named patient actually consented. Sharing the completed authorization with unauthorized staff can expose protected health information beyond the stated disclosure purpose.
Retention and record-keeping practices
Retain the authorization, signing evidence, and disclosure scope together so a New Mexico healthcare organization can demonstrate what the patient approved.
Apply the six-year HIPAA retention rule
Export the audit trail with the release
Match disclosure scope to authorization
Confirm the HIPAA business associate agreement
Legal standing and evidence
An electronically signed New Mexico HIPAA Release Form can provide evidence of intent, signer attribution, consent, and record integrity when the parties satisfy ESIGN and applicable New Mexico electronic-transactions law. HIPAA authorization requirements still apply, and electronic signing does not make wills, court orders, or family-law decrees eligible for electronic execution.

Questions about signing and compliance
These answers address specific signing, HIPAA, retention, and access questions for New Mexico HIPAA Release Form workflows.
signNow’s HIPAA compliance requires a business associate agreement. Before sending protected health information, confirm that the covered entity has completed the required BAA and configured access, authentication, retention, and disclosure procedures for this New Mexico authorization.
The Business plan includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2, and GDPR controls. HIPAA-specific deployment should be checked against the BAA requirement and the organization’s selected plan and configuration.
A signature alone does not define HIPAA authorization scope. Identify the patient, recipient, information categories, purpose, expiration, and revocation terms on the form before placing signNow fields or sending it for signature.
Use signNow’s audit trail and certificate of completion to preserve signer actions, timestamps, and completion evidence. Keep those records with the signed authorization and apply the six-year HIPAA documentation rule in 45 CFR §164.530(j).
If the signer cannot open the request, verify the email address, resend the invitation, or use a controlled signing link. SMS OTP can add a second factor when the organization requires stronger signer attribution for protected health information.
Electronic signing does not override HIPAA authorization requirements or exclusions under ESIGN. Wills, court orders, and family-law decrees remain outside ordinary electronic-signature treatment, while this health-information authorization requires accurate scope and consent.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.