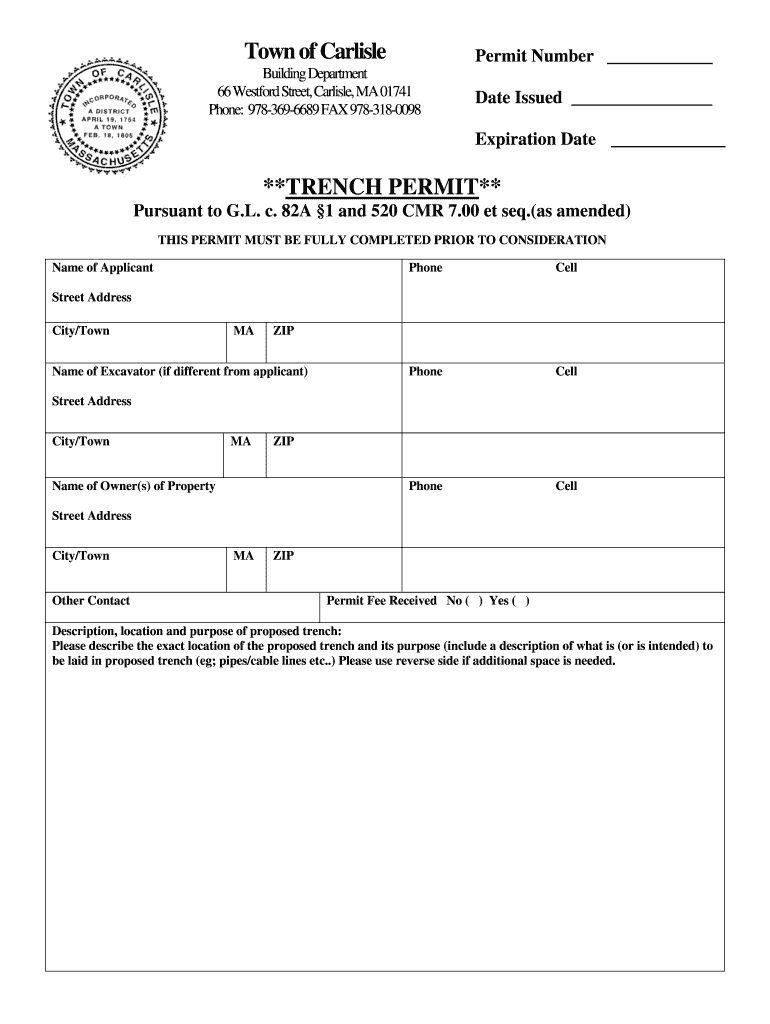
Trench Application Form
Accelerate Trench Application 0 creation, negotiation, and execution with airSlate SignNow.
What the Trench Application Form does
The Trench Application Form records project information and approvals connected with excavation or trench work. In signNow, a sender uploads the form, reviews detected fillable fields, assigns fields to the responsible people, and sends it for completion and signature. Signers can review the populated record online, sign from a supported device, and receive a completed copy. signNow stores the signed document with an audit trail showing signer activity, timestamps, and completion history. Apply any additional safety, construction, or state requirements governing the underlying project.
Business types using trench applications
Trench Application Form workflows help field contractors, construction offices, and enterprise project teams collect consistent information and preserve signed records.
A solo excavation contractor can complete site-specific trench applications from a mobile device, capture the required project details, and send the record for electronic signature without returning to an office. A construction office can route trench applications among estimators, project managers, and clients, preserving the completed form and audit trail for project administration and contract documentation. An enterprise construction organization can standardize trench application templates, control access by team, and connect signed records with systems such as Procore, NetSuite, or Microsoft 365.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses the trench application
Construction contractors
Construction contractors use the Trench Application Form to document excavation-related project information, identify responsible parties, and obtain signatures before retaining the completed record with its audit trail.
Project administrators
Project administrators use the form to standardize submissions across jobs, route approvals to designated signers, and keep completed applications available for project records and later review.
How the trench form workflow works
The signNow workflow moves the Trench Application Form from an uploaded document to a signed, auditable project record.
Upload form: Upload the Trench Application Form PDF. Map fields: Review detected fields and assign recipients. Send request: Send the prepared application for signatures. Retain record: Store the completed form and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Steps to complete the trench form
Use this sequence to prepare, route, sign, and retain a Trench Application Form in signNow.
Upload form:
Upload the completed form PDF. Detect fields:
Let signNow detect fillable fields. Assign signers:
Assign fields to each signer. Send form:
Send the signing request. Store copy:
Download the completed record.
Recommended trench form workflow settings
Configure the Trench Application Form around signer identity, signature evidence, protected storage, and the retention rule that applies to its specific business record.
| Setting | Recommendation |
|---|---|
| Signer authentication method | Email verification with SMS OTP |
| Electronic signature type | Typed or drawn signature |
| Audit trail handling | Retain completion certificate with signed PDF |
| Document retention period | Apply the governing record rule |
| Encryption configuration | AES-256 at rest and TLS in transit |
Security for signed trench records
Data at rest:
Data in transit:
Security assurance:
Information security:
Privacy compliance:
Signature compliance:
How the audit trail records signing
The audit trail connects each Trench Application Form action to a signer, time, document state, and retrievable completion record.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log actions:
Export evidence:
Best practices for trench applications
Accurate field review, controlled delivery, complete audit evidence, and documented retention help keep each Trench Application Form usable after signing.
Verify project details before sending
Preserve the complete signing record
Limit access to project personnel
Apply the governing retention rule
Legal standing for business records
A Trench Application Form signed electronically can be admissible when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains reproducible under ESIGN and applicable state law. Those rules do not cover wills, codicils, testamentary trusts, certain court orders, or specified family-law documents.

Documents requiring extra formalities
Real-estate deeds
Wills and codicils
Court orders
Family-law decrees
Privacy pitfalls when sharing trench forms
Personal identifiers placed in a Trench Application Form can be exposed when completed files are emailed without access restrictions. A signer may complete the form without documented electronic-record consent, weakening evidence that the transaction was authorized. Shared links can expose a form to an unintended person when recipient identity checks are not configured. Unrestricted downloads can leave signed forms and audit trails outside the organization’s approved retention and access controls.
Troubleshooting trench application signing
Resolve field, signer, compliance, and plan questions before relying on a completed Trench Application Form as a project record.
Upload the Trench Application Form as a PDF, then inspect signNow’s detected fields before sending. Detection can identify field locations, but the sender remains responsible for confirming labels, recipients, required fields, and signing order.
The Business plan includes templates and audit trails, while Business Premium adds bulk send. Select a plan based on the number of trench applications and routing pattern rather than assuming every plan includes bulk delivery.
Email signing is not itself enough to establish evidentiary value. Under ESIGN and UETA, preserve intent, electronic-record consent where required, signer attribution, and a reproducible signed record with its audit trail.
If the application contains protected health information, signNow lists HIPAA compliance with a required BAA. Confirm that the organization has the BAA and applies appropriate access, retention, and disclosure controls.
For a consumer-facing electronic record, ESIGN requires disclosure of the right to receive paper, access to the electronic format, and a withdrawal process under 15 U.S.C. §7001(c). Configure the workflow accordingly.
If a signer cannot open the request, verify the email address, resend the invitation, or provide a controlled signing link. For stronger attribution, add SMS authentication or another available signer-verification method.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.