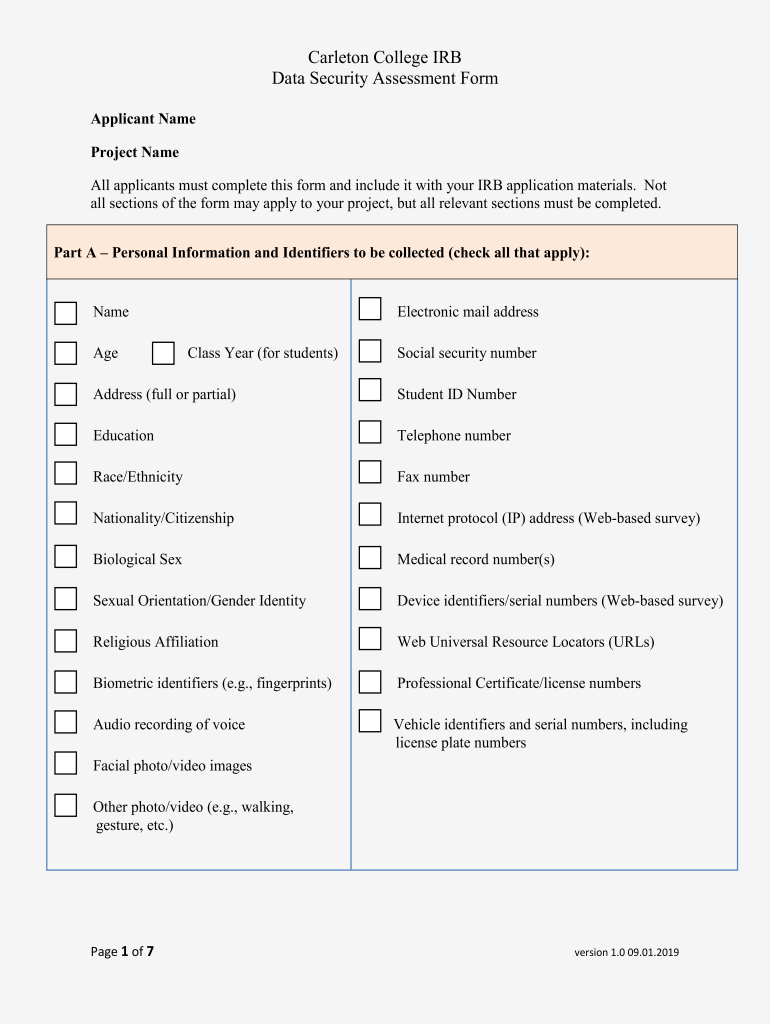
Data Security Assessment Form Institutional Review Board
Use a Data Security Assessment Form Institutional Review Board template to make your document workflow more streamlined.
What this institutional review board assessment does
The Data Security Assessment Form Institutional Review Board records whether a research project, system, or vendor protects the data used in an institutional review board submission. It typically organizes answers about collection, storage, access, transmission, disclosure, retention, incident response, and responsible personnel. The completed assessment gives reviewers a structured basis for identifying safeguards and unresolved risks before approving or continuing a study. In signNow, an uploaded form can be mapped to fillable fields, routed to designated reviewers, signed electronically, and retained with an audit trail showing the completion history.
Features that support board review
The workflow keeps assessment answers, reviewer actions, signatures, and supporting evidence together so institutional review board teams can evaluate data safeguards consistently.
Field placement
Upload the Data Security Assessment Form Institutional Review Board and place fields for assessment answers, reviewer initials, dates, approvals, and signatures without recreating the document.
Role routing
Route the completed assessment to institutional reviewers in a defined order, keeping investigator, security, privacy, and board approvals visible in one workflow.
Audit trail
Capture timestamps, signer identity, actions, and document history so the board can review how the assessment was completed and when each approval occurred.
Reusable templates
Use controlled templates for recurring studies or vendor assessments while preserving required questions and reducing omissions across submissions.
Data protection
Protect research and security information with encryption, access controls, and compliance features aligned with the organization’s handling requirements.
Record storage
Store the completed assessment and certificate of completion together, giving authorized reviewers a retrievable record for governance and later review.
How this assessment workflow works
Complete the Data Security Assessment Form Institutional Review Board in signNow by preparing the document, checking its fields, routing it to responsible reviewers, and retaining the completed record.
Upload form: Upload the assessment document. Review fields: Auto-detect and verify fillable fields. Route assessment: Assign reviewers and approval roles. Archive record: Store signed copies with audit evidence.
Steps to complete this assessment online
Prepare the Data Security Assessment Form Institutional Review Board in signNow, verify its field mapping, route it to the people responsible for each section, and retain the signed evidence.
Upload document:
Upload the board assessment PDF. Check fields:
Check detected fields and add missing responses. Assign roles:
Assign investigators, reviewers, and approvers. Send workflow:
Send the assessment and monitor completion. Store records:
Download the signed assessment and audit trail.
Security controls for this assessment
Data at rest:
Data in transit:
Security certification:
Security standard:
Healthcare safeguards:
Privacy compliance:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the assessment audit trail records
The audit trail documents the technical history of the Data Security Assessment Form Institutional Review Board rather than repeating the steps used to create or send it.
Authenticate signer:
Timestamp actions:
Hash document:
Seal record:
Log activity:
Export evidence:
Mobile options for assessment workflows
The signNow iOS and Android apps support completing the Data Security Assessment Form Institutional Review Board from supported mobile devices. Users can capture source pages with a camera and continue signing when offline.
iPhone app iOS 15 or later Android app Android 10 or later Mobile workflow Offline signing and camera capture
Organizations should manage iOS 15 or later and Android 10 or later devices through their mobile-security policies. Confirm offline-storage controls, camera permissions, SSO provisioning, API access, and certificate or long-term-validation requirements before deploying the assessment workflow to reviewers.



Recommended setup for this assessment
Configure the Data Security Assessment Form Institutional Review Board workflow around identified reviewers, documented evidence, controlled access, and the institution’s approved research-record policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture timestamps, identity, IP, and actions |
| Document retention | Follow institutional research-record policy |
| Encryption | TLS 1.2/1.3 and AES-256 |
Best practices for board assessments
Use documented roles, source evidence, controlled templates, and retained audit records to make each Data Security Assessment Form Institutional Review Board submission reviewable and defensible.
Validate answers against source evidence
Separate completion and approval roles
Control template revisions
Archive the assessment record
Challenges when completing this assessment
Security responses may omit data locations, retention practices, subprocessors, or access controls, leaving institutional reviewers without evidence for an informed decision. A completed assessment can expose research-system details or personal information when broad sharing permissions are applied to the signed document. Unclear signer roles can make it difficult to determine whether an investigator, vendor, security officer, or board representative approved each response. Failure to preserve the final assessment with its audit trail can weaken the institution’s ability to reconstruct review history during an audit or inquiry.
Legal standing and practical value
A completed Data Security Assessment Form Institutional Review Board creates a reviewable record of data-protection decisions, assigned responsibilities, and approvals. For U.S. transactions, ESIGN, 15 U.S.C. ch. 96, and UETA generally support electronic signatures when intent, consent, attribution, and reproducible records are demonstrated; exclusions such as wills and court filings still apply.

Risks of an incomplete assessment
Review delay
Evidence gap
Privacy exposure
Compliance dispute
Troubleshooting this assessment workflow
These answers address field mapping, reviewer routing, protected information, audit evidence, plan selection, and U.S. electronic-signature requirements for this institutional review board assessment.
Upload the original PDF again, then inspect every detected field before sending. signNow supports templates and fillable fields, but a reviewer should confirm that security questions, attachment areas, initials, dates, and signature fields match the institutional review board’s actual form.
Use signNow role assignments and ordered routing to separate the investigator’s responses from security, privacy, and board approval. The sender should verify each recipient’s email and permission before delivery so one reviewer cannot unintentionally edit another reviewer’s section.
Business pricing is $8/user/month when billed annually, and the Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps. Business Premium adds bulk send and kiosk mode; Enterprise adds advanced signer authentication and advanced fields.
signNow states that HIPAA compliance requires a business associate agreement. If the assessment contains protected health information, confirm that the organization has the required BAA and configure access, authentication, and retention controls through its compliance process.
The signNow audit trail records signing activity, timestamps, signer information, and document history. Export the completed assessment and audit trail together, then apply the institution’s approved retention policy rather than assuming a universal period for this form.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention requirements are satisfied. For consumer-facing records, review the ESIGN disclosure requirements in 15 U.S.C. §7001(c) before using electronic delivery.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.