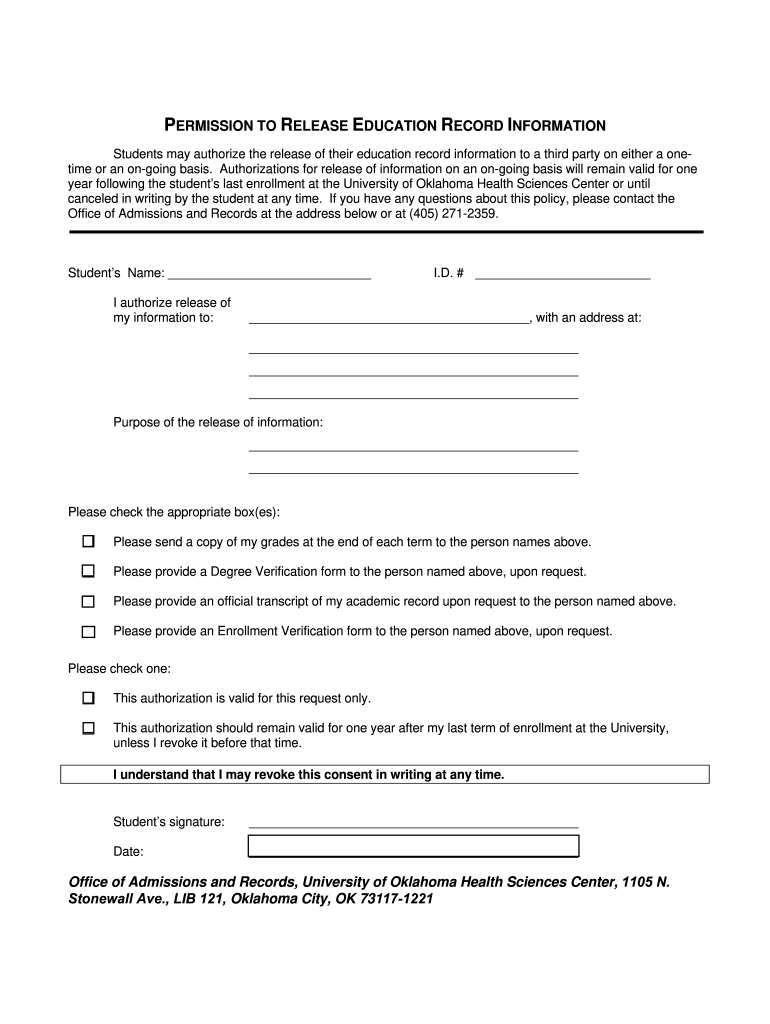
Authorization Forms University Of Oklahoma
Use a Authorization Forms University Of Oklahoma template to make your document workflow more streamlined.
What this authorization form does
Authorization Forms University Of Oklahoma is a permission record used to document who may receive information or perform a defined action for a University of Oklahoma process. The exact scope depends on the issuing office and the form’s wording. A completed copy should identify the signer, recipient, purpose, information or action covered, and any expiration or revocation terms. signNow can upload the document, detect fillable fields, route signatures, and retain the completed PDF with its audit trail. Review FERPA, institutional policy, and applicable state or federal law before relying on the authorization.
Documents and audiences covered
Students and families
Use the form for student-record permissions, transcript requests, enrollment-related authorizations, or other University of Oklahoma processes where the responsible office specifies a recipient and purpose. Confirm whether FERPA or another privacy rule applies before collecting a signature.
Administrative users
Departments, clinics, vendors, and employees can use the form for operational permissions, disclosures, or service-related approvals. Document the exact scope and keep the signed record with its audit trail according to University of Oklahoma policy and applicable law.
How this authorization workflow works
The workflow keeps the University of Oklahoma document intact while adding controlled fields, signer routing, electronic signatures, and completion evidence.
Upload document: Upload the university authorization PDF. Detect fields: Auto-detect and verify fillable fields. Route for signing: Send assigned fields to each signer. Preserve record: Store the signed PDF with its audit trail.
Complete the authorization form online
Use signNow to upload the University of Oklahoma authorization form, verify its fields, route it to the named signer, and preserve the completed record.
Upload form:
Upload the University of Oklahoma authorization document. Check fields:
Review detected fields and add missing fields. Assign signers:
Assign each field to the correct signer. Send form:
Send the authorization through signNow. Store record:
Store the completed record and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the authorization audit trail works
For an Authorization Forms University Of Oklahoma record, signNow documents identity, timing, integrity, and retrieval events separately.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper-evident sealing:
Event logging:
Trail export:
Recommended authorization workflow setup
Configure the authorization form around signer identity, explicit consent, document integrity, and University of Oklahoma recordkeeping requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enabled for every authorization |
| Document retention | Follow University of Oklahoma policy |
| Encryption | TLS 1.2/1.3 and AES-256 |
Security controls for authorization records
Data in transit:
Data at rest:
Security reporting:
Information security:
Health information:
Electronic signatures:



Platform requirements for signing
Use a current version of Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow supports mobile access through iOS and Android applications, with encrypted connections using TLS.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile access iOS and Android mobile apps
University of Oklahoma offices should manage browser updates, device access, and account permissions through their institutional policy. Enterprise deployments may also require API access, SSO provisioning, managed devices, and documented retention controls for authorization records and audit trails.
Recordkeeping practices for authorization forms
Reliable records management connects the completed authorization, its audit trail, the governing office policy, and access controls.
Export the signed form and audit trail
Confirm the applicable retention schedule
Archive records with controlled access
Review scope before final signature
Key performance indicators that demonstrate SignNow's proven track record.
Authorization form troubleshooting and FAQs
These answers address field setup, signer access, privacy requirements, plan selection, and legal limits for this University of Oklahoma authorization workflow.
Upload the University of Oklahoma authorization document, then review signNow’s detected fields before sending. Add missing signer, date, initials, or acknowledgment fields manually and confirm each field belongs to the correct person.
The Business plan includes legally binding eSignatures, templates, and audit trails at $8/user/month when billed annually. Business Premium adds bulk send at $15/user/month; select the plan based on the number and complexity of authorization requests.
Use the form’s exact recipient, purpose, scope, and expiration language. For student records, confirm whether FERPA applies and obtain any required institutional consent before sending; an audit trail cannot cure missing substantive authorization language.
If a signer cannot access the email, verify the address, resend the invitation, or provide a controlled signing link. Use SMS authentication when identity assurance requires more than email access, and document any office-approved alternative process.
signNow encrypts data in transit with TLS 1.2/1.3 and at rest with AES-256. HIPAA compliance requires a BAA and applies only when the workflow genuinely handles protected health information, not merely because the form is used at a university.
A signed authorization can support evidence of intent, attribution, and record integrity under ESIGN and UETA when applicable. Wills, court orders, and certain family-law documents remain statutory exclusions, so review the document’s actual legal purpose before relying on electronic signing.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.