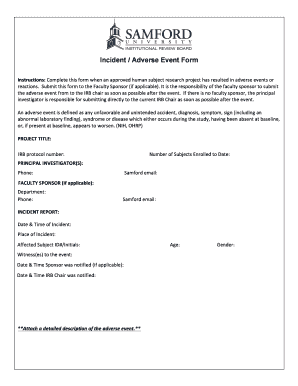
Incident Adverse Event Form
Use a Incident Adverse Event Form template to make your document workflow more streamlined.
What the incident form records
An Incident Adverse Event Form records what happened, when and where it occurred, who was involved, immediate actions, witness information, and review decisions. It gives a U.S. organization a structured record for investigating an adverse event rather than relying on disconnected emails or handwritten notes. With signNow, a sender uploads the form, adds or confirms fields, routes it to witnesses and reviewers, collects electronic signatures, and stores the completed document with an audit trail. If the record contains protected health information, the organization must apply its HIPAA policies and access controls.
Who uses this incident form
Healthcare teams
Healthcare teams use this form to document adverse events, capture factual details, and route completed records for review with an auditable signature history.
Compliance teams
Safety, compliance, and operations teams use it to standardize incident reporting, preserve witness information, and coordinate follow-up actions across locations.
Features for incident reporting workflows
signNow connects the Incident Adverse Event Form’s factual reporting fields with controlled signing, routing, auditability, and record handling.
Field placement
Upload the Incident Adverse Event Form, identify its blanks, and add text, date, checkbox, and signature fields without rebuilding the document.
Signer routing
Send each incident record to the assigned reviewer or signer in a defined order, reducing missing approvals and unclear responsibility.
Audit trail
Capture signing activity, timestamps, and document history in an audit trail that supports internal review of the reported incident.
Reusable template
Use a reusable template for recurring incident reports while preserving fields for event date, location, description, witnesses, and corrective action.
Mobile signing
Collect signatures from desktop or mobile devices when supervisors, witnesses, or reviewers work away from a central office.
Record storage
Store the completed form with its audit trail so authorized teams can retrieve the record during investigations, audits, or follow-up reviews.
How the incident form works
The signNow workflow turns the Incident Adverse Event Form into a controlled record from upload through review, signature, and audit-trail storage.
Upload: Upload the Incident Adverse Event Form. Prepare fields: Detect and place required fields. Route: Send it to witnesses and reviewers. Complete: Store signatures with the audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete the incident form online
Use this sequence to prepare, route, sign, and preserve an Incident Adverse Event Form in signNow.
Upload form:
Upload the completed Incident Adverse Event Form. Add fields:
Add signature, date, text, and checkbox fields. Assign recipients:
Assign witnesses, reviewers, and signing order. Send form:
Send invitations or create a signing link. Store record:
Review signatures and save the audit trail.
Platform requirements for incident forms
Complete and sign the Incident Adverse Event Form in a current Chrome, Firefox, Safari, or Edge browser on Windows or macOS. signNow also provides mobile apps for iOS and Android, allowing reviewers to access assigned incident records away from a desk.
Browsers Chrome, Firefox, Safari, and Edge Operating systems Windows, macOS, iOS, and Android Mobile apps signNow mobile apps for iOS and Android
Organizations should manage access through approved devices, role-based permissions, and documented retention procedures. Teams connecting incident workflows to other systems should confirm the required signNow plan, API access, SSO provisioning, and any certificate, authentication, or HIPAA configuration needed for the information collected.
Security for incident form records
Transport encryption:
Stored data:
Security assurance:
Management standard:
Healthcare safeguards:
Signer verification:



Best practices for incident form completion
Accurate fields, controlled routing, restricted access, and paired record storage make an Incident Adverse Event Form easier to review and defend.
Define required incident fields
Route the form to accountable reviewers
Restrict access to sensitive records
Preserve the signed record
Privacy challenges in incident reporting
Including patient names, medical details, or witness contact information in a broadly shared copy can expose personal data beyond the incident-review team. Sending an Incident Adverse Event Form to witnesses without explaining electronic-record consent can weaken evidence that each person intended to sign electronically. Using a shared account or unrestricted signing link can make signer attribution difficult when multiple employees access the same incident record. Copying narrative details into email notifications can disclose sensitive incident facts outside the controlled document and audit-trail workflow.
What the incident audit trail records
The audit trail documents signing events and record history separately from the Incident Adverse Event Form’s factual narrative.
Signer authentication:
Timestamp capture:
Activity details:
Document history:
Completion evidence:
Audit retrieval:
Incident form troubleshooting questions
Resolve field, signing, authentication, and retention questions before distributing an Incident Adverse Event Form through signNow.
Upload the original Incident Adverse Event Form as a PDF or supported document, then use signNow’s editor to place fields. If automatic field detection does not identify every blank, add signature, date, text, and checkbox fields manually before sending.
The signNow Business plan costs $8/user/month with annual billing and includes legally binding eSignatures, templates, audit trails, and mobile apps. Business Premium adds bulk send at $15/user/month annually; Enterprise adds advanced signer authentication at $30/user/month.
For an Incident Adverse Event Form containing protected health information, signNow states that HIPAA compliance requires a business associate agreement. Confirm the BAA and configure access controls before collecting or sharing PHI.
A completed form can be supported by signNow’s audit trail, which records signing activity such as timestamps, IP information, and action history. Preserve the signed document and audit trail together under your organization’s record policy.
If a signer cannot open the email, generate a shareable signing link or resend the invitation from signNow. For stronger attribution, add SMS authentication or another available signer-authentication method before resending.
An electronic signature for this business record generally depends on intent, consent, attribution, and the ability to retain and reproduce the record under ESIGN and applicable state law. Consumer-facing workflows may also require the disclosure in 15 U.S.C. §7001(c).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.