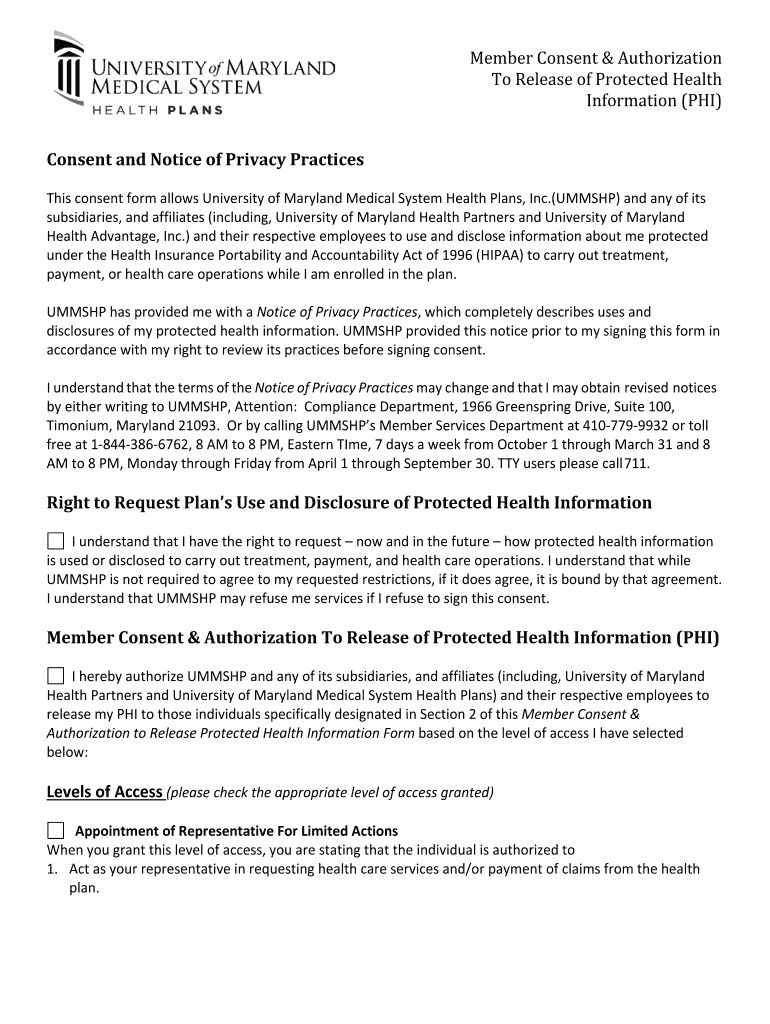
Umha HIPAA Privacy Consent & Auth Form University Of Maryland
Use a PDF UMHA HIPAA Privacy Consent & Auth Form University Of Maryland template to make your document workflow more streamlined.
What this authorization form does
The Umha HIPAA Privacy Consent & Auth Form University Of Maryland records a patient’s consent and authorization for specified uses or disclosures of protected health information. In signNow, an administrator uploads the University of Maryland document, reviews automatically detected fillable fields, assigns patient and organizational signers, and sends the form electronically. Each signer reviews the stated information, recipient, and purpose before signing. The completed document and audit trail provide an accessible record, while HIPAA safeguards, institutional policy, and applicable electronic-signature law continue to govern its use.
Who uses this authorization form
Healthcare providers
Healthcare providers and University of Maryland-affiliated clinics use the form to capture patient consent, specify authorized disclosures, assign recipient roles, and preserve completed records containing protected health information.
Patients and representatives
Patients and authorized representatives review the stated purpose, information scope, recipient, and expiration details before signing the University of Maryland authorization electronically.
Business types using this form
Healthcare organizations use this form to capture patient permission, define authorized disclosures, and retain evidence of the completed authorization workflow.
A solo Maryland therapist can use the form to document a patient’s HIPAA consent and authorization before sharing protected health information with a named recipient. A university-affiliated clinic can route completed consent and authorization forms to patients, providers, and records staff while preserving signer identity and an auditable completion record. A multi-site healthcare enterprise can standardize the University of Maryland form through reusable templates, controlled access, and centralized audit trails for recurring patient authorization workflows.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Legal standing of the authorization form
A completed University of Maryland HIPAA consent and authorization form can provide evidence of patient intent when the signer, consent, attribution, and retained record are properly documented. ESIGN and applicable state electronic-transaction law generally recognize electronic signatures, but HIPAA privacy duties and any required institutional procedures still apply.

How this authorization workflow works
The workflow converts the University of Maryland authorization form into a controlled electronic signing process while preserving field assignments and completion evidence.
Upload form: Upload the University of Maryland PDF Check fields: Review detected fields and add missing authorization fields Set recipients: Assign patient and organization recipients Complete record: Collect signatures and preserve the completed audit trail
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features for this authorization workflow
signNow applies field detection, recipient roles, audit evidence, mobile signing, and HIPAA safeguards to the University of Maryland authorization process.
Field detection
Auto-detected fields help identify places for patient information, authorization details, dates, and signatures before the University of Maryland form is sent.
Role assignment
Recipient roles keep patient and organizational signature responsibilities separate, reducing attribution errors during the authorization process.
Reusable template
Reusable templates preserve the University of Maryland form structure for recurring patient authorization workflows without recreating fields each time.
Audit evidence
Audit trails record signing activity and completion evidence for internal review of the authorization record.
Mobile signing
Mobile apps allow authorized staff and patients to review and sign the form from supported devices when the workflow permits.
HIPAA safeguards
HIPAA compliance is available with a required business associate agreement for workflows involving protected health information.
Security for protected health information
Encryption at rest:
Transport encryption:
Independent assurance:
Security certification:
Health data compliance:
Privacy controls:



Recommended workflow configuration
Configure the University of Maryland authorization form around signer identity, protected health information, audit evidence, and the applicable retention obligation.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enabled for every completed form |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 |
Privacy and disclosure pitfalls
Including a patient’s full medical details in the signed PDF can expose more protected health information than the authorization requires. Leaving the recipient, purpose, or information scope blank may make the authorization unclear for the organization processing disclosure. Assigning the patient’s signature field to the wrong recipient can undermine attribution and create a disputed consent record. Sharing a completed authorization through unrestricted links can expose protected health information to unintended viewers.
Inside the authorization audit trail
The audit trail records who interacted with this form, when each action occurred, and how the completed record can be reviewed after signing.
Authenticate signer:
Capture timestamp:
Record document integrity:
Seal audit history:
Deliver final copy:
Export audit trail:
Retention schedule for signed authorizations
HIPAA-covered entities must apply the federal six-year documentation rule and check whether University of Maryland or state policy requires longer preservation.
Six years from creation
Six years from last effective date
Longer rule if applicable
Retain completion evidence
Reassess changed authorizations
Best practices for this form
Accurate scope, signer assignment, retention, and contractual safeguards help keep the University of Maryland authorization record usable and privacy-conscious.
Limit the disclosure scope
Check signer assignments
Retain the complete record
Confirm the HIPAA agreement
Troubleshooting the University of Maryland form
These answers address field detection, signer assignment, HIPAA safeguards, delivery, bulk sending, and retention for this authorization workflow.
Upload the University of Maryland form as a PDF, then check signNow’s detected fields before sending. If a field is missing, add the appropriate text, date, checkbox, or signature field manually and confirm every required authorization element remains visible.
The Business plan includes legally binding eSignatures and audit trails. For HIPAA workflows, signNow states that HIPAA compliance requires a business associate agreement. Confirm the applicable BAA and configure access controls before sending forms containing protected health information.
Use signNow’s recipient roles and field assignments to identify the patient, authorized recipient, and organizational representative. Review the completed PDF and audit trail to verify that each required person signed the intended fields.
If a signer cannot open the email, resend the invitation or generate a signing link. For stronger identity assurance, use available authentication controls such as SMS-based verification where configured for the account and workflow.
The Business Premium plan adds bulk send, which is useful when the same University of Maryland authorization form must reach many patients. Review each recipient’s assigned fields before transmission because bulk delivery does not replace privacy review.
After completion, signNow records actions in an audit trail and provides the signed document and completion evidence. Retain the record for six years from creation or the last effective date when HIPAA’s rule applies, under 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.