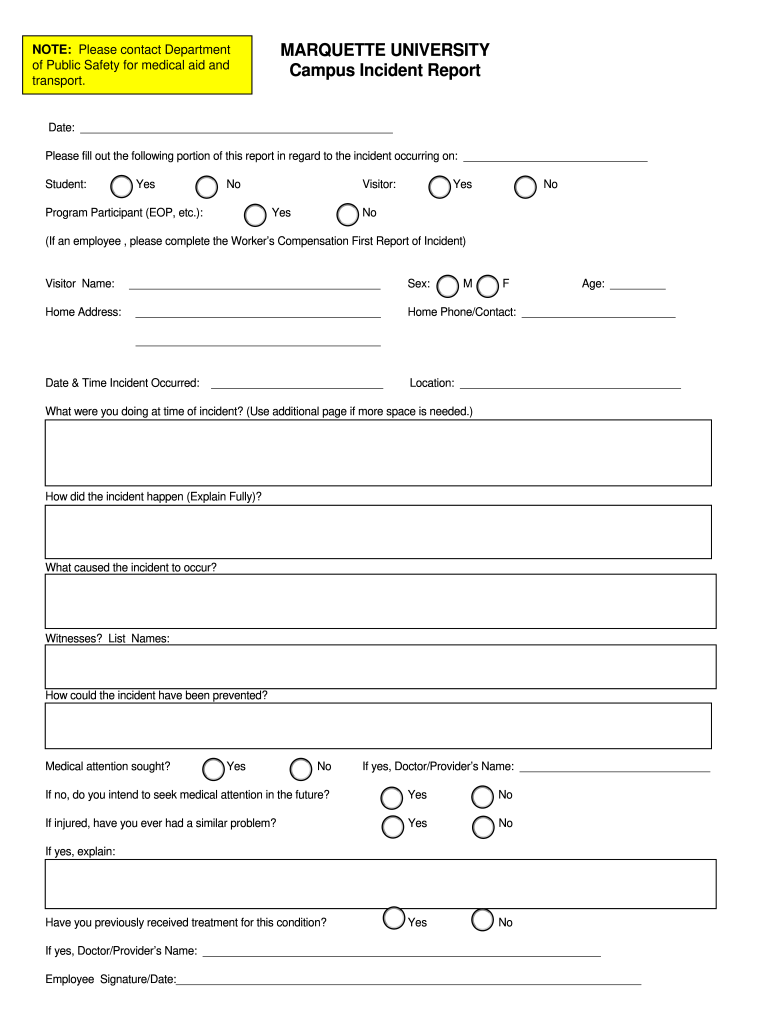
Non Employee Incident Report Non Form
Use a Fill Fillable Non Employee Incident Report Non template to make your document workflow more streamlined.
What this incident report does
The Non Employee Incident Report Non Form records an incident involving someone who is not an employee, such as a contractor, visitor, vendor, or other outside party. It typically captures the event description, people involved, location, date, facts, corrective actions, and signatures, but the exact fields depend on the source template. Upload the document to signNow, review detected fillable fields, add missing fields, route it to the responsible signer, and retain the completed report with its audit trail. No federal filing deadline or issuing agency is identified for this form name.
Who uses this incident report
Workplace operations
Supervisors, safety coordinators, and human resources teams can use the report to document incidents involving contractors, visitors, vendors, or other non-employees. They can collect the relevant facts, identify the signer, and preserve the completed record for internal review without circulating paper copies.
Industry teams
Healthcare, construction, property, and public-sector organizations may adapt the report for incidents involving people who are not employees. The responsible team should limit collected information, confirm any industry-specific reporting rule, and retain the signed document under its records policy.
How the incident report workflow works
Complete the report, route it to the appropriate signer, and preserve the signed record with signNow’s audit trail.
Upload the form: Upload the completed Non Employee Incident Report Non Form to signNow. Check fields: signNow detects fillable areas and lets you add missing fields. Send for signature: Send the incident report to the required signer by email or link. Archive securely: Store the signed report with its audit trail and completion record.
Recommended incident report setup
Configure the report workflow around signer identity, an evidentiary audit trail, secure transmission, and an approved retention policy.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP address, and actions |
| Document retention | Retain according to organizational policy |
| Encryption | TLS in transit and AES-256 at rest |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Features for completing the incident report
signNow connects the report’s fillable fields, signer routing, authentication, and recordkeeping into one documented electronic workflow.
Field placement
Upload the Non Employee Incident Report Non Form and place signature, date, initials, and text fields without rebuilding the document.
Signer routing
Route the report to a named signer by email or signing link while keeping the requested action and recipient clear.
Audit trail
Capture signer actions, timestamps, and document history in an audit trail that supports later review.
Reusable template
Use templates when the same incident-report structure recurs, reducing inconsistent field placement across submissions.
Mobile signing
Complete the report from a desktop or mobile device when field personnel cannot return to the office.
Secure records
Keep the completed report and completion record together for internal review, investigations, or authorized disclosure.
What the audit trail records
For a Non Employee Incident Report Non Form, the audit trail documents who acted, when they acted, and how the completed record was preserved.
Authenticate signer:
Capture timestamp:
Record document history:
Seal completion:
Log workflow actions:
Export evidence:
Privacy and disclosure pitfalls
Including a non-employee’s unnecessary personal details can expose sensitive information in every distributed copy of the signed report. Sending the report before obtaining electronic-record consent can weaken evidence that the signer agreed to use an electronic document. Using an unrestricted signing link may allow an unintended person to access or complete the incident report. Failing to preserve the completion certificate and audit trail can make signer identity, timing, and document history harder to establish.
Legal standing of the incident report
A signed Non Employee Incident Report Non Form may be used as business evidence when the signer demonstrates intent, consents to electronic records, can be identified, and the record is retained accurately. ESIGN, 15 U.S.C. ch. 96, and applicable UETA rules support electronic records, but they exclude wills, certain court orders, and specified family-law documents.

Security for signed incident reports
Stored data:
Data transmission:
Security assurance:
Information security:
Protected health data:
Electronic signatures:
Platform requirements for the incident report
Use signNow in Chrome, Firefox, Safari, or Edge on Windows or macOS. The signNow mobile apps support completing and signing the Non Employee Incident Report Non Form on iOS and Android devices.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile apps iOS and Android signNow apps
Organizations handling sensitive incident details should manage access through controlled accounts, role-based permissions, and documented retention procedures. Where the workflow involves protected health information, confirm that the required HIPAA business associate agreement and internal safeguards are in place before sending the report.
Recordkeeping practices for this report
Preserve the completed report as evidence while aligning retention, access, and disclosure decisions with the organization’s incident-records policy and applicable state or industry requirements.
Apply a documented retention schedule
Export evidence after completion
Minimize sensitive information before sending
Review the template before reuse
Incident report troubleshooting questions
These answers address field detection, signer access, electronic-signature evidence, protected information, plan selection, and record storage for this report.
Upload the original Non Employee Incident Report Non Form as a PDF or supported document file, then check every detected field before sending. signNow’s Business plan includes templates and audit trails, but field placement still requires human review for this report.
Confirm the signer’s email address, resend the invitation, or generate a new signing link. If stronger identity evidence is required, Business Premium adds relevant workflow options, while Enterprise adds advanced signer authentication according to the configured plan.
Electronic-signature enforceability depends on intent, consent, attribution, and reliable record retention under ESIGN and applicable UETA or New York ESRA rules. Preserve the completed report and its audit trail, and obtain consumer disclosures when required by 15 U.S.C. §7001(c).
A report containing protected health information requires an appropriate HIPAA workflow and business associate agreement. signNow identifies HIPAA compliance as requiring a BAA; confirm that agreement and organizational safeguards before sending health information.
Business is listed at $8 per user per month with annual billing, while Business Premium is $15 and Enterprise is $30. Product limits and invite allowances apply, so review the current plan terms before routing recurring incident reports.
Download or retain the signed report together with its completion record and audit trail. Do not rely on an email attachment alone; store the evidence in an access-controlled repository governed by the organization’s retention policy.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.