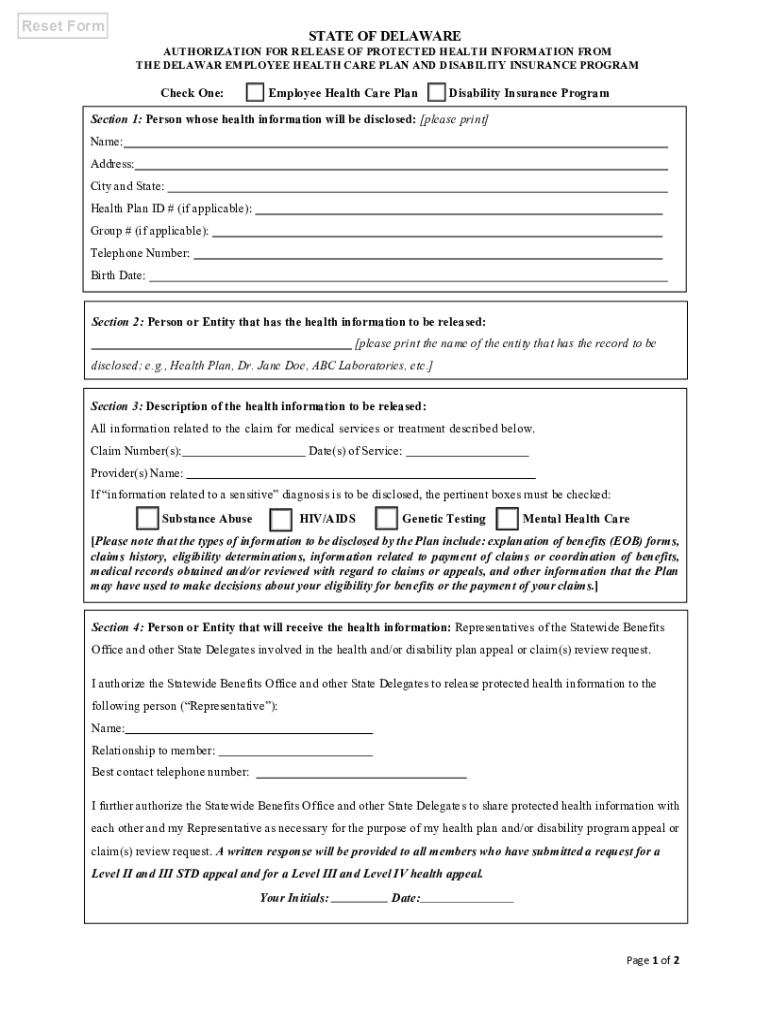
DE Authorization For Release Of Protected Health Information
Use a DE Authorization For Release Of Protected Health Information 0 template to make your document workflow more streamlined.
What this authorization does
A DE Authorization For Release Of Protected Health Information is a patient permission document that allows a covered healthcare provider to disclose specified medical information to a named recipient. It should identify the patient, the information or records covered, the recipient, the purpose, and an expiration date or event. The patient or authorized representative reviews and signs the authorization before disclosure. Under HIPAA, the provider must follow applicable authorization requirements and retain related documentation; 45 CFR §164.530(j) sets a six-year retention period for required records.
Who uses this authorization form
Healthcare providers
Healthcare providers use this authorization to document a patient’s permission before disclosing specified protected health information to a named person, insurer, attorney, or organization. Staff can prepare the form, identify the records and purpose, obtain the patient’s signature, and preserve the completed record with its audit trail.
Patients and representatives
Patients, legal representatives, and records departments use the authorization when a third party needs access to defined medical information. The workflow should identify the recipient, scope, purpose, expiration, and revocation process so the signed document matches the disclosure requested.
How the authorization process works
This authorization connects a patient’s consent with a defined disclosure request, so the recipient and permitted health information are documented before release.
Identify the patient: Use the patient’s legal name and contact details. Define the disclosure: Specify records, recipient, purpose, and expiration. Capture authorization: The patient reviews consent language and signs. Control disclosure: The provider releases only the approved information.
Complete this authorization in signNow
Use signNow to prepare the authorization, assign the patient’s fields, collect the signature, and preserve evidence of the completed disclosure consent.
Upload form:
Upload the DE authorization document. Check fields:
Review detected fields and add patient signature fields. Add signer:
Enter the recipient’s email address. Complete record:
Send, sign, and download the completed record.
Recommended setup for this authorization
Configure the authorization workflow around patient identity, protected information, auditability, and HIPAA recordkeeping obligations.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Patient electronic signature |
| Audit trail | Export certificate and activity log |
| Document retention | 6 years under 45 CFR §164.530(j) |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security controls for health information
HIPAA compliance:
SOC 2 Type II:
ISO 27001:
Transport encryption:
Storage encryption:
Electronic signatures:
Platform requirements for signing online
You can prepare and sign this authorization in signNow through Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android. Secure connections use TLS 1.2 or TLS 1.3 for data in transit.
Supported browsers Chrome, Firefox, Safari, and Edge Supported systems Windows, macOS, iOS, and Android Secure connection TLS 1.2 or TLS 1.3 connection
Healthcare organizations should use managed Windows, macOS, iOS, or Android devices with current browser security updates. Administrators should also evaluate API access, SSO provisioning, and retention controls before connecting authorization workflows to clinical or records-management systems.



Features for this authorization workflow
signNow combines field preparation, signer delivery, authentication, audit evidence, and export controls for a documented protected-health-information consent process.
Field detection
Upload the authorization and let signNow detect fillable areas before you verify and assign the patient’s signature, date, and initials fields.
Flexible delivery
Send the authorization by email or signing link, allowing the patient to review the exact disclosure language before signing.
Audit trail
Capture signer actions, timestamps, and document status in an audit trail that can accompany the completed authorization.
Signer authentication
Use email verification, SMS authentication, or advanced signer authentication according to the disclosure risk and organization policy.
Mobile signing
Complete the authorization from supported desktop browsers or signNow mobile apps when staff need to work away from a records office.
Record export
Export the signed authorization and completion evidence for controlled storage under the provider’s HIPAA retention policy.
Privacy and disclosure pitfalls
Including a recipient or record category too broadly can make the authorization unclear and increase the risk of disclosing information beyond the patient’s stated consent. Sending the completed authorization through an unapproved channel can expose protected health information or the patient’s identifying details. Failing to verify the patient or representative can weaken attribution and create uncertainty about whether valid consent was obtained. Giving every team member unrestricted access can expose the authorization and audit trail beyond the roles needed to process the disclosure.
Best practices for protected health information authorizations
Clear scope, controlled access, and complete records help providers document consent before disclosing protected health information.
Describe the permitted disclosure precisely
Review fields before sending the authorization
Match authentication to disclosure risk
Archive the complete authorization record
Retention rules for authorization records
Retain the authorization and supporting signing evidence according to HIPAA and applicable state or organizational requirements; the federal HIPAA period is six years.
Six years for HIPAA records
Not applicable to this form
Not applicable to this form
Not applicable to this form
Longer state policy periods
What the signNow audit trail records
The audit trail documents signing activity separately from the authorization’s substantive HIPAA language, creating a retrievable record of how consent was collected.
Authenticate signer:
Capture timestamp:
Record document:
Seal record:
Track activity:
Export audit trail:
Troubleshooting this health information authorization
Resolve signing, plan, authentication, and recordkeeping questions before releasing protected health information through a completed authorization.
The Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps. For HIPAA-covered workflows, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm that your organization has the required BAA before sending protected health information.
The Business Premium plan adds bulk send and quick invite links, while Enterprise adds advanced signer authentication. The Site License can add HIPAA and 21 CFR Part 11 capabilities. Select the plan and contractual controls that match your protected-health-information workflow.
A signer can receive the authorization by email or through a generated signing link. If a stronger identity check is required, Enterprise provides advanced signer authentication, while SMS authentication may be configured as an additional control.
HIPAA permits electronic records, but the authorization must still identify the information, recipient, purpose, and expiration or event where applicable. signNow’s audit trail records actions and timestamps; it does not determine whether the authorization’s language satisfies HIPAA.
The Business plan includes 100 signature invites per user per year when billed annually, with overage fees. The Site License uses $1.50 per signature invite and is designed for 1,000 or more documents annually, with unlimited users.
After completion, signNow provides the signed document and certificate of completion, while the audit trail records signing activity. Export both and retain them with the authorization according to the covered entity’s HIPAA record policy and 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.