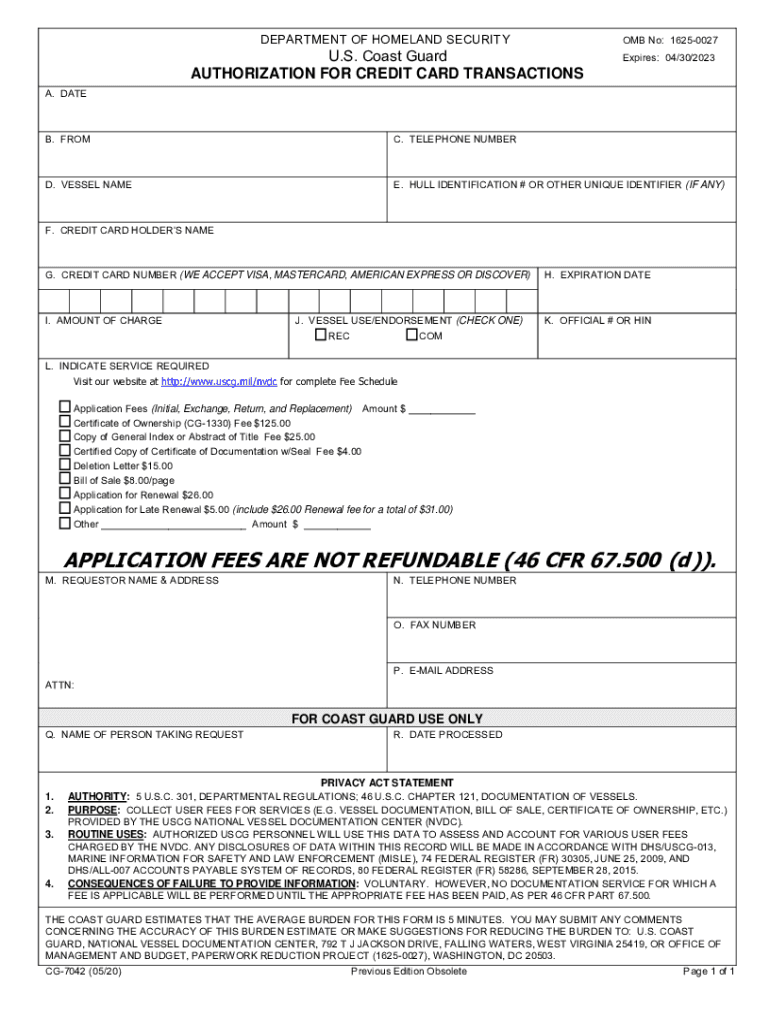
CG7042 Authorization For Credit Card Transactions
Use a CG7042 PDF Authorization For Credit Card Transactions 2020 template to make your document workflow more streamlined.
What the CG7042 authorization does
CG7042 Authorization For Credit Card Transactions is a written authorization that lets a cardholder or authorized representative approve specified credit card transactions for a business relationship. The form records the transaction authority, signer’s intent, and approval evidence in one document. With signNow, the sender uploads the CG7042 form, reviews or adds fillable fields, assigns signer roles, sends it for electronic signature, and stores the completed form with its audit trail. The authorization does not replace payment-network rules, cardholder-data safeguards, or state-law requirements.
Who uses the CG7042 authorization
Payment operations
Payment teams use the CG7042 to document a cardholder’s transaction authorization, capture the signer’s approval, and preserve the completed record with its audit trail.
Business administrators
Businesses use the form when an authorized representative must approve card transactions remotely, while finance and records teams control access and retain the signed authorization.
How to complete the CG7042 form
Use this signNow workflow to prepare the CG7042 authorization, route it to the correct signer, and preserve evidence of completion.
Upload form:
Upload the CG7042 PDF to signNow. Check fields:
Review detected fields and add missing authorization fields. Assign signer:
Assign the cardholder or representative as signer. Complete record:
Send, collect the signature, and save the audit trail.
Recommended authorization workflow setup
Configure the CG7042 workflow around signer attribution, transaction evidence, controlled access, and retention requirements applicable to the authorization record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enabled with completion certificate |
| Document retention | Follow applicable tax and state rules |
| Encryption | TLS 1.2/1.3 and AES-256 encryption |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security controls for card authorizations
Transport encryption:
Stored-data encryption:
Security assurance:
Security certification:
Payment-data protection:
Electronic-signature compliance:
What the audit trail records
The CG7042 audit trail connects the signer, authorization event, document integrity, and completion history into a retrievable evidence record.
Authenticate signer:
Capture timestamps:
Hash document:
Seal audit record:
Log activity:
Export audit trail:
Find and fill out the correct cg7042pdfauthorization for credit card transactions
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| USCG CG-7042 2020 | 4.8 Satisfied (5882 Votes) | |
| USCG CG-7042 2016 | 4.8 Satisfied (4276 Votes) | |
| USCG CG-7042 2014 | 4.6 Satisfied (1163 Votes) |
Privacy and disclosure checks for card authorizations
Store only the cardholder information necessary for this authorization, avoiding full card numbers and unrelated personal data. Capture the signer’s electronic consent before signing, including access to the authorization terms and any consumer disclosure required by ESIGN. Restrict completed authorization forms and audit trails to personnel handling payment approvals, disputes, or records administration. Confirm the signer’s identity and authorization scope before processing transactions, especially when a business employee signs for an organization.
Processing stages for card authorizations
Move the CG7042 authorization from field preparation through signer review and controlled archival without separating the evidence from the transaction record.
Prepare the form
Deliver to signer
Complete signer review
Archive completed record
Risks of incomplete authorization records
Weak consent
Authorization dispute
Proof gap
Privacy exposure
Legal standing of the authorization
A signed CG7042 authorization can support a U.S. business transaction when the signer demonstrates intent, consents to electronic records, can be attributed to the record, and the record remains reproducible under ESIGN, 15 U.S.C. ch. 96, and applicable UETA law. These frameworks do not cover wills, codicils, testamentary trusts, or certain court orders and official filings.

Troubleshooting CG7042 authorization workflows
Resolve field, signer, evidence, plan, and retention questions before relying on a completed CG7042 authorization for a transaction.
Upload the original CG7042 PDF again, then review signNow’s detected fields before sending. Add missing signer, date, or authorization fields manually and confirm each field is assigned to the correct cardholder or authorized representative.
The Business plan includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month when billed annually. Business Premium is $15 per user per month annually and adds bulk send.
A signer can usually open the request from the email link without creating an account. If stronger attribution is needed, configure SMS verification or another available authentication method before sending the CG7042 authorization.
Use the completed document together with its audit trail. The record should show intent, consent, signer attribution, timestamps, and reliable reproduction; ESIGN and applicable UETA law govern electronic business records, subject to statutory exclusions.
Do not place full card numbers in unnecessary fields or filenames. PCI DSS addresses cardholder-data safeguards, while signNow provides encryption in transit and at rest for the electronic record.
Export the signed CG7042 form and audit trail before closing the transaction file. Apply the retention period required for the transaction context, including IRC §6501(a) when the record supports federal tax documentation.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.