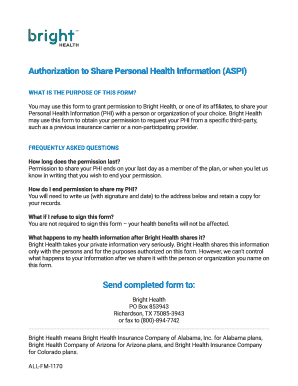
Authorization To Share Personal Health Information Aspi
Use a Authorization To Share Personal Health Information ASPI template to make your document workflow more streamlined.
What this health authorization does
Authorization To Share Personal Health Information Aspi is a patient permission record identifying which personal health information may be disclosed, to whom, for what purpose, and for how long. The patient or legally authorized representative reviews those limits and signs the document. A provider or other covered entity then uses the completed authorization to document consent before releasing the specified information. HIPAA’s authorization rules require meaningful scope and purpose details; signNow provides the electronic workflow, signature evidence, and audit trail, but the organization remains responsible for accurate content and lawful disclosure.
Who uses this authorization
Healthcare providers
Healthcare providers use this authorization to capture a patient’s permission before disclosing specified records to a named recipient. Staff should verify the information scope, purpose, expiration, representative authority, and required HIPAA language before sending the document for signature.
Patients and representatives
Patients and authorized representatives review the disclosure purpose, recipient, information categories, expiration, and revocation instructions before signing. They should receive a reproducible copy and understand that the authorization governs only the information and recipient identified in the document.
How this health authorization works
The authorization moves from document preparation through consent, signing, and controlled retention for the named health information recipient.
Upload form: Upload the authorization document to signNow. Prepare fields: Review detected fields and add missing consent fields. Assign signers: Assign the patient and recipient signing roles. Store record: Complete signatures and retain the audit trail.
Complete this authorization in signNow
Prepare the authorization’s disclosure scope and signer details before sending it through signNow for an auditable electronic signature.
Upload form:
Upload the completed authorization template. Review fields:
Check patient and recipient fields. Add fields:
Add signatures, dates, and consent fields. Send document:
Send through a secure invitation. Retain evidence:
Store the signed PDF and audit trail.
Privacy and disclosure pitfalls
Listing an overly broad recipient can disclose personal health information beyond the patient’s intended purpose. Leaving expiration or purpose fields incomplete weakens the record of the patient’s informed consent. Sending the signed authorization to an unintended email address exposes protected information and consent details. Allowing unrestricted template access can let unauthorized staff alter recipient, purpose, or disclosure fields.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization workflow setup
Configure identity checks, evidence capture, retention, encryption, and access controls before sending patient authorizations.
| Setting | Recommendation |
|---|---|
| Authentication method | Email invitation with SMS verification |
| Signature type | Electronic signature with patient intent |
| Audit trail | Export completed audit trail |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption and provisioning | AES-256 with role-based user access |
Platform requirements for signing
Use Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow mobile apps support signing on iOS and Android, while encrypted connections use TLS 1.2 or TLS 1.3.
Browser support Chrome, Firefox, Safari, and Edge Operating systems Windows, macOS, iOS, and Android Secure connection TLS 1.2 or 1.3 required
Healthcare organizations should use managed devices, role-based accounts, and controlled access to completed authorizations. Enterprise deployments may connect signNow with identity, storage, or records systems through available integrations and API capabilities. Confirm device management, session controls, and retention policies before exposing PHI.



Features for health information authorizations
signNow connects document preparation, patient signing, evidence capture, and controlled retention for Authorization To Share Personal Health Information Aspi.
Field preparation
Upload the authorization and review signNow’s detected fields, then add missing patient, recipient, purpose, expiration, signature, and date fields before sending.
Signer routing
Assign the patient or authorized representative as signer and route the completed authorization to the named healthcare recipient or internal records team.
Audit trail
Capture signer actions, timestamps, and document history in an audit trail that can accompany the signed authorization during compliance review.
Signer authentication
Use SMS verification or stronger authentication options when the organization’s risk assessment requires more than an email invitation.
Secure retention
Store completed authorizations with controlled access and encryption while applying the retention period required for the underlying HIPAA record.
System integration
Connect signNow with storage and healthcare operations systems to reduce manual copying of recipient and document information after signing.
Security and health data protection
HIPAA protection:
Transit encryption:
Stored encryption:
Security certification:
Information security:
Electronic signatures:
Authorization retention schedule
Retain the authorization according to the rule governing the underlying disclosure record, and apply longer state requirements when they control.
6 years from creation or last effective date
3 years from tax filing
3 years after hire or one year after termination
3 years for payroll records
Longer period under state law
Record-keeping practices for authorizations
Preserve the patient’s authorization, signature evidence, access history, and disclosure controls as one reviewable record.
Apply the governing retention period
Export the audit trail
Limit access to completed records
Validate scope before disclosure
Risks of incomplete authorization
Unauthorized disclosure
Consent gap
Recipient ambiguity
Evidence weakness
Authorization form troubleshooting
Resolve field, signer, plan, and retention questions before releasing this patient authorization for disclosure.
Business includes legally binding eSignatures, templates, and audit trails for this authorization. Business Premium adds bulk send and kiosk mode, while Enterprise adds advanced signer authentication. A HIPAA workflow requires signNow’s HIPAA-compliant configuration and a business associate agreement where signNow processes PHI.
The authorization can be signed electronically when the patient demonstrates intent, consents to electronic records, can access the record, and the completed record remains reproducible. ESIGN and applicable state law, including UETA or New York ESRA, govern electronic execution.
Use signNow’s field editor to identify patient, recipient, purpose, information scope, expiration, signature, and date fields. Auto-detection can identify fillable areas, but the sender must verify every field against the authorization’s required content before sending.
A signer can often complete the document without a signNow account through the secure invitation. Add SMS authentication when identity assurance is needed, and confirm the patient’s electronic-record access and consent before signing.
Business provides audit trails; Business Premium adds bulk send and kiosk mode; Enterprise adds advanced signer authentication. Subscription plans include 100 signature invites per user annually, with plan-specific overage fees, so confirm volume before deployment.
HIPAA requires covered entities to retain required policies, procedures, and related documentation for six years from creation or the last effective date under 45 CFR 164.530(j). Apply longer state or clinical-record rules when they govern the underlying authorization.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.