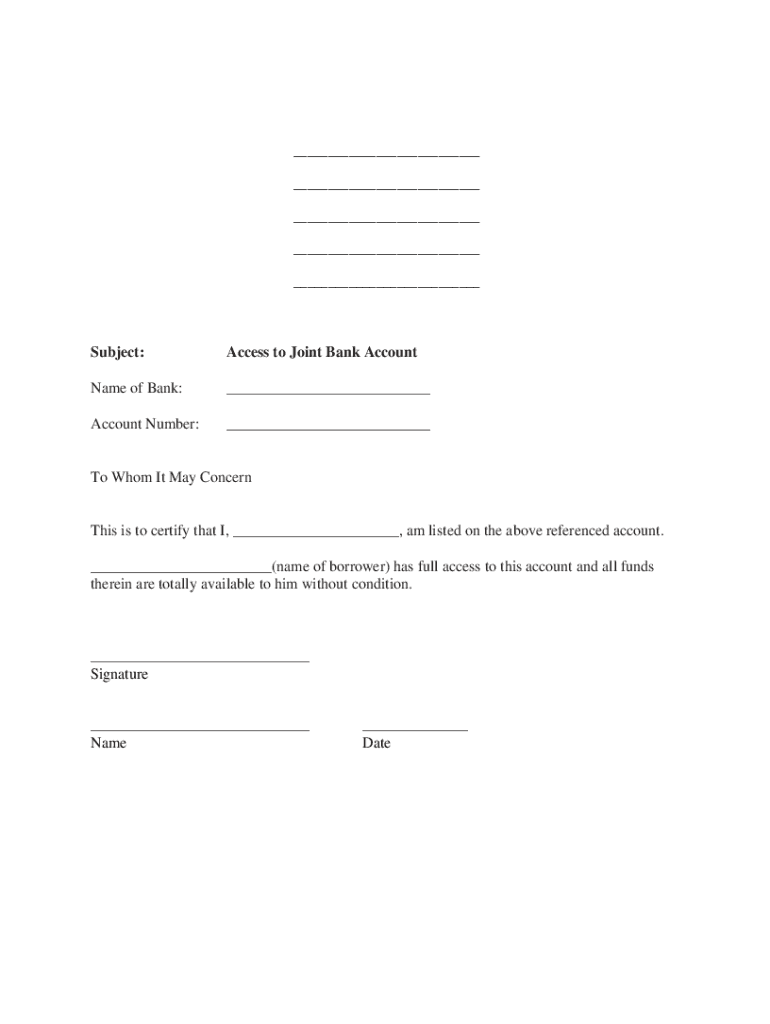
Joint Access Letter Form
Use a Joint Access Letter Template template to make your document workflow more streamlined.
What Joint Access Letter Form does
Joint Access Letter Form is a business document used to give two or more parties shared access, authority, or permission for a defined matter. The supplied U.S. reference materials do not identify a federal issuing agency, statutory field list, filing deadline, or official form code for this title, so the parties should confirm the document’s purpose and governing state law before signing. In signNow, upload the document, review detected fields, place signature and date fields for each authorized signer, send it, and retain the completed PDF with its audit trail.
Who uses this access letter
Business operations
Operations teams use Joint Access Letter Form to document shared access, delegated authority, or permissions between business parties. The document can support contracts, internal approvals, vendor arrangements, or controlled access decisions, but its legal effect depends on the actual terms and governing state law.
Legal review
Legal and compliance teams use the letter when a signed record must identify each authorized party and preserve the signing history. They should confirm whether separate notarization, witnessing, agency language, or regulated-record controls apply before relying on it.
Businesses that use this letter
Joint Access Letter Form workflows fit organizations that must document shared authority, identify every signer, and preserve a reliable electronic record.
Small businesses can use a reusable Joint Access Letter Form template to document shared access decisions, collect signatures from owners or representatives, and retain the completed letter without coordinating a paper exchange. Legal services teams can route a Joint Access Letter Form in role-based order, review signer identity and scope, and preserve the audit trail alongside the matter file for later administrative or contractual review. Enterprise operations teams can connect signNow with systems such as Salesforce, NetSuite, or Microsoft 365 to route the letter through established records processes while administrators control templates, users, and access permissions.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Key features for this form
signNow organizes the Joint Access Letter Form workflow around accurate field placement, authorized signers, electronic records, and reviewable completion evidence.
Field detection
Upload the Joint Access Letter Form and review automatically detected fields before adding any missing signature, date, or acknowledgment fields.
Signer assignment
Route separate signature fields to each authorized party, reducing uncertainty about who approved the letter and when.
Electronic signing
Collect typed or drawn electronic signatures while preserving the document’s completion history and signer actions.
Flexible delivery
Use email delivery or a signing link when the parties need separate access to the same letter.
Audit trail
Retain the executed PDF with its audit trail so reviewers can examine the signing sequence and recorded events.
Data protection
Apply signNow’s TLS 1.2/1.3 and AES-256 protections to the electronic workflow and stored document data.
How the form workflow works
Use this sequence to prepare, route, sign, and preserve the Joint Access Letter Form without losing signer attribution or document history.
Upload document: Upload the Joint Access Letter Form file to signNow. Review fields: Review detected fields and add missing signatures or dates. Assign signers: Assign each signature field to an authorized party. Store record: Send, complete, and store the signed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete the letter in signNow
Follow these steps to prepare the Joint Access Letter Form, obtain the required signatures, and preserve evidence of completion.
Upload:
Upload the Joint Access Letter Form. Review:
Check detected fields and add missing ones. Assign:
Assign each field to its signer. Send:
Send the letter for electronic signatures. Archive:
Download the completed record and audit trail.
Recommended workflow configuration
Configure the Joint Access Letter Form around signer attribution, electronic consent, document integrity, and the retention rule applicable to its underlying business purpose.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Retained with completed PDF |
| Document retention | Apply the governing record rule |
| Encryption | TLS 1.2/1.3 and AES-256 |
What the audit trail records
The signNow audit trail documents the events surrounding the Joint Access Letter Form, helping reviewers connect the executed file with signer activity and timestamps.
Signer authentication:
Timestamp capture:
Document integrity:
Tamper evidence:
Action history:
Audit retrieval:
Platform requirements for signing
Signers can open the Joint Access Letter Form through Chrome, Firefox, Safari, or Edge on Windows and macOS, or use signNow mobile apps on iOS and Android. The supplied product facts specify TLS 1.2/1.3 for data in transit.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile apps iOS and Android mobile apps
Organizations using managed devices should verify browser updates, mobile permissions, identity-provider policies, and repository access before deployment. Enterprise teams should also confirm whether their selected signNow plan provides the required API, SSO, authentication, or compliance add-ons for this document’s underlying use case.
Signer authentication and certificates
PKI certificates:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Audit evidence:
Privacy and disclosure pitfalls
Including unrestricted personal data can expose information to every recipient who receives or stores the completed Joint Access Letter Form. Failing to capture electronic consent may leave the signer’s agreement to use an electronic record difficult to prove later. Assigning one shared account to multiple representatives obscures which person reviewed or signed the Joint Access Letter Form. Sending the letter to an outdated email address can disclose access terms to an unintended recipient.
Best practices for this letter
Accurate signer assignment, documented consent, and controlled retention reduce disputes about who received access and what the signed letter authorized.
Confirm authority before sending
Assign every field precisely
Preserve the executed record
Document electronic consent clearly
Risks of an incomplete letter
Invalid authority
Electronic record dispute
Access disagreement
Weak evidence
Key performance indicators that demonstrate SignNow's proven track record.
Joint Access Letter Form troubleshooting
These answers address field assignment, signer verification, electronic consent, plan selection, security, and preservation of the completed Joint Access Letter Form.
Upload the original Joint Access Letter Form file again, then review signNow’s detected fields before sending. Auto-detection may not identify every blank, so add missing signature, date, initials, or acknowledgment fields manually and assign each one to the correct signer.
The signNow Business plan is listed at $8 per user per month with annual billing and includes templates and audit trails. Business Premium adds bulk send at $15 per user per month annually; confirm the selected plan before preparing multiple letters.
Use a verified signer email, then add SMS OTP or another available authentication control when the letter grants sensitive access. Stronger authentication supports attribution, but the parties remain responsible for confirming the signer’s legal authority.
For a consumer-facing electronic record, provide the ESIGN disclosure, explain the right to receive paper, confirm electronic access, and explain withdrawal procedures under 15 U.S.C. §7001(c). Preserve evidence that the signer consented before relying on the record.
signNow encrypts data in transit with TLS 1.2/1.3 and at rest with AES-256. Its compliance materials identify ESIGN and UETA compliance, while HIPAA workflows require a business associate agreement when protected health information is involved.
Open the completed document and its certificate of completion or audit trail from the signNow account, then export both records to the organization’s controlled repository. Apply the retention rule for the underlying transaction because no universal period is established for this title.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.