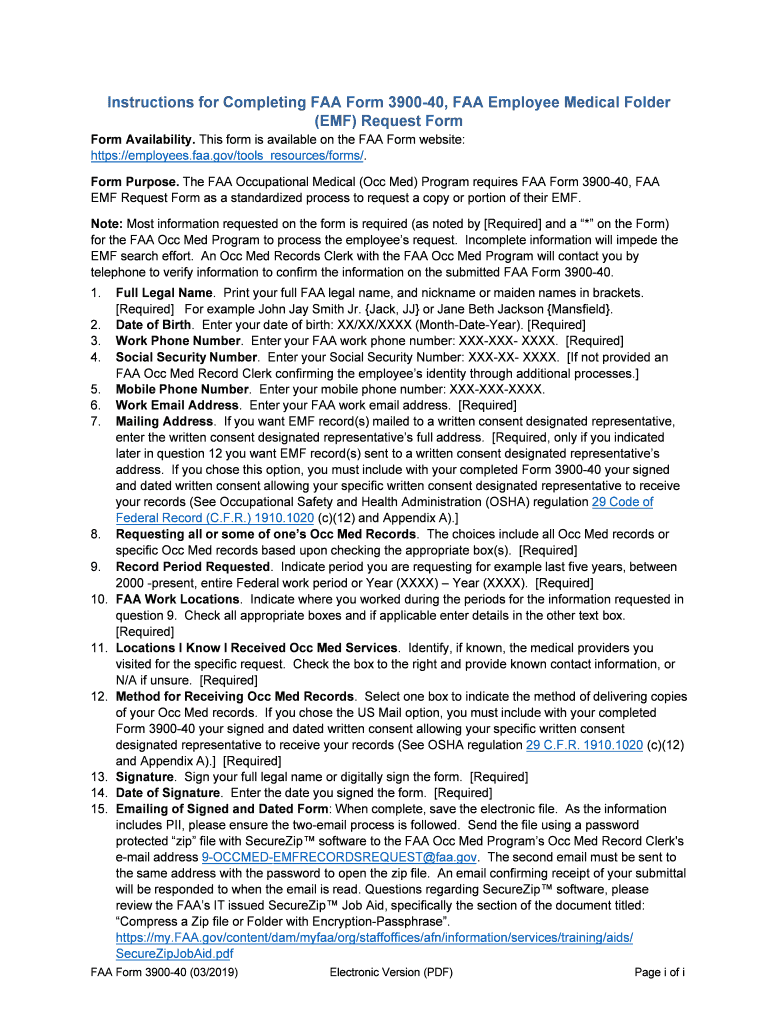
Ato Employee Medical Folder Request Form Form 3900 40
Use a ATO Employee Medical Folder Request Form Form 3900 40 template to make your document workflow more streamlined.
What this medical-folder request does
The Ato Employee Medical Folder Request Form Form 3900 40 is a request document for obtaining or coordinating access to an employee medical folder. The available form name does not identify an issuing agency, required fields, filing deadline, or submission office, so those details must be confirmed from the source document or receiving organization. In signNow, upload the PDF, auto-detect or place fields, assign the authorized signer, send it securely, and retain the completed document with its audit trail. HIPAA obligations apply when the request contains protected health information.
Who uses this medical-folder request
Human resources
Human-resources and benefits teams can use the Ato Employee Medical Folder Request Form Form 3900 40 to route an employee’s folder request for review and signature. They should verify the requester’s authority, limit access to necessary personnel, and apply HIPAA or state privacy controls when the document contains protected health information.
Healthcare records
Healthcare administrators and records teams can use the request when coordinating access to an employee medical folder. The workflow can cover authorization and consent records, but signNow does not decide disclosure eligibility; the receiving organization must apply HIPAA, state law, and its own records policy.
How this medical-folder request works
The request moves from an uploaded document to an auditable signature record through four focused signNow steps.
Upload: Upload the medical-folder request PDF. Add fields: Auto-detect or place fillable fields. Assign signer: Assign the employee or authorized recipient. Finish: Complete, audit, and store the request.
Quick steps to complete the request
Use this sequence to prepare the medical-folder request without changing its substantive authorization requirements.
Upload:
Upload the source PDF to signNow. Place fields:
Review detected fields and add missing ones. Assign:
Assign the authorized recipient and signing order. Complete:
Send, monitor, download, and retain the completed request.
What the audit trail records
The signNow audit trail documents the signing event separately from the medical-folder request’s substantive authorization and disclosure decisions.
Authenticate signer:
Capture timestamps:
Record integrity:
Seal history:
Review completion:
Export evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended workflow setup
Configure the request around signer identity, protected information, audit evidence, and the retention rule that applies to the medical record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email invitation with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail and encryption | Detailed audit trail with AES-256 storage |
| Document retention | Six years when HIPAA applies |
| User provisioning | Admin-managed roles and least-privilege access |
Record-keeping practices for this request
Preserve the signed request, audit evidence, authorization context, and retention decision together so the employee medical-folder workflow remains reviewable.
Apply the correct medical-record retention period
Export the audit trail with the signed document
Archive the request securely
Check state rules before deletion
Platform requirements for this form
Complete the Ato Employee Medical Folder Request Form Form 3900 40 through Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow encrypts data in transit using TLS 1.2 or TLS 1.3 and provides mobile applications for iOS and Android.
Browser support Chrome, Firefox, Safari, and Edge on Windows or macOS Mobile access iOS and Android signNow mobile applications Transport security TLS 1.2 or 1.3 for transmitted data
Use a managed device when the request contains protected health information, and restrict downloaded copies to authorized personnel. Organizations connecting signNow to internal systems should separately review API access, SSO provisioning, retention controls, and any certificate or long-term validation requirements imposed by their medical-record policy.
Security for medical-folder requests
Stored data:
Data in transit:
Security report:
Information security:
Health information:
Privacy framework:
Organizations that use this request
The best fit depends on who controls the employee medical folder and which privacy, authorization, and retention rules govern the request.
A small healthcare practice can use the request to route an employee medical-folder access document, while restricting the workspace to designated records staff and preserving the signed PDF with its audit trail. A regional employer can standardize requests across human-resources and benefits teams, using templates and delegated sending while requiring recipient verification before any employee health information is disclosed. An enterprise healthcare system can connect repeatable request workflows to approved repositories or internal applications, then apply role-based access, HIPAA controls, and state-specific retention review across departments.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
State rules and exclusions
State notarization
Wills excluded
Family-law documents
Real-estate deeds
Rollout and retention timeline
Use the timeline to coordinate testing, controlled sending, staff access, and retention for the employee medical-folder request.
setup:
First send:
Team onboarding:
HIPAA retention:
State review:
Audit export:
Access review:
Deletion decision:
Privacy pitfalls to address
Sending the request to an unverified recipient can expose employee health information and create an unauthorized disclosure risk under HIPAA. Leaving authorization or consent language incomplete may prevent the receiving organization from processing the medical-folder request. Granting broad workspace access can expose signed requests beyond the human-resources or medical-record personnel who need them. Deleting the signed PDF without its audit trail can weaken the organization’s ability to reconstruct the request history.
Healthcare use cases for the request
Healthcare teams can adapt a signNow workflow for this request while keeping authorization, disclosure, and retention decisions under their own compliance program.
Healthcare operations
A healthcare organization can send an employee medical-folder request to an authorized recipient, collect the signature remotely, and preserve the completion record for its compliance team.
- Confirm the recipient’s authorization before sending.
- Use HIPAA controls when protected health information is present.
This scenario illustrates a controlled healthcare workflow without claiming that signNow determines whether disclosure is legally permitted. The organization remains responsible for consent language, minimum-necessary access, recipient verification, and retention under HIPAA and applicable state medical-record rules. signNow supplies the electronic signing and audit evidence layer.
Fertility care
Fertility Centers of Illinois is a documented signNow customer whose healthcare workflow demonstrates why an API-connected signature process can help manage sensitive forms across operational teams.
- Use API workflows for repeatable healthcare requests.
- Keep authorization and disclosure review outside the signature platform.
The customer story identifies Fertility Centers of Illinois and its positive API experience, but it does not establish use of this exact form. Apply the example narrowly: reuse the integration pattern only after mapping the medical-folder request’s recipients, disclosures, access controls, and applicable HIPAA business associate requirements.
Troubleshooting medical folder requests
Resolve document, signer, compliance, plan, and retention questions before using the completed Ato Employee Medical Folder Request Form Form 3900 40.
Upload the original PDF again, then check that the file opens normally before placing fields. Business supports templates and audit trails; the 7-day free trial also permits workflow testing before subscription selection. The form’s agency-specific acceptance rules still require confirmation from the receiving office.
Business includes legally binding eSignatures, templates, and audit trails at $8 per user per month when billed annually. For protected health information, signNow lists HIPAA compliance with a required business associate agreement; configure the workflow only after confirming the covered-entity relationship.
A completed signature does not replace a required medical-record authorization or agency-specific consent. ESIGN and UETA address electronic signatures, while HIPAA privacy requirements govern protected health information. Confirm the request form’s disclosure language and recipient authority before sending it.
If the signer cannot access the email, verify the address and resend the invitation from signNow. SMS-based authentication may require a suitable plan or configuration. Keep the recipient’s identity aligned with the employee or authorized requester named on this medical-folder request.
Business plans include 100 signature invites per user annually, with overage fees after the included allocation. Business Premium adds bulk send, while Enterprise adds advanced signer authentication. Select a plan based on this form’s volume and authentication needs rather than assuming unlimited invitations.
Export the completed document and audit trail from signNow, then retain them under the applicable medical-record policy. HIPAA-covered documentation generally requires six years from creation or the last effective date under 45 CFR 164.530(j); state rules may require longer retention.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.