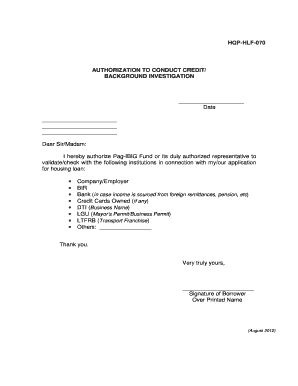
Authorization Letter To Conduct Credit Investigation Form
Use a Authorization Letter To Conduct Credit Investigation template to make your document workflow more streamlined.
What this authorization letter does
An Authorization Letter To Conduct Credit Investigation Form gives a named recipient permission to investigate an applicant’s credit information for a stated purpose. It normally identifies the applicant, authorized investigator, information sources or scope, consent language, signature, and date. The letter is not a credit report and does not itself determine eligibility. In a signNow workflow, the sender uploads the form, checks detected fields, adds signer and recipient details, sends it for signature, and retains the signed document with its audit trail. Apply ESIGN, UETA, and applicable state privacy requirements.
Who uses this authorization letter
Credit investigations
Credit unions, lenders, property managers, and private investigators use this letter to obtain a person’s permission before contacting credit bureaus, creditors, employers, or other authorized sources. The document should identify the applicant, recipient, investigation purpose, permitted disclosures, signer, and date so the recipient can evaluate the authorization’s scope.
Related workflows
Real estate and financial-services teams can send the letter with related applications, disclosures, consent forms, or agreements. signNow supports templates, signing links, audit trails, and mobile apps, helping teams collect the authorization without rekeying the applicant’s identifying information.
How to complete the authorization letter
Follow these steps to prepare, sign, and retain an Authorization Letter To Conduct Credit Investigation Form electronically.
Upload form:
Upload the completed Authorization Letter To Conduct Credit Investigation Form to signNow. Review details:
Confirm names, addresses, authorization scope, and investigation purpose before sending. Add fields:
Place signature and date fields beside each required signer’s information. Send securely:
Send the authorization letter by email or a secure signing link. Archive records:
Store the signed letter and completion certificate with the audit trail.
Recommended authorization letter setup
Configure the Authorization Letter To Conduct Credit Investigation Form for identifiable signers, documented consent, reliable evidence, and controlled retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion certificate and activity history |
| Document retention | Retain according to applicable state policy |
| Encryption | Use TLS 1.2/1.3 and AES-256 protection |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
signNow records authentication, timestamps, document integrity, and retrieval evidence for the completed authorization letter.
Authenticate signer:
Capture timestamp:
Log activity:
Hash document:
Seal record:
Export trail:
Privacy and disclosure pitfalls
Including a broad credit-investigation purpose can leave recipients uncertain about which records the signer actually authorized them to obtain. Sending the letter before confirming the applicant’s legal name, address, and recipient details creates avoidable identity and attribution disputes. Storing the signed authorization beside unrestricted applicant files can expose sensitive financial information to personnel without an investigation role. Treating an electronic signature as permission to bypass privacy laws can create disclosure problems even when the signature itself is valid.
Risks of an incomplete authorization letter
Consent dispute
Limited investigation
Attribution challenge
Proof weakness
Recordkeeping practices for this form
Retain the authorization letter with evidence showing what the signer approved, when approval occurred, and who could access the record.
Match retention to the governing rule
Export the complete evidence package
Restrict access to applicant data
Verify the authorization scope
Security for authorization records
Transport encryption:
Stored encryption:
Security reporting:
Information security:
Electronic signatures:
Health information:
Processing stages for the authorization letter
The form has no universal federal processing deadline; timing depends on document readiness, signer response, and the investigator’s requirements.
Prepare the document
Deliver to signer
Collect signer approval
Complete and archive



Authorization letter troubleshooting
Resolve field, signer, consent, plan, healthcare, and legal-scope questions before relying on the completed authorization letter.
Upload the original PDF again and confirm that fields are not locked, flattened, or password-protected. signNow can then detect fillable areas or let you place fields manually before sending the Authorization Letter To Conduct Credit Investigation Form.
Use email authentication or add SMS verification when signer attribution needs stronger evidence. The Business plan includes audit trails; advanced signer authentication is available with Enterprise features, subject to the selected configuration and agreement.
For a consumer-facing authorization, provide the ESIGN Act disclosure, explain access to electronic records, and describe withdrawal procedures. These requirements come from 15 U.S.C. §7001(c), not from signNow.
The Business plan costs $8/user/month when billed annually and includes audit trails, templates, and mobile apps. It includes 100 signature invites per user annually; additional invites may incur overage fees.
For healthcare-related credit investigations involving protected health information, confirm that a business associate agreement is required. signNow lists HIPAA compliance with a BAA requirement; apply the HIPAA Privacy Rule to the disclosure.
Electronic signatures generally receive legal recognition under ESIGN and applicable state law when intent, consent, attribution, and record retention are demonstrated. Wills, court filings, and listed statutory exceptions remain outside that framework.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.