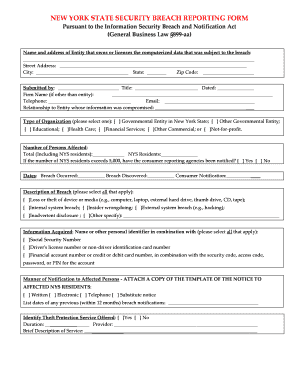
New York State Security Breach Reporting Form Pursuant To The Information Security Breach And Notification Act General Business
Use a NEW YORK STATE SECURITY BREACH REPORTING FORM Pursuant To The Information Security Breach And Notification Act General Business template to make your document workflow more streamlined.
What this New York breach form does
The New York State Security Breach Reporting Form Pursuant To The Information Security Breach And Notification Act General Business is a business notice used to report a security breach involving New York residents’ private information. It records the organization’s identity, breach circumstances, affected data, resident impact, and notification details for New York regulators. The completed form supports reporting under New York General Business Law §§ 899-aa and 899-bb, while signNow can help teams complete fields, obtain authorized signatures, and preserve the signed record and audit trail.
Key capabilities for breach reporting
This workflow combines structured incident reporting, controlled approvals, electronic signatures, and auditable recordkeeping for New York breach-response teams.
Structured reporting
Capture the reporting organization, contact information, incident description, and affected New York residents in one structured record for review.
Guided completion
Use signNow’s fillable fields to enter breach details consistently, reducing transcription errors when several internal teams contribute information.
Signature routing
Route the completed report to an authorized representative for an electronic signature when the organization’s process requires approval.
Audit trail
Preserve timestamps, signer activity, and document history through signNow’s audit trail for internal review and later recordkeeping.
Controlled access
Use role-based access and encryption controls to limit exposure of sensitive incident information during preparation and signature collection.
Workflow continuity
Connect completed records with supported storage or business systems so compliance teams can organize breach documentation alongside related case materials.
Who uses this breach report
Incident response
Incident response teams use the form to document the breach, affected New York residents, private-information categories, notification actions, and authorized approval before regulatory submission.
Compliance teams
Privacy counsel, compliance officers, and authorized business representatives use signNow to coordinate review, signature collection, audit evidence, and secure retention of the completed report.
Businesses that use this workflow
The form is most useful where a security incident requires coordinated fact gathering, authorized approval, and a defensible record of New York reporting activity.
A solo New York business owner can prepare the incident facts, identify affected private information, and route the completed report to counsel or an authorized signer without assembling separate paper packets. A regional healthcare provider can coordinate breach details, notification records, and authorized approval while restricting access to protected information under its HIPAA compliance program and business associate agreement. An enterprise privacy office can standardize reports across subsidiaries, use role-based review, preserve audit trails, and connect completed New York filings with its broader incident-management and records program.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the form workflow works
The signNow workflow moves this New York breach report from preparation to authorized approval while keeping the final document connected to its audit evidence.
Upload: Upload the New York breach-report template. Prepare fields: Auto-detect or place its fillable fields. Complete: Enter incident and notification information. Approve and store: Send for authorized signature and preserve the record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How to complete this New York form
Use this sequence to prepare the form, obtain approval, and retain a complete record of the New York breach-reporting action.
Upload form:
Upload the New York breach reporting form to signNow. Check fields:
Confirm incident and notification fields are fillable. Complete report:
Enter affected-information and organization details. Route signature:
Send to the authorized representative for signature. Store evidence:
Download the signed report with its audit trail.
How the audit trail records approval
The audit trail documents the technical and human events connecting this New York breach report to its authorized signer and final record.
Signer authentication:
Timestamp capture:
Document hashing:
Tamper sealing:
Activity logging:
Evidence export:
Platform requirements for this form
Use signNow in Chrome, Firefox, Safari, or Edge on Windows or macOS. The signNow mobile apps support iOS and Android for reviewing and signing this New York breach report. Secure transport uses TLS 1.2/1.3.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile systems iOS and Android mobile apps
Enterprise deployments can pair managed Windows, macOS, iOS, and Android devices with administrative controls, API access, and SSO where the selected signNow plan provides them. Regulated teams should also configure access permissions, retention policies, and any certificate or authentication controls required by their internal incident-response procedures.



Recommended workflow settings
Use controlled authentication, an auditable signature process, and authority-based retention for this sensitive New York incident record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enabled with exported completion record |
| Document retention | Organization policy and applicable authority |
| Encryption | TLS 1.2/1.3 and AES-256 at rest |
Security controls for breach reports
Transport encryption:
Stored encryption:
Security certification:
Information security:
Signature compliance:
Signer verification:
Privacy and disclosure pitfalls
Including names, account details, or unnecessary identifiers in the report can expand disclosure beyond information needed for New York notification review. Sending the completed report to the wrong recipient can expose incident details before legal, regulatory, and communications teams approve distribution. Failing to record signer consent and authentication weakens evidence that the authorized representative approved the submitted breach information. Leaving shared templates editable can allow unauthorized changes to incident facts, affected data descriptions, or notification dates.
Retention periods for related records
The New York breach-reporting statute does not create one universal retention period for every supporting record. Apply the rule tied to the record’s legal category and preserve the completed report under organizational policy.
3 years: federal tax records
6 years: material tax understatement
6 years: HIPAA documentation
3 years: FLSA payroll records
5 years: OSHA injury records
Recordkeeping practices for New York reports
Accurate preparation, restricted access, linked audit evidence, and authority-based retention make the completed report easier to review and defend.
Minimize personal information before routing
Preserve the report and audit trail together
Reconcile incident facts before approval
Apply the correct retention authority
Troubleshooting New York breach reports
These answers address field mapping, electronic signatures, authentication, audit evidence, plan limits, and sensitive-data handling for this New York reporting workflow.
Upload the organization’s New York breach reporting template as a PDF or reusable signNow template, then verify that incident, resident, and notification fields are mapped correctly. The Business plan includes templates, while Business Premium adds bulk send for repeated reporting workflows.
A New York report may be electronically signed when the organization has signer intent, electronic consent where required, signer attribution, and a retained reproducible record. ESIGN and New York’s Electronic Signatures and Records Act support electronic records, but filing rules should be confirmed with the relevant authority.
Use signNow’s audit trail to review signer identity details, timestamps, actions, and document history. Download the completed report and audit evidence together, then apply the organization’s retention policy and any applicable New York breach-response requirements.
Business provides legally binding eSignatures and audit trails at $8 per user per month with annual billing. Business Premium is $15 per user per month annually and adds bulk send, which may help when multiple approved notices use the same structure.
Use SMS OTP or another available authentication method when incident sensitivity requires more than an email link. Enterprise adds advanced signer authentication, while stronger controls should be selected according to the organization’s risk assessment and New York reporting process.
If the report includes protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Store only necessary information, restrict access, and confirm that the completed report’s retention schedule satisfies the healthcare organization’s obligations under 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.