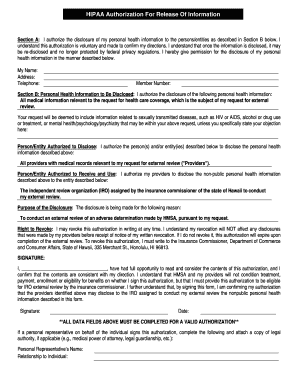
Section A: Authorize the disclosure of my personal health information to the persons/entities as described in Section B below
Use a Section AI Authorize The Disclosure Of My Personal Health Information To The PersonsEntities As Described In Section B Below 0 template to make your document workflow more streamlined.
What this health information authorization does
This authorization form gives named persons or entities permission to receive or use specified personal health information. Section A identifies the individual authorizing disclosure, while Section B identifies the recipients or entities allowed to receive the information. The completed document should state the information covered, its purpose, expiration or revocation terms, and the authorizing person’s signature. Healthcare organizations should apply HIPAA requirements, verify the signer’s identity, and disclose only the information and recipients described in the authorization. A signed electronic record can support consent documentation when applicable legal and organizational requirements are satisfied.
Who uses this authorization form
Healthcare providers
Healthcare providers, medical practices, and release-of-information teams use this form when a patient authorizes disclosure to named persons or entities. They review Section A, identify Section B recipients, limit the records and purpose, collect the signature, and verify expiration or revocation terms before release.
Authorized recipients
Patients, personal representatives, attorneys, insurers, and designated family members may participate as authorizers or recipients. The workflow should make the disclosure scope understandable, preserve the signed authorization, and restrict access to staff with a defined need to process the request.
Who benefits from this authorization workflow
Healthcare release coordinators use the form to document a patient’s permission before sending specified records to an identified provider, insurer, attorney, or family representative. signNow helps them route the authorization, capture the signature, and retain completion evidence without recreating the document for each request. Fertility and specialty-care administrators use similar authorization workflows when patients permit information sharing among treatment providers. Fertility Centers of Illinois founder John Butler described signNow’s responsive API and service; a configured workflow can connect signed authorizations with internal records while preserving controlled access to PHI.
Features for this authorization form
signNow connects field review, signer consent, audit evidence, and controlled storage for Section A and Section B authorization workflows.
Defined scope
Define the specific individuals, records, and recipients covered by the authorization before sending, helping staff apply the requested disclosure scope consistently.
Field detection
Upload the authorization and review detected fields for Section A, Section B, signature, date, purpose, and expiration before inviting the signer.
Electronic consent
Collect a traceable electronic signature with intent and consent evidence, supporting organized authorization records under applicable ESIGN, UETA, and HIPAA procedures.
Audit trail
Capture timestamps, signer actions, and document history in an audit trail that helps healthcare teams investigate when and how authorization occurred.
Access control
Use role-based access and controlled templates to reduce accidental disclosure while allowing authorized staff to prepare and route the form.
Secure records
Keep the signed authorization and completion evidence together so disclosure staff can verify the applicable recipient, scope, and expiration before releasing PHI.
How this authorization works in signNow
The signNow flow moves this authorization from field review to signer consent and controlled retention without changing the disclosure scope.
Upload form: Upload the completed authorization template to signNow. Detect and verify: Auto-detect fields, then verify Section A and Section B. Route for signature: Send the authorization to the named signer. Complete and retain: Store the signed record and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete this authorization in signNow
Prepare Section A and Section B carefully, then use signNow to route the authorization and preserve evidence of completion.
Upload document:
Upload the authorization PDF to signNow. Review fields:
Review detected fields in Section A and Section B. Add required fields:
Add signature, date, consent, and recipient fields. Add signer:
Enter the authorized signer’s email address. Send request:
Send the prepared authorization for signature. Store evidence:
Store the signed form with its audit trail.
How the authorization audit trail works
For this PHI authorization, the audit trail connects signer identity, consent actions, document history, and retrievable completion evidence.
Authenticate signer:
Capture timestamps:
Record document history:
Seal evidence:
Review completion:
Export audit trail:
Find and fill out the correct section ai authorize the disclosure of my personal health information to the personsentities as described in section b below
airSlate SignNow helps you fill in and sign documents in minutes, error-free. Choose the correct version of the editable PDF form from the list and get started filling it out.
| Versions | Form popularity | Fillable & printable |
|---|---|---|
| HIPAA Authorization For Release Of Information 2016 | 4.7 Satisfied (86 Votes) |
Recommended authorization setup
Configure this workflow around signer verification, precise disclosure scope, audit evidence, and documented HIPAA retention responsibilities.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enabled with completion certificate |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
Retention schedule for authorization records
Retain this authorization according to HIPAA, state privacy rules, and the covered entity’s documented record schedule; six years is the HIPAA federal minimum for required policies and procedures.
Six years for HIPAA records
Organization health-record policy
State law review
Signed authorization evidence
Revocation and expiration records
Security for health information
HIPAA safeguards:
Encrypted storage:
Secure transmission:
Independent controls:
Information security:
Completion evidence:
Privacy and disclosure pitfalls
The authorization may name recipients too broadly, allowing disclosure beyond the person or entity identified in Section B. Sensitive health information can remain exposed when unnecessary diagnoses, treatment details, or identifiers are included in the signed document. Missing signature dates, expiration terms, or revocation instructions can make the authorization difficult to administer consistently. Unrestricted staff access to completed authorizations can expose PHI beyond the workforce members assigned to process the disclosure.
Best practices for this authorization
Use precise scope, controlled preparation, documented review, and defensible retention when processing this health information authorization.
Limit Section B recipients and scope
Control the approved template
Retain evidence for six years
Verify before releasing PHI
Real-world authorization workflows
Healthcare and legal teams use structured authorization workflows to connect signer consent with recipient verification and controlled disclosure processing.
Healthcare administration
Fertility Centers of Illinois needed dependable patient-facing workflows for health-related documents and information exchange.
- Patient authorization routing
- API-connected document handling
Founder John Butler reported that the signNow team was responsive and that its API worked well for Fertility Centers of Illinois. For a Section A and Section B authorization, a comparable configured workflow can route patient consent, preserve completion evidence, and connect the signed record with controlled internal processing.
Legal services
A regional legal-services practice needed signed health-information authorizations from clients before coordinating records with medical providers.
- Named recipient verification
- Audit trail retention
Using signNow for this scenario would let the practice upload the authorization, place fields for the authorizer and designated recipient, send the document electronically, and retain the signed PDF with its completion history. The practice would still need to review HIPAA obligations, state law, and client-specific disclosure scope.
Troubleshooting this authorization
Use these targeted checks when preparing, sending, signing, or retaining this health information authorization.
Question: Why does the signer receive an access error? Answer: Confirm the email address and signing link, then resend the request from signNow. Business includes legally binding eSignatures and audit trails. If the authorization contains PHI, the organization must also apply its HIPAA policy and verify that a BAA is required for the deployment.
Question: Does signNow support HIPAA workflows for this authorization? Answer: signNow lists HIPAA compliance with a BAA required. Configure access, authentication, retention, and workforce permissions through the organization’s compliance program; the platform does not replace the covered entity’s HIPAA authorization procedures or minimum-necessary review.
Question: Can I change Section B after sending? Answer: Do not alter recipient names or disclosure scope after signature. Void the existing request, correct the authorization, and send a new document so the audit trail clearly connects the signer’s consent with the final Section B language.
Question: Which signNow plan supports audit trails? Answer: The Business plan includes audit trails, templates, mobile apps, and legally binding eSignatures at $8 per user per month when billed annually. Confirm that the selected plan and organizational controls meet the healthcare provider’s HIPAA and record-management requirements.
Question: Is an electronic signature legally effective here? Answer: ESIGN, 15 U.S.C. chapter 96, and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are established. Consumer-facing records may require an ESIGN disclosure under 15 U.S.C. §7001(c), while HIPAA authorization requirements still apply.
Question: Why is the completed PDF missing a field? Answer: Upload the correct authorization file, review signNow’s detected fields, and add or reposition fields manually before sending. Confirm that Section A, Section B, signature, date, purpose, and expiration information remain visible in the final signed copy.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.