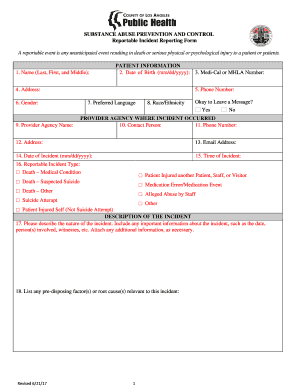
Reportable Incident Reporting Form
Use a Reportable Incident Reporting Form template to make your document workflow more streamlined.
What the Reportable Incident Reporting Form does
The Reportable Incident Reporting Form records what happened, who was affected, how the event was reviewed, and which corrective action followed. It is used by organizations that need a consistent incident record rather than scattered email statements. A sender uploads the form to signNow, checks or adds fields for dates, descriptions, witnesses, reviewers, and acknowledgments, then sends it to the designated participants. Each signer reviews and signs electronically, while signNow preserves the completion record and audit trail for controlled storage and later investigation.
Business types that use incident reports
The Reportable Incident Reporting Form fits organizations that need a documented account, reviewer acknowledgment, and controlled evidence of follow-up.
A solo healthcare practice can route a patient-safety incident to its clinician owner, capture acknowledgment, and retain the signed report without purchasing a separate document system. A regional employer can standardize workplace incident reports across locations, assign supervisors as reviewers, and preserve role-based evidence for each completed investigation. An enterprise compliance department can connect incident reporting to controlled repositories, use templates for repeat events, and manage access through centralized signNow administration.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How to complete the incident report
Follow the report from initial upload through signed acknowledgment without changing the original factual record.
Upload report: Upload the incident report PDF. Prepare fields: Auto-detect fields and add missing incident details. Route report: Send the report to assigned reviewers. Complete record: Collect signatures and preserve the audit trail.
How the incident audit trail works
The audit trail records who handled the Reportable Incident Reporting Form, which actions occurred, and how the completed record can be reviewed later.
Authenticate signer:
Timestamp event:
Hash document:
Seal record:
Store evidence:
Export trail:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Platform requirements for incident reporting
Complete the Reportable Incident Reporting Form in Chrome, Firefox, Safari, or Edge using Windows 10, macOS 12, iOS, or Android.
Windows browsers Chrome and Edge on Windows 10 or later Mac browsers Safari and Chrome on macOS 12 or later Mobile browsers Safari on iOS and Chrome on Android
Use a managed browser and a stable internet connection when incident details contain personal or health information. Organizations can connect signNow through its API, configure SSO provisioning, and apply retention, certificate, or long-term validation controls according to their internal policy.
Security for incident reports
Data in transit:
Data at rest:
Security reporting:
Information security:
Protected health information:
Electronic signatures:
Features for reportable incident workflows
signNow organizes the Reportable Incident Reporting Form from upload through acknowledgment, while preserving the evidence reviewers need to understand the completed record.
Field detection
Upload the Reportable Incident Reporting Form and let signNow identify fillable areas before you add missing narrative, date, initials, and acknowledgment fields.
Controlled routing
Route the incident report to an investigator, supervisor, or affected party in a defined signing order, reducing manual forwarding and missed acknowledgments.
Audit evidence
Capture signer actions, timestamps, and completion evidence in an audit trail linked to the completed incident record.
Reusable templates
Use templates for recurring incident categories while preserving the fields and approval sequence required by your internal policy.
Mobile signing
Collect signatures from a desktop or mobile device, including workflows used at a worksite or during an active response.
Protected records
Store the signed report with its completion certificate and apply access controls appropriate to personal, employment, or health information.
Recommended incident report setup
Configure the Reportable Incident Reporting Form around signer identity, evidence preservation, controlled access, and the retention rule applicable to the incident record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS verification |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion certificate and action log |
| Document retention | Six years for HIPAA records |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
Record-keeping practices for incident reports
Preserve the completed report, signer evidence, and retention decision together so investigators can reconstruct what happened and when.
Export the signed report and audit trail
Restrict access to authorized reviewers
Apply the correct retention period
Separate facts from conclusions
Privacy pitfalls in incident reporting
Including patient names, medical details, or witness statements in an email subject line can expose sensitive incident information before authorized review. Sending a completed report to every department instead of named reviewers can violate least-privilege access and complicate later accountability. Failing to capture electronic consent before a consumer signs can weaken the record’s ESIGN evidence, especially when paper access was not disclosed. Allowing an investigator to edit the original signed report can obscure the factual history; issue a controlled amendment instead.
Troubleshooting incident report workflows
Resolve field, signer, consent, security, and retention issues before the Reportable Incident Reporting Form becomes part of the official incident record.
Upload the original PDF again, then inspect whether its fields are flattened, protected, or embedded as unsupported controls. signNow can auto-detect fillable areas, but a flattened report may require manually placed text, date, initials, and signature fields before sending.
The Business plan includes legally binding eSignatures, templates, and audit trails at $8/user/month with annual billing. Business Premium adds bulk send at $15/user/month. Select the plan based on this form’s volume and routing needs.
For a consumer-facing report, provide the ESIGN disclosure required by 15 U.S.C. §7001(c), including paper-record access and consent withdrawal procedures. Capture affirmative consent before signing, then retain the disclosure with the completed form.
Use signNow authentication settings that match the report’s sensitivity. Email delivery identifies the recipient, while SMS codes or stronger authentication can add identity evidence. Enterprise includes advanced signer authentication; document the selected method in policy.
signNow provides audit trails and completion records, while HIPAA compliance requires a business associate agreement when protected health information is handled. Apply six-year retention from creation or last effective date under 45 CFR 164.530(j).
If a signer cannot open the invitation, confirm the email address, resend the request, or generate a signing link when appropriate. The sender should verify the link recipient before sharing an incident report containing personal information.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.