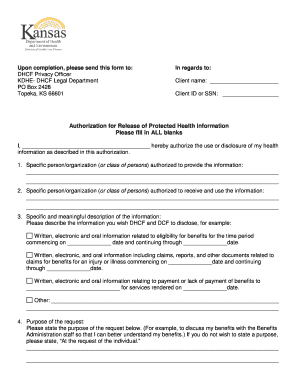
Authorization For Release Of Protected Health Information Kdhe Kdheks
Use a Authorization For Release Of Protected Health Information KDHE Kdheks template to make your document workflow more streamlined.
What this authorization does
An Authorization For Release Of Protected Health Information Kdhe Kdheks lets a patient permit a named healthcare provider or other holder to disclose specified protected health information to an identified recipient. The document should state the information covered, disclosure purpose, recipient, signature, date, and expiration or revocation terms. With signNow, a sender uploads the authorization, places or auto-detects fillable fields, assigns patient and recipient roles, sends the document, and retains the completed PDF with its audit trail. HIPAA’s administrative-record rule requires six years from creation or the last effective date under 45 CFR 164.530(j).
Who uses this health authorization
Healthcare providers
Patients authorize a healthcare provider, insurer, attorney, family member, or another named recipient to receive specified protected health information. The authorization identifies the information, purpose, recipient, signature, and effective period so staff can evaluate the requested disclosure before releasing records.
Records departments
Medical-records departments and compliance teams send, verify, and archive the authorization. They use signNow to assign patient fields, collect electronic signatures, preserve the audit trail, and keep the completed record with the patient’s disclosure documentation.
How this authorization works
The authorization moves from document preparation to signed consent and retained evidence through four controlled signNow actions.
Upload form: Upload the authorization PDF Detect fields: signNow identifies fillable fields Assign parties: Add the patient and recipient Complete record: Send, sign, and retain evidence
Complete this authorization in signNow
Prepare the Authorization For Release Of Protected Health Information Kdhe Kdheks in signNow using the document’s actual patient, recipient, scope, and signature fields.
Upload:
Upload the authorization PDF Check fields:
Review detected fields Assign roles:
Assign patient and recipient Send:
Send for electronic signatures Archive:
Store the signed record
Features for authorization workflows
signNow connects field preparation, patient signing, recipient routing, audit evidence, and retention for this protected-health-information authorization.
Field placement
Upload the Authorization For Release Of Protected Health Information Kdhe Kdheks and place patient, recipient, date, and acknowledgment fields without recreating the document.
Role assignment
Assign the patient and authorized recipient separately so every required signature and date is associated with the correct participant.
Remote signing
Send the authorization by email or signing link when an in-person appointment is unavailable, while preserving the intended signing sequence.
Audit trail
Capture timestamps, participant activity, and completion evidence in an audit trail that can remain with the signed authorization.
HIPAA safeguards
Use signNow encryption and HIPAA compliance with a required BAA when the workflow handles protected health information.
Record retention
Store the completed PDF and audit trail together to support the six-year HIPAA administrative-record period and longer state requirements.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete the authorization on mobile
The signNow mobile apps support iOS 15 or later and Android 10 or later. Users can capture a paper authorization with a device camera, review fields, and sign when connectivity is limited.
iPhone app iOS 15 or later Android app Android 10 or later Mobile workflow Camera capture and offline signing
Healthcare staff should use managed iOS or Android devices, apply organizational access policies, and confirm connectivity before sending protected health information. Camera capture should be limited to approved workflows, while offline work should synchronize only through the signNow application after the device reconnects.



Security for protected health information
HIPAA compliance:
Security report:
Information security:
Transport encryption:
Storage encryption:
Signer authentication:
Challenges when processing this authorization
The authorization names a recipient but does not clearly identify the protected health information or purpose, creating uncertainty before disclosure. A patient signs electronically, but the organization cannot produce the completed form and audit trail when reviewing the disclosure. A shared inbox or unrestricted template exposes patient identifiers to staff without a business need or approved role assignment. The authorization lacks an expiration or revocation process, leaving records staff unsure whether a later disclosure remains permitted.
What the signNow audit trail records
The audit trail documents the authorization’s signing evidence separately from the clinical disclosure decision and supports later record review.
Authenticate signer:
Capture timestamp:
Hash document:
Seal document:
Record activity:
Export evidence:
Recommended authorization workflow setup
Configure the authorization workflow around patient identity, documented consent, secure transfer, and the HIPAA record-retention requirement.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for remote patient signing |
| Signature type | Electronic signature with recorded intent |
| Audit trail | Retain the completed audit trail |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
Best practices for this authorization
Accurate scope, controlled signer assignment, and documented retention reduce disclosure errors when processing this health-information authorization.
Specify the disclosure scope before sending
Assign patient and recipient fields separately
Archive the signed authorization and audit trail
Verify authorization before releasing information
Retention periods for authorization records
Retain each completed authorization according to HIPAA and any longer state healthcare-record requirement that applies to the organization.
Six years from creation
Six years after last effective date
State rule may extend retention
Retain disclosure history
Preserve completion evidence
Troubleshooting this authorization workflow
Resolve signer, scope, account, and privacy questions before releasing protected health information under the completed authorization.
A missing patient signature means the Authorization For Release Of Protected Health Information Kdhe Kdheks is not complete for the intended electronic workflow. In signNow, verify the patient’s assigned signature and date fields, resend the document, and review the completed audit trail after signing.
signNow’s HIPAA compliance requires a business associate agreement when the service handles protected health information for a covered entity or business associate. Confirm that the required BAA is in place before uploading this authorization or related patient records.
The Business plan is listed at $8 per user per month with annual billing and includes audit trails and templates. HIPAA compliance requires a BAA, so confirm the account configuration and contractual requirements before processing protected health information.
If a signer cannot open the document, verify the invitation address, resend the signNow request, or provide a controlled signing link. The signer can often complete the authorization without a signNow account, subject to the workflow’s authentication requirements.
An authorization should state the information categories, recipient, purpose, and expiration or revocation terms required by the applicable disclosure rule. signNow records the signing event, but the healthcare organization remains responsible for accurate legal content.
signNow encrypts data in transit with TLS 1.2 or 1.3 and at rest with AES-256. HIPAA requires appropriate safeguards, but encryption alone does not validate patient consent, disclosure scope, or state-specific authorization requirements.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.