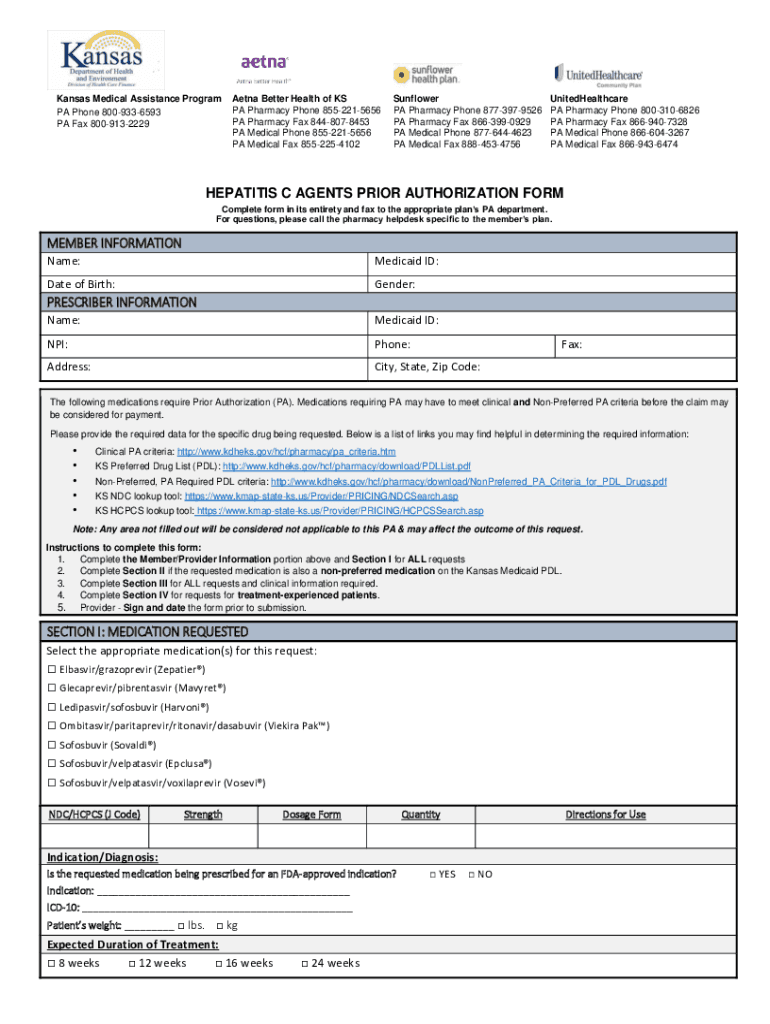
General Prior Authorization Request Kmap State Ks US Form
Use a General Prior Authorization Request Kmap state ks us template to make your document workflow more streamlined.
What this prior authorization request does
The General Prior Authorization Request Kmap State Ks US Form is a healthcare request used to ask a health plan to approve a treatment, service, medication, or procedure before it is provided. The requesting clinician or facility supplies patient identifiers, diagnosis information, requested care, clinical justification, provider details, and supporting records. The plan reviews the submission against coverage and medical-necessity criteria, then returns an approval, denial, or request for more information. Because requirements vary by payer and Kansas program, confirm the applicable instructions before sending the completed form.
Who completes this healthcare request
Healthcare providers
Healthcare providers use the request to submit patient-specific authorization details, diagnosis codes, treatment plans, and supporting clinical documentation to a payer. A clinic can route the form to the responsible provider, utilization-review team, and health-plan contact while preserving the completed record and audit trail.
Care organizations
Hospitals, outpatient centers, pharmacies, and behavioral-health practices use the form when a payer requires approval before care begins. Staff can coordinate clinical attachments, patient consent, provider signatures, and payer responses without recreating the request across email threads.
Features that support authorization requests
signNow organizes the form, required signers, clinical attachments, and completion evidence in one controlled workflow for payer review.
Field preparation
Upload the payer’s PDF and use detected fields as a starting point, then verify every patient, provider, diagnosis, and requested-service field before sending.
Signer routing
Route the request to the clinician, patient, or authorized representative in the required sequence, reducing missing signatures and incomplete submissions.
Audit trail
Capture timestamps, signer actions, and document history so staff can show when the authorization request was completed and transmitted.
Signer verification
Use SMS verification or another configured authentication method when payer policy requires stronger evidence of signer identity.
Secure records
Keep the completed request and certificate of completion together with clinical attachments and the payer’s final response.
Workflow integration
Connect authorization workflows with healthcare systems or storage services to reduce duplicate data entry and controlled-document downloads.
How to complete the request online
Use this sequence to prepare the request, obtain required signatures, and preserve evidence for the payer review.
Upload documents:
Upload the payer-specific request and supporting clinical records. Check fields:
Review detected fields and add missing patient or provider data. Add signers:
Assign the provider, patient, or authorized representative. Send request:
Send the authorization request and monitor completion. Store evidence:
Download the signed request and retain the audit trail.
Ways to send and sign the request
- Use the web app when staff prepare the request, verify fields, assign clinical signers, and monitor payer-related completion from a managed workstation.
- Use the mobile app when an authorized provider or patient must review and sign the request away from the clinic, subject to privacy controls.
- Use kiosk mode for supervised, on-site signing when a facility manages the patient’s signing experience on an organization-controlled device.
- Use a shareable signing link only when access controls and payer policy permit it; avoid exposing patient information through an unrestricted link.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended setup for this request
Configure the request around patient privacy, signer identity, payer review, and documented healthcare-record retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion certificate and action history |
| Document retention | Six years under HIPAA 45 CFR §164.530(j) |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
How the audit trail records approval
The audit trail preserves technical evidence showing who handled this healthcare request, when each action occurred, and whether the record changed.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log actions:
Export trail:
Security controls for patient records
Transport encryption:
Stored encryption:
Health information:
Security assurance:
Information security:
Electronic signatures:
Platform requirements for this form
Complete the General Prior Authorization Request Kmap State Ks US Form through a current Chrome, Firefox, Safari, or Edge browser on Windows or macOS. signNow mobile apps support iOS and Android workflows, while TLS 1.2 or TLS 1.3 protects information in transit.
Browser support Chrome, Firefox, Safari, and Edge on Windows or macOS. Mobile access Android and iOS devices support mobile signing workflows. Connection security TLS 1.2 or TLS 1.3 protects data in transit.
Healthcare organizations should use managed Windows, macOS, iOS, or Android devices when patient information is involved. Configure account access, signer authentication, and retention according to the payer contract, organizational policy, HIPAA obligations, and applicable Kansas requirements. A HIPAA workflow requires a business associate agreement with signNow.



Record-keeping practices for authorization requests
Retain the signed request with its supporting evidence, payer response, and access history under the applicable healthcare record policy.
Preserve the complete authorization packet
Apply the correct HIPAA retention period
Restrict access to patient information
Track payer responses and revisions
Retention periods for authorization records
Use the longest applicable period after checking HIPAA, Kansas requirements, payer contracts, and the organization’s healthcare-record policy.
Six years for HIPAA records
Payer policy period
Signed request packet
Version history
Completion evidence
Privacy pitfalls to check before sending
Patient identifiers and clinical attachments can be exposed when staff use unrestricted signing links or personal email accounts. Missing electronic-consent disclosures can weaken a consumer-facing signing workflow under 15 U.S.C. §7001(c). Incorrect signer routing may leave the provider signature absent while the payer receives an incomplete authorization request. Overwriting a revised clinical request can remove evidence needed to explain what the payer reviewed.
Examples of healthcare authorization workflows
Healthcare teams can adapt the signing workflow to payer-specific clinical documentation and authorization requirements.
Fertility care
Fertility Centers of Illinois represents a healthcare setting where patient-facing documents and clinical workflows require controlled signatures and responsive routing.
- Collect patient and provider signatures
- Preserve completion evidence for records
The customer story identifies Fertility Centers of Illinois as a signNow customer and highlights its API and responsive support. That evidence does not establish a specific prior-authorization result, but it shows how a healthcare organization can adapt controlled signing and record workflows for payer authorization packets.
Kansas clinic
A Kansas outpatient clinic can use the request when a health plan requires clinical justification before a scheduled service.
- Route the form to authorized clinical staff
- Attach payer-requested supporting records
The clinic should verify the payer’s current form, submission channel, and required clinical attachments before sending. signNow can organize the signature sequence and audit evidence, while the payer—not signNow—determines whether the requested service receives authorization.
Troubleshooting this authorization workflow
Resolve field, signer, privacy, legal, plan, and retention questions before the request reaches the payer.
Upload the payer-specific PDF again and check whether the source is image-only or password-protected. signNow can detect fields in supported documents, but staff must verify every detected field before sending clinical information.
Open the signer settings and confirm the assigned email, signing order, and authentication method. Business supports audit trails; stronger authentication options and advanced controls depend on the selected signNow plan and configuration.
A HIPAA workflow requires a business associate agreement with signNow and appropriate administrative safeguards. Confirm the BAA, limit access, and avoid sending protected health information through an uncontrolled link.
ESIGN and UETA support electronic signatures when intent, consent, attribution, and record reproduction are established. Consumer-facing workflows also require the disclosures and access procedures described in 15 U.S.C. §7001(c).
Business is listed at $8 per user per month with annual billing and includes 100 signature invites per user per year. Business Premium is $15 and adds bulk send; confirm overage terms before large payer campaigns.
Export the signed PDF, certificate of completion, and audit trail together, then store them under the healthcare-record policy. HIPAA records require six years under 45 CFR §164.530(j), unless another applicable rule requires longer retention.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.