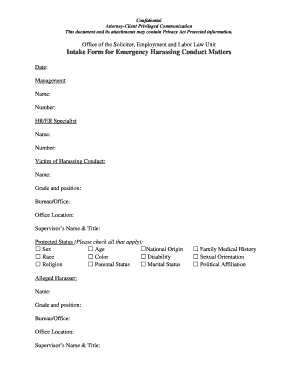
This Document And Its Attachments May Contain Privacy Act Protected Information
Use a This Document And Its Attachments May Contain Privacy Act Protected Information template to make your document workflow more streamlined.
What this privacy notice means
This document is a warning that the document and its attachments may contain information protected under the Privacy Act. It is not, by itself, a standardized federal form, tax return, authorization, or filing with a stated issuing agency. Its purpose is to alert recipients to handle the attached record carefully, limit access, and follow the governing program’s disclosure and retention rules. With signNow, a sender can upload the notice and attachments, place required fields, send them to identified signers, capture an audit trail, and retain the completed record under organizational policy.
Who uses this privacy notice
Government workflows
Government agencies, contractors, and businesses use this notice when a document or attachment contains personal information protected by the Privacy Act. It helps recipients recognize handling restrictions before reviewing, signing, storing, or sharing the record.
Regulated teams
Healthcare, education, legal, human resources, and financial teams can place the notice on records containing personally identifiable information. It prompts authorized access, careful transmission, and retention under the document’s governing policy.
How to complete this notice
Follow the source record’s instructions while using signNow to prepare, route, sign, and preserve the protected-information notice.
Upload documents: Upload the notice and its attachments. Prepare fields: Review detected fields and add required signers. Send request: Send the protected-information notice securely. Archive evidence: Store the signed record with its audit trail.
Features for protected-information documents
signNow supports the document preparation, controlled signing, audit evidence, and retention workflow needed for this privacy notice and its attachments.
Document context
Upload the notice and its attachments together, then review the file before adding recipients. Keeping related records in one signing request helps preserve the notice’s context during completion.
Field review
Auto-detect fillable fields where available, then verify every field against the source document. Manual review remains necessary because this notice has no universal federal field layout.
Controlled routing
Assign each required signer by role and sequence. Role-based routing helps prevent an unauthorized recipient from signing or receiving a protected attachment before the responsible reviewer acts.
Audit trail
Capture signing activity, timestamps, and completion history in an audit trail. Preserve that evidence with the signed notice instead of treating the signature image as the entire record.
Mobile access
Use signNow’s mobile apps when authorized personnel must review or sign away from a desk. Mobile access can support field operations without removing the organization’s disclosure controls.
Secure storage
Store completed documents with access restrictions and the applicable retention policy. signNow encryption supports secure transmission and storage, while the organization remains responsible for governance.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Legal standing of the notice
The notice is evidence of a handling instruction, not automatic proof that an attachment is admissible or authorized for disclosure. Electronic signing can satisfy ESIGN and UETA requirements when intent, consent, attribution, and record retention are established. Wills, codicils, testamentary trusts, court orders, and family-law decrees remain outside those federal electronic-signature rules.

Quick completion guide
Prepare this notice with its attachments in signNow, verify each recipient, and preserve the completed record with its audit trail.
Upload files:
Upload the notice and attachments. Review fields:
Check detected fields manually. Assign recipients:
Add authorized recipients and signers. Complete workflow:
Send, sign, and download the completed record.
What the audit trail records
The audit trail supplements the protected-information notice by documenting signing activity and completion evidence for the underlying record.
Signer authentication:
Timestamp capture:
Document history:
Tamper evidence:
Activity log:
Audit export:
Security controls for protected records
Transport encryption:
Storage encryption:
Security certification:
Management certification:
Health data protection:
Signature compliance:
Recommended workflow configuration
Configure access, signing evidence, encryption, retention, and user roles around the underlying protected-information record.
| Setting | Recommendation |
|---|---|
| Authentication method | Two-factor authentication for authorized signers |
| Signature type | Electronic signature under ESIGN and UETA |
| Audit trail and encryption | Detailed audit trail with TLS 1.2/1.3 and AES-256 |
| Document retention | Follow the underlying agency or program policy |
| User provisioning | Role-based access for approved recipients |
Record-keeping practices for protected notices
Treat the notice as part of the underlying record, preserving access evidence, retention authority, and secure handling controls.
Retain the notice with its source record
Export the audit trail after signing
Limit access to authorized recipients
Archive completed records securely
State rules and document exclusions
State notarization
Wills excluded
Family law
Real-estate deeds
Troubleshooting protected-information workflows
Use the underlying record’s handling policy to resolve legal questions, then use signNow controls to document the signing event securely.
This notice does not identify a universal signature requirement. In signNow, upload the notice with its attachments, inspect the source document’s instructions, and add only the fields required by the responsible agency, contract, or internal policy. Do not infer an agency approval from the notice alone.
The Privacy Act notice does not establish a single retention period. Keep the signed notice with the underlying record and apply the controlling agency policy, contract, or sector rule. For HIPAA documentation, 45 CFR 164.530(j) requires six years, when that rule applies.
A signNow audit trail records signing activity, timestamps, and completion history, but it does not determine whether disclosure is legally permitted. Confirm each recipient’s authorization and apply the source program’s Privacy Act, HIPAA, FERPA, or contractual access rules.
If the attachment contains protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm that the organization has the required BAA and configure access controls before sending the notice or attached record.
Business includes legally binding eSignatures, audit trails, templates, and mobile apps at $8 per user per month when billed annually. The plan does not replace agency handling rules, and paid subscription plans include 100 signature invites per user annually.
If a recipient cannot open the signing request, verify the email address, resend the invitation, or provide an approved signing link. Do not send an unprotected attachment through an alternative channel unless the responsible policy permits that transfer.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.