Cciso Exam Eligibility Application Form Certified Ciso Ec
Use a CCISO Exam Eligibility Application Form Certified CISO EC template to make your document workflow more streamlined.
What the CCISO eligibility application does
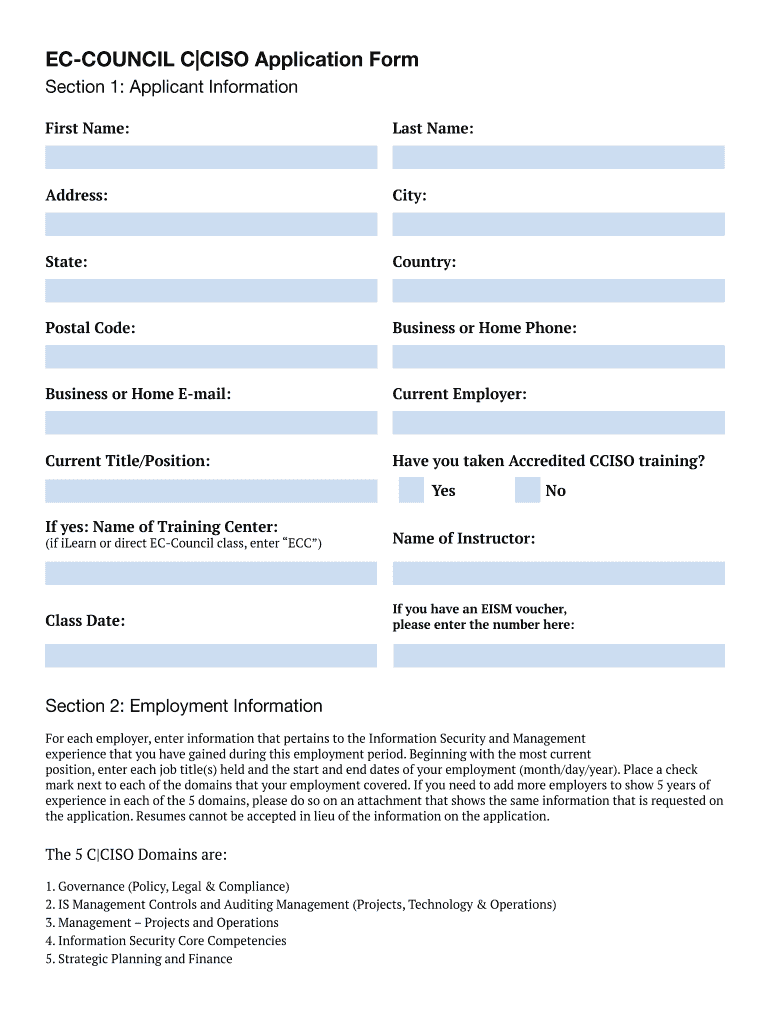
The C|CISO Exam Eligibility Application Form is used to organize an applicant’s information for review before pursuing the Certified CISO examination. It captures the applicant’s identifying details, professional background, education, experience, and supporting declarations in one record. The form itself does not award certification or replace any examination requirement; the responsible certification body determines eligibility and next steps. With signNow, a prepared copy can be uploaded, its fillable fields detected, routed to the applicant or authorized reviewer, signed electronically, and retained with an audit trail.
Who benefits from this application workflow
The form is most useful where an applicant and an authorized reviewer must maintain a clear, signed eligibility record.
Individual cybersecurity professionals can organize identity, education, employment, and experience details before submitting a C|CISO eligibility application for review. Corporate security teams can route applications through designated managers, preserve approval evidence, and keep each applicant’s completed record separate. Training or certification administrators can use templates, controlled access, and audit trails to manage repeated eligibility applications without changing applicant-specific information.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the application workflow works
The signNow workflow keeps preparation, applicant review, electronic signing, and evidence preservation in a defined sequence.
Upload application: Upload the C|CISO eligibility application into signNow. Review fields: Auto-detect fields and correct field assignments. Route document: Send the application to the designated applicant. Preserve evidence: Store the signed record with its audit trail.
Complete and sign the application
Prepare the C|CISO eligibility application first, then use signNow to detect fields, route the document, capture the signature, and preserve completion evidence.
Upload form:
Upload the completed C|CISO application. Detect fields:
Let signNow detect fillable fields. Assign signer:
Review fields and add the applicant. Send form:
Send the application for signature. Save evidence:
Store the signed file and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended application workflow settings
Use controlled identity, signing, retention, and access choices when routing the C|CISO eligibility application through signNow.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP with admin-managed users |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable detailed signing history |
| Document retention | Retain by certification policy |
| Encryption | AES-256 at rest and TLS 1.2/1.3 in transit |
How the application audit trail is created
The audit trail documents the C|CISO application’s signing evidence separately from the steps used to prepare and route the form.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log activity:
Export evidence:
Privacy risks in the application workflow
Including personal identifiers or unrelated employment records can expose more applicant information than the C|CISO eligibility review requires. Sending the application before capturing required consent or signature evidence can leave the reviewer unable to confirm applicant approval. Leaving completed applications accessible to every workspace user may disclose certification history beyond the authorized review team. Using an unrestricted signing link can allow an unintended recipient to open or sign the C|CISO application.
Recordkeeping practices for the application
Retention should follow the certification body’s instructions and the organization’s documented records policy because no universal period is established here.
Set the retention rule before signing
Export the audit trail promptly
Limit access to authorized reviewers
Separate corrections from signed records
Application processing stages
The C|CISO application moves from document preparation through signer delivery, completion, and evidence preservation.
Prepare the document
Deliver to signer
Collect signature
Archive completion



Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

Troubleshooting the C|CISO application
Use these answers to resolve plan, signing, privacy, and recordkeeping questions before submitting the eligibility application.
Business is signNow’s entry plan at $8 per user per month when billed annually. It includes templates and audit trails, so a prepared C|CISO application can be routed and evidenced without moving to Business Premium. Month-to-month pricing is $20 per user per month.
Business Premium adds bulk send at $15 per user per month when billed annually. That feature matters when an administrator must distribute substantially similar C|CISO application packages to multiple applicants; it is not necessary for one individually prepared application.
The C|CISO application may contain professional and identity information. signNow lists HIPAA compliance as requiring a business associate agreement, but HIPAA applies only when protected health information is involved; it does not independently govern a certification application.
For U.S. transactions, ESIGN recognizes electronic signatures when intent, consent, attribution, and record retention are established. UETA generally governs intrastate transactions in adopting jurisdictions. Review the certification body’s own submission rules before relying on an electronic signature.
If a recipient cannot open the application, confirm the email address, resend the invitation, or use an approved signing link. Check that required fields were assigned to the correct signer and that the document was not replaced after field placement.
Completed records should include the signed C|CISO application, attachments, certificate of completion, and audit trail. signNow supports audit trails and document history, but the appropriate retention period comes from the organization’s certification, employment, contractual, or records policy.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.