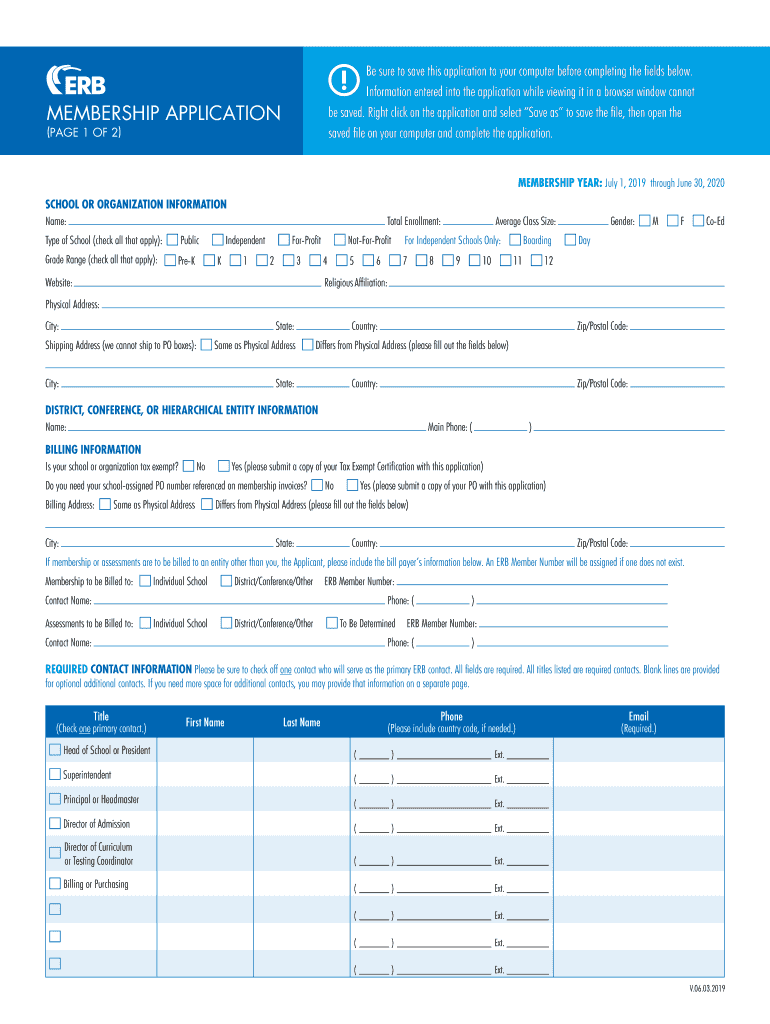
Information Entered Into The Application While Viewing It In A Browser Window Cannot
Use a Information Entered Into The Application While Viewing It In A Browser Window Cannot template to make your document workflow more streamlined.
What browser-entered information means
Information Entered Into The Application While Viewing It In A Browser Window Cannot identifies information that a person enters into an application while viewing it in a web browser, rather than completing a separately downloaded paper record. In signNow, the sender uploads the source document, places or confirms fillable fields, assigns recipients, and sends the application for completion. The signer opens the browser session, enters the requested information, reviews the record, and applies an electronic signature when authorized. The completed document and audit trail can then be retained together for business records and later review.
Who uses this browser-based application
Operations teams
Staff enter application data, obtain signatures, and retain the completed record with its audit trail.
Regulated organizations
Healthcare, financial, legal, and government teams apply access controls when browser-entered information contains sensitive data.
Recommended setup for browser-entered information
Configure the browser workflow around signer identity, signature evidence, access control, and retention requirements for the completed record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP addresses, and actions |
| Document retention | Retain signed records under applicable policy |
| User provisioning | Assign role-based access through administrators |
How the browser completion flow works
The signNow process moves this application from source document to completed, auditable record through four controlled actions.
Upload: Upload the source application Map fields: Auto-detect or place fillable fields Send: Assign recipients and send Finish: Complete, sign, and retain evidence
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail preserves evidence about who interacted with the browser-entered application, what actions occurred, and when the record was completed.
Signer authentication:
Timestamp capture:
Document integrity:
Tamper evidence:
Event attribution:
Trail retrieval:
Security and data protection
TLS protection:
AES-256 encryption:
HIPAA compliance:
SOC 2 Type II:
ISO 27001:
Two-factor authentication:
Platform requirements for browser completion
Complete this application through a supported browser using a secure TLS connection. signNow supports Chrome, Firefox, Safari, and Edge on Windows and macOS, with mobile access available on iOS and Android.
Desktop browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Secure connection TLS 1.2 or TLS 1.3
Organizations should use managed Windows, macOS, iOS, or Android devices when the application contains personal or regulated information. Confirm that browser updates, access controls, authentication settings, and storage policies align with the organization’s requirements before distributing the completed record.
Key features for this application workflow
signNow connects field completion, signer routing, electronic signatures, and audit evidence for applications completed inside a browser window.
Field mapping
Upload the application and use detected or placed fields so signers know exactly where browser-entered information belongs.
Recipient routing
Send the application to named recipients by email, allowing each person to complete assigned fields in sequence.
Electronic signing
Use typed or drawn signatures where the signer has authority and electronic signing is legally appropriate for the transaction.
Audit evidence
Capture timestamps, IP information, and action history to connect the completed application with its signing events.
Data protection
Protect information in transit with TLS 1.2 or 1.3 and at rest with AES-256 under signNow’s compliance controls.
Record retention
Retain the final application and supporting audit evidence according to the organization’s recordkeeping policy and applicable law.
Legal standing for browser-entered records
A browser-entered record may support a U.S. transaction when the signer demonstrates intent, consents to electronic records, can be identified, and the record remains reproducible. ESIGN, 15 U.S.C. ch. 96, and applicable state law such as UETA generally recognize qualifying electronic signatures; exclusions include wills, certain court orders, and family-law decrees.

Challenges when entering information in a browser
A sender may map a browser field to the wrong recipient, causing personal information to appear in the wrong signer’s workspace. A signer may complete visible fields but overlook required information, leaving the application incomplete despite a captured signature. An organization may retain the signed document without its audit trail, reducing evidence about identity, timing, and signing actions. A browser session may expose sensitive application data when shared devices, unmanaged accounts, or broad permissions remain enabled.
Best practices for browser-entered information
Accurate field mapping, controlled access, and complete signing evidence help preserve the reliability of this browser-based application record.
Review every field before sending
Match authentication to information sensitivity
Store the signed record with evidence
Limit access before sharing
Troubleshooting browser-entered applications
Resolve field, access, authentication, and evidence issues before treating this browser-entered application as complete.
The browser field is missing. What should the sender do?
Open the source document in signNow, inspect the detected fields, and add any missing text, date, or signature fields manually. Assign every field to the correct recipient before sending. Review the completed document against the source application to confirm that all required information appears.
The signer cannot open the application. What should I check?
Confirm the recipient address, resend the invitation, and ask the signer to use a supported browser with TLS 1.2 or 1.3 enabled. If organizational controls block the session, an administrator should review account permissions and browser restrictions without forwarding sensitive application information through unsecured channels.
Can this application use SMS authentication?
Yes. signNow supports two-factor authentication options, including SMS one-time passwords where configured. Select the authentication requirement before sending and confirm that the signer’s phone number is accurate. Stronger authentication may be appropriate when the application contains personal, financial, healthcare, or government information.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.