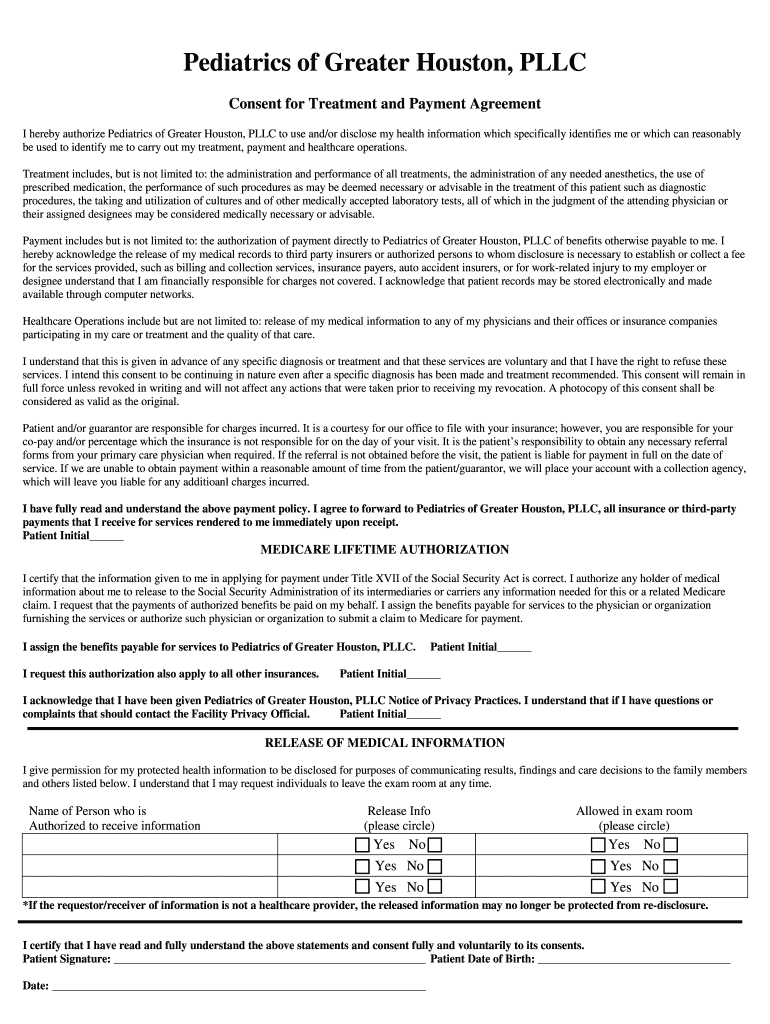
Consent For Treatment And Payment Agreement Consent Form
Use a Consent For Treatment And Payment Agreement Consent Form template to make your document workflow more streamlined.
What this consent agreement does
The Consent For Treatment And Payment Agreement Consent Form records a patient’s permission for treatment and acknowledgment of payment responsibilities. It typically connects the patient or authorized representative with a healthcare provider before care proceeds, while the organization supplies the specific treatment, billing, privacy, and financial language. With signNow, the provider uploads the agreement, reviews automatically detected fillable fields, assigns the patient or representative, sends the document, and preserves the signed copy with an audit trail. HIPAA-covered records generally require six-year retention under 45 CFR §164.530(j).
Organizations that use this agreement
Treatment providers, clinics, and health systems use this agreement when patient consent and payment acknowledgment must be documented before or during care.
A solo medical practice can send treatment and payment agreements from a reusable template, collect patient signatures remotely, and retain the completed record with an audit trail. A multi-location clinic can route agreements to patients or authorized representatives, apply role-based access, and standardize consent evidence across offices while using HIPAA-compliant controls. An enterprise health system can connect agreement workflows with administrative systems, manage delegated sending, and apply centralized retention and authentication policies across high-volume patient intake.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the consent agreement works
The consent agreement moves from document preparation to authenticated signing and organized record storage.
Upload document: Upload the consent agreement and review detected fields before requesting signatures. Add signers: Assign patient or representative fields and set the signing order. Request signatures: Send a secure invitation for review, consent, and electronic signature. Archive record: Store the completed agreement with its certificate and audit trail.
What the audit trail records
For this treatment and payment agreement, the audit trail preserves identity, timing, document integrity, and retrieval evidence separately from the agreement text.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Connect evidence:
Export trail:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended consent workflow setup
Configure the treatment and payment agreement around signer identity, electronic intent, protected information, audit evidence, and the retention rule that applies to the completed record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email invitation with SMS verification |
| Signature type | Electronic signature with intent record |
| Audit trail | Enabled with completion certificate |
| Document retention | Six years under HIPAA 45 CFR §164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
Features for treatment and payment consent
signNow combines field preparation, signer routing, audit evidence, and protected storage for the specific treatment and payment agreement workflow.
Field detection
Upload the agreement and review automatically detected fields before assigning patient, representative, provider, and date fields.
Remote signing
Send the treatment and payment agreement by email or secure signing link without requiring every signer to create an account.
Signer routing
Use signing order when a patient and authorized representative must complete separate sections in sequence.
Audit evidence
Capture timestamps, signer actions, and completion evidence for the completed consent record.
Data protection
Protect agreement data with TLS 1.2/1.3 in transit and AES-256 encryption at rest.
Reusable templates
Reuse an approved agreement template while preserving organization-specific treatment, billing, and privacy language.
Security for signed agreements
Transport encryption:
Stored data:
Security reporting:
Security certification:
Healthcare compliance:
Signature compliance:
Mobile options for consent signing
The signNow iOS and Android apps let healthcare staff and patients review and sign the Consent For Treatment And Payment Agreement Consent Form from a mobile device. Camera-based capture can convert a paper agreement into a document for preparation.
iOS app signNow iOS app supports mobile agreement review and signing. Android app signNow Android app supports mobile agreement review and signing. Camera capture Camera capture supports scanning paper consent documents.
Organizations should manage mobile access through approved devices, identity controls, and documented privacy procedures. Healthcare workflows may require a business associate agreement, controlled permissions, and retention policies aligned with HIPAA obligations. Confirm offline behavior, connectivity, and local storage expectations before deploying the form in patient-facing operations.
Processing the consent agreement
Processing depends on document readiness, signer access, and healthcare organization policy; no universal statutory turnaround period applies to this agreement.
Prepare document
Deliver to signers
Collect signature
Archive completion
Retention rules for signed records
Retention depends on the record’s role and the healthcare organization’s obligations; apply the rule that actually covers the completed agreement.
HIPAA requires six years from creation or last effective date under 45 CFR §164.530(j).
Use three years from filing under IRC §6501(a) only when the agreement is a tax record.
Retain payroll-related records for three years under 29 CFR §516.5 when applicable.
Retain applicable injury records for five years following the year under 29 CFR §1904.33.
Retain applicable workplace exposure records for thirty years under 29 CFR §1910.1020.
Privacy pitfalls to prevent
Including diagnosis details or payment information beyond the agreement’s purpose can expose protected health information to unnecessary recipients. Failing to capture the patient’s electronic-record consent can weaken evidence that the signer intended to use an electronic agreement. Leaving completed agreements available to broad teams can violate minimum-necessary access practices for protected health information. Sending the form before checking signer roles can leave a representative’s authorization or required acknowledgment undocumented.
Record-keeping practices for consent
A defensible record combines the signed agreement, audit evidence, controlled access, and a retention schedule tied to the agreement’s actual healthcare purpose.
Confirm the applicable retention rule
Export the complete evidence set
Limit access to authorized staff
Archive the final agreement securely
Consent agreement troubleshooting
These answers address field setup, healthcare privacy, electronic-consent evidence, plan limits, signing order, and statutory exclusions for this agreement.
On the Business plan, upload the agreement, review signNow’s detected fields, and manually place any missing signature, date, or acknowledgment fields. Test the completed document before sending so the patient or representative cannot bypass required consent sections.
For patient information, use signNow’s HIPAA-compliant configuration with a business associate agreement when required. HIPAA compliance does not replace the healthcare organization’s own privacy notice, minimum-necessary access controls, or state-specific consent requirements.
Use signNow’s audit trail and completion certificate to document signer identity, timestamps, actions, and the final agreement. Under ESIGN and UETA, enforceability still depends on intent, consent to electronic records, attribution, and reliable retention and reproduction.
Business includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month when billed annually. Subscription plans include 100 signature invites per user per year, so review usage and overage terms before large patient campaigns.
If a representative must sign after the patient, assign both signers and configure the required order before sending. The recipient should review treatment and payment language, complete required fields, and receive the finished agreement and audit evidence.
Do not use electronic signing alone for wills, codicils, testamentary trusts, or covered court filings. The ESIGN Act excludes those categories, while this healthcare agreement may generally use electronic signatures when applicable consent and state-law requirements are satisfied.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.