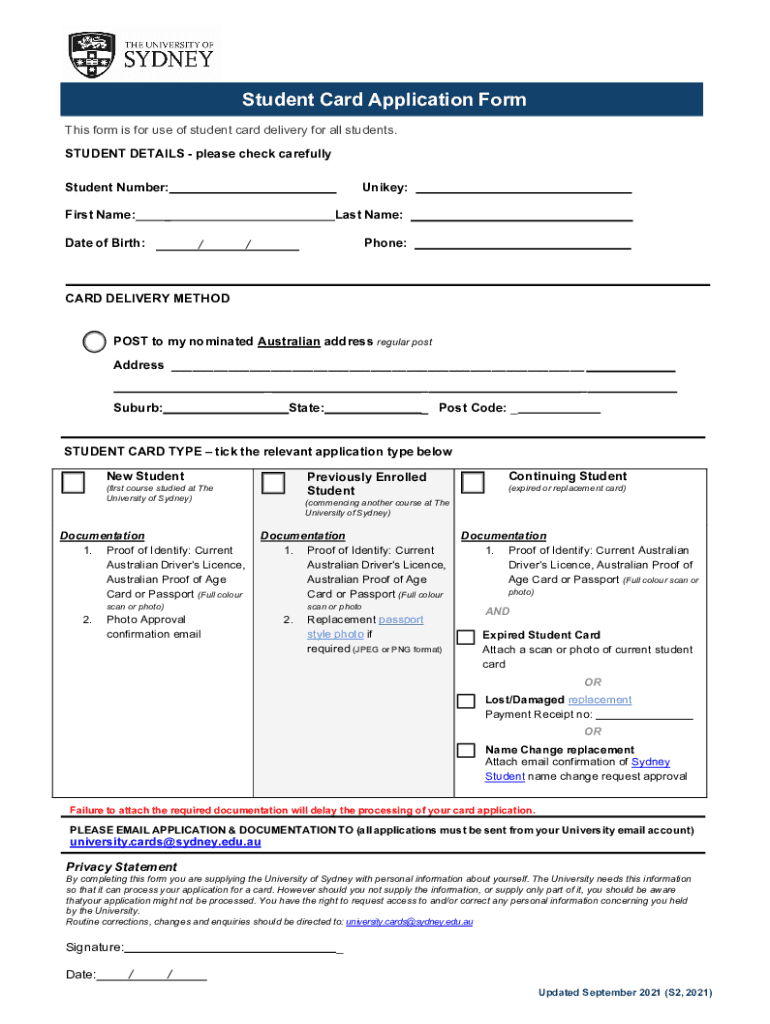
Student Card Application Form The University Of Sydney
Use a Student Card Application Form The University Of Sydney template to make your document workflow more streamlined.
What this student card application is
The Student Card Application Form The University Of Sydney is an application record used by a student to request or manage a university student card. It collects the information required by the University of Sydney’s process, then may be reviewed by an authorized university office. With signNow, a sender uploads the form, checks detected fields, assigns applicant and reviewer roles, and sends the document for completion. The finished form can be returned with an audit trail showing delivery, access, signing, and completion events. Specific eligibility fields and submission requirements remain governed by university instructions.
Who uses this student card form
Students
Students can complete the university’s student card application digitally, review entered details, and provide any required acknowledgment before returning it to the appropriate university office.
University offices
University departments can route applications for review, maintain consistent records, and retain completed copies with an activity history for administrative follow-up.
How the student card workflow works
The workflow moves the University of Sydney student card application from document preparation through signature, return, and documented storage.
Upload form: Upload the University of Sydney student card application document. Check fields: Review detected fields and add missing applicant details. Send application: Send the completed application to the designated university recipient. Archive record: Store the signed copy with its audit trail.
Recommended student card workflow setup
A controlled setup keeps applicant information accurate, routes the form to the right university recipient, and preserves evidence of completion.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with signing intent |
| Audit trail | Export completed certificate and activity history |
| Document retention | Follow University of Sydney records policy |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail documents how the University of Sydney student card application moved from invitation to completed electronic record.
Signer authentication:
Timestamp capture:
Document integrity:
Tamper evidence:
Action history:
Audit export:
Platform requirements for applicants
Applicants can access the University of Sydney student card application through signNow using Chrome, Firefox, Safari, or Edge on Windows or macOS, with signNow mobile apps available for iOS and Android. Secure transmission uses TLS 1.2/1.3.
Browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android SignNow apps signNow web and mobile apps
University administrators should use managed accounts and approved devices when handling applicant information. Teams can connect signNow with Google Workspace, Microsoft 365, Google Drive, Box, or another approved repository, then apply institutional access controls and retention rules.



Security for student card applications
Data at rest:
Data in transit:
Security certification:
Security management:
Privacy compliance:
Signature compliance:
Challenges when completing this form
Applicant names or student identifiers may be entered differently from university records, creating a manual reconciliation step before the card request can proceed. A missing acknowledgment, date, or signature can leave the University of Sydney application incomplete and require the applicant to resubmit information. Sending the completed form to an unapproved recipient can expose student information and conflict with university privacy or access-control requirements. Storing the application without its completion evidence can make later review of delivery, signing, and authorization events more difficult.
Best practices for this application
Accurate field mapping, controlled access, complete audit evidence, and an approved records policy keep this student card application usable after signing.
Verify every field against the source
Restrict access to applicant information
Preserve the audit trail with the form
Apply the university retention policy
Key performance indicators that demonstrate SignNow's proven track record.
Student card application troubleshooting
These answers address field detection, signer access, electronic-signature evidence, privacy, plan selection, and record handling for this university application.
Upload the original University of Sydney student card application as a readable PDF or supported document. If fields are not detected, place them manually and confirm that names, student details, and dates align with the source form before sending.
The signNow Business plan includes templates, audit trails, and mobile apps. If the workflow requires bulk sending to many applicants, Business Premium adds bulk send; select the plan based on the university’s volume and routing requirements.
Use signNow’s audit trail to review timestamps, signer actions, and delivery events. ESIGN and UETA recognize electronic records when intent, consent, attribution, and reliable record retention are established; university policy may impose additional requirements.
For applicant information treated as education records, apply the University of Sydney’s applicable privacy and records policies. FERPA may apply to U.S. educational institutions, while Australian privacy obligations may govern this university’s records.
If the signer cannot open the invitation, verify the email address, resend the request, or provide a controlled signing link. The recipient can usually sign without creating a separate signNow account unless the workflow requires authentication.
The completed form and audit trail should be retained in the university-approved repository. signNow supports export and secure storage workflows, but the University of Sydney must determine the authoritative retention period and access permissions.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.