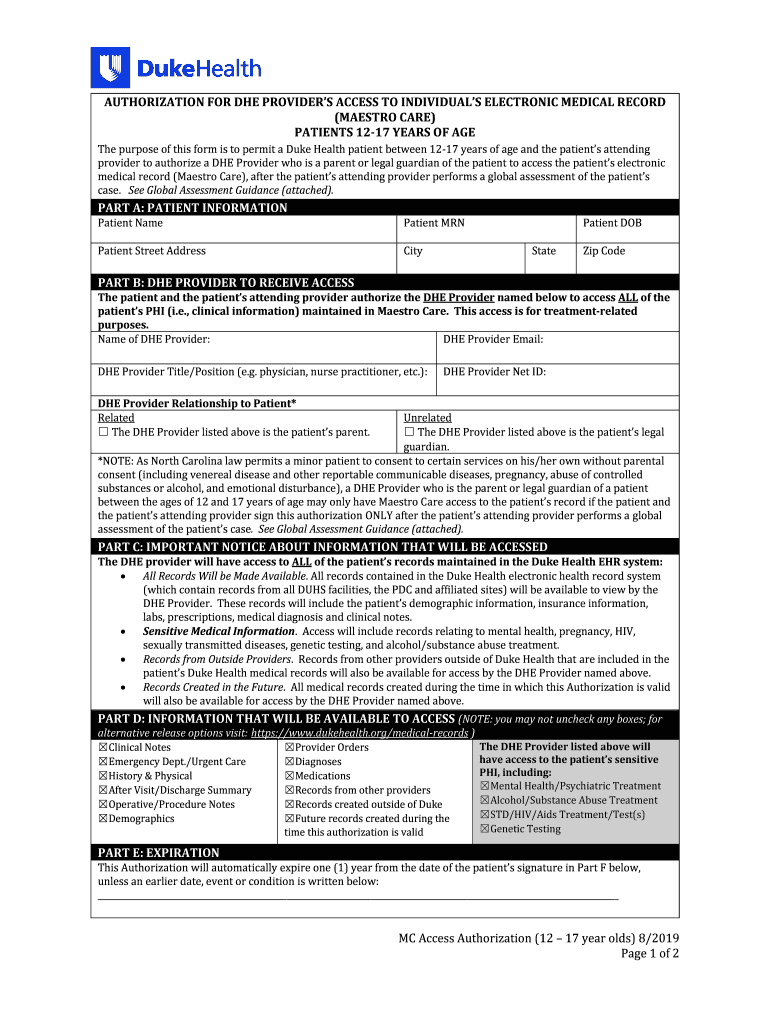
Electronic Medical Record Authorization 12 To 17 Years Of Age Form
Use a Electronic Medical Record Authorization 12 To 17 Years Of Age template to make your document workflow more streamlined.
What this authorization form does
The Electronic Medical Record Authorization 12 To 17 Years Of Age Form documents permission to disclose specified medical records for a patient aged 12 through 17. It identifies the patient, authorized signer, recipient, records or dates covered, purpose, consent, signature, and authorization period. Requirements can depend on the treatment involved, the signer’s authority, HIPAA, and state minor-consent law. In signNow, a healthcare organization uploads the form, checks its fields, routes it to the authorized signer, and retains the completed record with an audit trail.
Who benefits from this authorization workflow
Healthcare organizations use this form to document age-specific consent and control disclosure of medical records.
A pediatric or adolescent clinic can route age-specific medical authorizations to patients, parents, or guardians while preserving the requested disclosure scope and completed audit record. A hospital records department can use reusable fields for provider, recipient, purpose, expiration, and signature information when processing authorizations for patients ages 12 through 17. A multi-site healthcare enterprise can centralize templates, signer permissions, and retention controls while connecting completed authorizations to approved medical-record workflows.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Complete this authorization in signNow
Use this sequence to prepare, route, sign, and retain the authorization without losing consent or audit evidence.
Upload form:
Upload the authorization PDF to signNow. Check fields:
Review auto-detected fields and add missing patient, consent, and signature fields. Assign signers:
Assign each field to the patient, parent, guardian, or other authorized signer. Send and track:
Send the authorization and monitor completion from the signNow workspace. Store record:
Download the completed authorization and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization form setup
Configure the authorization workflow around signer identity, electronic consent, audit evidence, and HIPAA record-retention obligations.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for authorized signers |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, IP addresses, and actions |
| Document retention | Keep six years when HIPAA applies |
| Encryption | AES-256 at rest and TLS 1.2/1.3 |
How the authorization audit trail works
signNow records identity, timing, document integrity, and retrieval details as the 12-to-17 authorization moves through signing.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Retrieve evidence:
Platform requirements for signNow
Use Chrome, Firefox, Safari, or Edge on Windows 11 or macOS, or use the signNow app on iOS and Android to prepare and sign this authorization securely.
Browsers Chrome, Firefox, Safari, Edge Operating systems Windows 11, macOS, iOS, Android Mobile apps iOS and Android signNow apps
Healthcare teams should manage mobile access through approved devices, identity controls, and least-privilege permissions. Enterprise deployments may connect signNow through API access, SSO provisioning, and approved storage integrations. Confirm TLS settings, certificate requirements, and HIPAA safeguards with your organization’s security and compliance teams before handling protected health information.
Security for medical authorizations
HIPAA protection:
Stored encryption:
Transport encryption:
SOC 2 controls:
ISO 27001:
Signer safeguards:
Best practices for this authorization
Accurate patient details, narrow disclosure scope, and preserved signing evidence reduce privacy and consent errors.
Confirm patient and signer identity
Define the requested disclosure scope
Review every field before sending
Preserve authorization evidence securely
Troubleshooting this authorization workflow
Resolve field, signer, privacy, retention, and legal-validity questions before releasing records for a patient ages 12 through 17.
Business includes legally binding eSignatures, templates, and audit trails. For protected health information, signNow identifies HIPAA compliance as requiring a BAA. Confirm your organization’s subscription, BAA, access controls, and disclosure practices before sending this authorization.
Upload the PDF again, then inspect signNow’s automatically detected fields manually. Add missing patient, authorized signer, consent, expiration, and signature fields before sending. Field detection assists preparation but does not determine whether a field is legally required.
A signer may complete the authorization without a signNow account when the invitation permits guest signing. If stronger identity evidence is required, configure SMS OTP or another available authentication control and document the chosen method.
Business is $8 per user per month with annual billing and includes audit trails and templates. Business Premium is $15 per user per month annually and adds bulk send. Confirm plan limits and current pricing before deployment.
HIPAA requires covered entities and business associates to retain certain documentation for six years from creation or the last effective date under 45 CFR 164.530(j). State medical-record rules may require longer retention, so apply the stricter schedule.
ESIGN and UETA generally support electronic signatures when intent, consent, attribution, and reproducible records are established. They do not replace HIPAA authorization content or state minor-consent rules, so review the patient’s care category and jurisdiction.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.