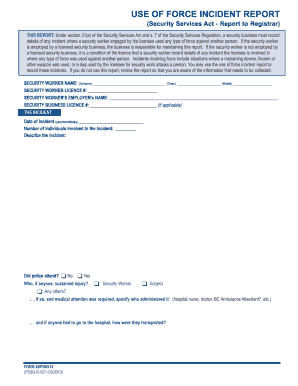
Use Of Force Incident Report SPD0513 Use Of Force Incident Report Security Services Act Report To The Registrar Form
Use a Use Of Force Incident Report SPD0513 Use Of Force Incident Report Security Services Act Report To The Registrar template to make your document workflow more streamlined.
What the SPD0513 report is
The Use Of Force Incident Report SPD0513 is a structured record for documenting a reported use-of-force event and routing it through the responsible organization’s review process. Its exact fields, approval requirements, issuing authority, and filing deadline are not supplied here, so users should follow the current agency-issued form and instructions. In signNow, upload the official document, review or add fields, assign authorized recipients, collect signatures, and preserve the completed PDF with its audit trail. ESIGN and UETA may support electronic signatures where applicable, but they do not replace agency rules or state requirements.
Organizations that manage SPD0513 reports
The right workflow depends on who documents the incident, who reviews it, and which agency controls the completed record.
A municipal police department can use a controlled SPD0513 template to standardize incident details, route supervisor review, and preserve the completed report with an audit trail for authorized records staff. A private security contractor can assign officers and managers distinct permissions, collect signatures after an incident, and retain the final report according to its contract and governing agency requirements. A multi-site public safety organization can centralize templates while delegating sending to approved locations, reducing duplicate versions and giving administrators visibility into completion status without exposing every report to every user.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features that support SPD0513 completion
signNow combines document preparation, controlled signing, audit evidence, and protected storage for teams handling the Use Of Force Incident Report SPD0513.
Form preparation
Upload the official SPD0513 PDF and prepare it without recreating the agency’s incident-report structure from scratch. Detected fields can be reviewed before the document is routed.
Field control
Place signature, initials, date, narrative, and review fields where the source report requires them. Manual field placement helps address fields that automated detection does not identify.
Controlled routing
Route the report to named officers, supervisors, or reviewers in the required order. Recipient assignments reduce the risk of an incomplete approval chain.
Signer authentication
Use email links, SMS OTP, or other configured authentication controls when agency policy requires more than an unauthenticated signing link.
Audit evidence
Capture timestamps, signer actions, and document history through the signNow audit trail. Export this evidence with the completed report for later review.
Secure retention
Protect the completed SPD0513 record with restricted access and encrypted storage. Apply the agency’s retention schedule rather than assuming a universal period.
How to complete SPD0513 online
Use this sequence to prepare, route, sign, and preserve the Use Of Force Incident Report SPD0513 in signNow.
Upload the form:
Upload the official SPD0513 source file. Check the fields:
Review detected fields and add missing fields. Set recipients:
Assign officers, supervisors, and reviewers. Complete the report:
Send, sign, and export the completed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the SPD0513 audit trail records
The audit trail helps connect the completed Use Of Force Incident Report SPD0513 with signer actions, timing, document history, and authorized retrieval.
Signer authentication:
Timestamp capture:
Document history:
Audit export:
Secure archival:
Record verification:
Recommended setup for SPD0513 workflows
Configure the report around controlled identity, traceable approval, protected storage, and the retention policy adopted by the responsible agency.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export with completion certificate |
| Document retention | Agency-approved schedule and legal holds |
| Encryption | TLS 1.2/1.3 and AES-256 |
Security controls for SPD0513 records
Data in transit:
Data at rest:
Security certification:
Information security:
Health information:
Signer verification:



Best practices for the SPD0513 report
Accurate facts, controlled routing, and documented retention help agencies preserve a reliable Use Of Force Incident Report SPD0513 record.
Record every SPD0513 field precisely
Write an objective chronological narrative
Verify routing before sending
Preserve the signed record securely
Challenges when completing SPD0513
Incomplete incident facts or vague force descriptions can make the SPD0513 narrative difficult for supervisors, investigators, or records staff to evaluate consistently. Incorrect signer routing can leave the report unsigned by the officer, supervisor, or agency representative required by internal procedure. Uncontrolled copies in email, local folders, and shared drives can expose sensitive incident details and weaken records-management consistency. Using an outdated or locally altered SPD0513 template can create missing fields, inconsistent terminology, and avoidable review questions.
Risks from mishandling SPD0513
Incomplete approval
Evidence question
Access violation
Review delay
Troubleshooting the SPD0513 signing workflow
Resolve routing, field-detection, authentication, and retention questions before the completed Use Of Force Incident Report SPD0513 is distributed or archived.
Upload the original SPD0513 PDF again, then inspect the document in signNow before sending. If fields are not detected, add signature, date, initials, and text fields manually and compare them with the source form.
The Business plan includes templates, audit trails, and legally binding eSignatures at $8/user/month when billed annually. If the workflow requires bulk sending, Business Premium is the plan identified in the product information as including that feature.
Use signNow’s audit trail to preserve signer actions, timestamps, and document history. ESIGN and UETA provide the federal and state electronic-signature framework, but the agency must still confirm that this report may be signed electronically.
Add the intended signer’s exact email address and verify the routing order before sending. If stronger identity assurance is required, use available authentication controls such as two-factor authentication or SMS OTP according to agency policy.
For sensitive incident information, restrict recipients and repository permissions before sending. signNow lists HIPAA compliance as requiring a BAA, but that framework applies only when protected health information is genuinely involved in the workflow.
A seven-day free trial is available without a credit card, while paid plans include unlimited users. Subscription plans include 100 signature invites per user per year, so review usage before high-volume deployment.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.