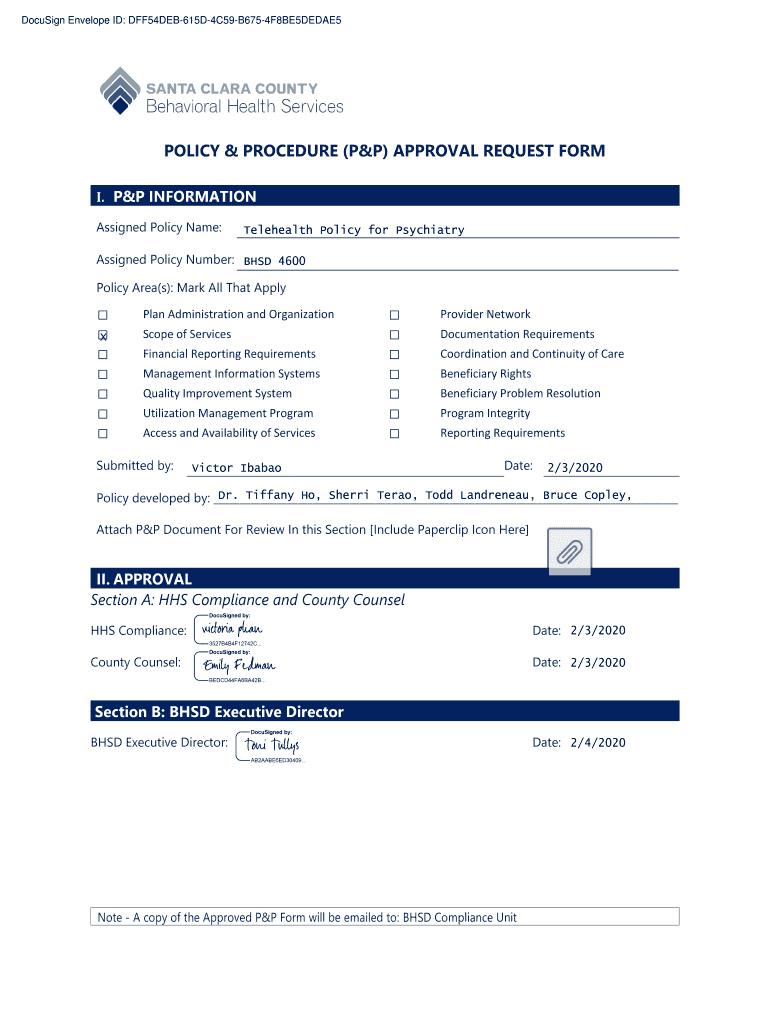
Policy & Procedure P&p Approval Request Form
Use a POLICY & PROCEDURE P&P APPROVAL REQUEST FORM template to make your document workflow more streamlined.
What this approval request form does
The Policy & Procedure P&p Approval Request Form records a proposed policy change, identifies its owner and reviewers, captures approval decisions, and preserves the final authorized version. It is not a government filing or a universal legal form; each organization should define its required fields, routing, effective date, and retention rule. In signNow, upload the request, review auto-detected fields, assign recipients, send it for approval, and store the completed document with its audit trail. ESIGN and UETA may support electronic execution when their consent, attribution, intent, and record-access requirements are met.
Who uses this approval request form
Operations teams
Operations teams use the form to approve revised procedures, employee instructions, vendor requirements, and internal controls. They can route the request to named reviewers, capture decisions, and retain the completed approval record with its audit trail for later policy reviews.
Regulated organizations
Healthcare, construction, financial-services, and legal organizations can adapt the form for controlled policy changes. Each audience should define its own approvers, effective dates, supporting documents, and retention requirements before sending the request for signature.
Who benefits from this approval form
Operations coordinators at growing construction and healthcare organizations use this request form to route policy changes for department review, document accountable approvals, and preserve a signed record before procedures reach employees, contractors, or patients. Compliance leads and office administrators use the form to collect policy-owner decisions, clarify effective dates, and send approved procedures through signNow when several reviewers must complete the same controlled workflow.
Features that support policy approval
The form becomes easier to control when its fields, routing, evidence, versions, and storage location are defined before sending.
Field detection
Upload the request and let signNow detect existing fields before adding missing approval or signature fields.
Role assignment
Assign each approval field to a named reviewer so responsibility for the policy decision is clear.
Approval routing
Use sequential routing when legal, compliance, and operations must review the same policy in order.
Audit trail
Capture timestamps, signer activity, and completion evidence with the request’s audit trail.
Version control
Store the final approved version separately from superseded drafts to support controlled publication.
System connection
Connect completed requests to business systems when the organization needs centralized records or reporting.
How the approval workflow works
The signNow workflow moves this request from a controlled draft to an attributable, stored approval record.
Upload request: Upload the completed approval request. Check fields: Review detected fields and add missing approvals. Route approval: Assign reviewers and send the request. Archive evidence: Store the signed record and audit trail.
Steps to complete the approval request
Use this sequence to prepare, route, sign, and retain the Policy & Procedure P&p Approval Request Form.
Upload:
Upload the request document. Review:
Confirm detected fields and recipients. Send:
Send the approval request. Complete:
Collect signatures and approvals. Store:
Download the audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the approval audit trail records
The audit trail connects each Policy & Procedure P&p Approval Request Form action to a signer, time, document state, and retrievable completion record.
Authenticate signer:
Timestamp actions:
Hash document:
Seal completion:
Record activity:
Retrieve evidence:
Recommended approval workflow setup
Configure the request around accountable reviewers, a reproducible final record, and the retention rule for the approved procedure.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with intent |
| Audit trail | Retain completion certificate and activity log |
| Document retention | Apply the underlying record rule |
| Encryption | TLS 1.2/1.3 and AES-256 encryption |
Best practices for policy approval
A controlled request should show what changed, who reviewed it, which version was approved, and how the final record will be preserved.
Identify the controlled policy clearly
Assign each reviewer’s responsibility
Preserve the approval evidence
Control publication after approval
Privacy and disclosure pitfalls
Personal information included in supporting exhibits may be visible to every recipient unless access permissions and recipient roles are reviewed before sending. An approval request can fail evidentiary review when the signer’s identity, consent to electronic records, or final document version is not clearly documented. Sending a draft procedure instead of the controlled final version can create conflicting instructions and weaken the organization’s change-management record. A missing effective date or policy owner can leave employees uncertain about which approved procedure governs their work.
Risks of incomplete policy approval
Unapproved policy
Version dispute
Signer challenge
Audit gap
Legal standing of electronic approval records
For a business policy approval, an electronic record can support admissibility when the parties intended to sign, consented to electronic records, can be attributed to the signer, and the record remains reproducible. ESIGN and UETA generally recognize those elements, but they exclude wills, certain court orders, and specified family-law documents.

Security controls for approval records
Transport encryption:
Stored encryption:
Security certification:
Management standard:
U.S. eSignature:
Healthcare protection:



Pricing and feature context
signNow pricing and feature details below use the Business plan reference; competitor values are marked Not verified where source data is unavailable.
| Features | signNow | DocuSign | Adobe Sign | PandaDoc |
|---|---|---|---|---|
| Starting price | $8/user/mo annually | Not verified | Not verified | Not verified |
| Free trial | 7 days, no card | Not verified | Not verified | Not verified |
| Bulk send | Business Premium | Not verified | Not verified | Not verified |
| Audit trails | Business included | Not verified | Not verified | Not verified |
| HIPAA support | Compliant with BAA | Not verified | Not verified | Not verified |
Retention periods for approval records
Retention depends on the subject of the approved procedure, not merely the signature date. Apply the rule for the underlying record and verify longer state requirements.
Three years from filing
Six years from creation
Three years for payroll
Five years after year
Thirty years for exposure
Troubleshooting policy approval requests
These answers address field assignment, plan limits, authentication, privacy, delivery, and the legal boundaries of electronic approval.
Upload the final Policy & Procedure P&p Approval Request Form to signNow and inspect the auto-detected fillable fields. Add missing approval, date, or signature fields manually, then assign each field to its intended reviewer before sending.
The Business plan includes templates, audit trails, and legally binding eSignatures. If the workflow requires bulk sending, Business Premium adds bulk send; if it requires advanced signer authentication, Enterprise adds that capability.
Use signNow’s audit trail and completion record to document intent, attribution, timestamps, and the final file. ESIGN and UETA recognize electronic signatures when those legal elements and record-retention requirements are satisfied.
For patient-related procedures, use a signNow HIPAA-compliant workflow with a required business associate agreement. Limit recipients, review attachments, and retain the approved record under the applicable HIPAA policy.
Check the recipient email, assigned fields, routing order, and authentication requirement before resending. A signer may need to reopen the invitation or use the configured SMS OTP rather than a forwarded link.
A signed policy request does not replace excluded transactions. Wills, certain court orders, and specified family-law documents fall outside ESIGN’s general coverage, while state law may impose additional requirements for particular records.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.