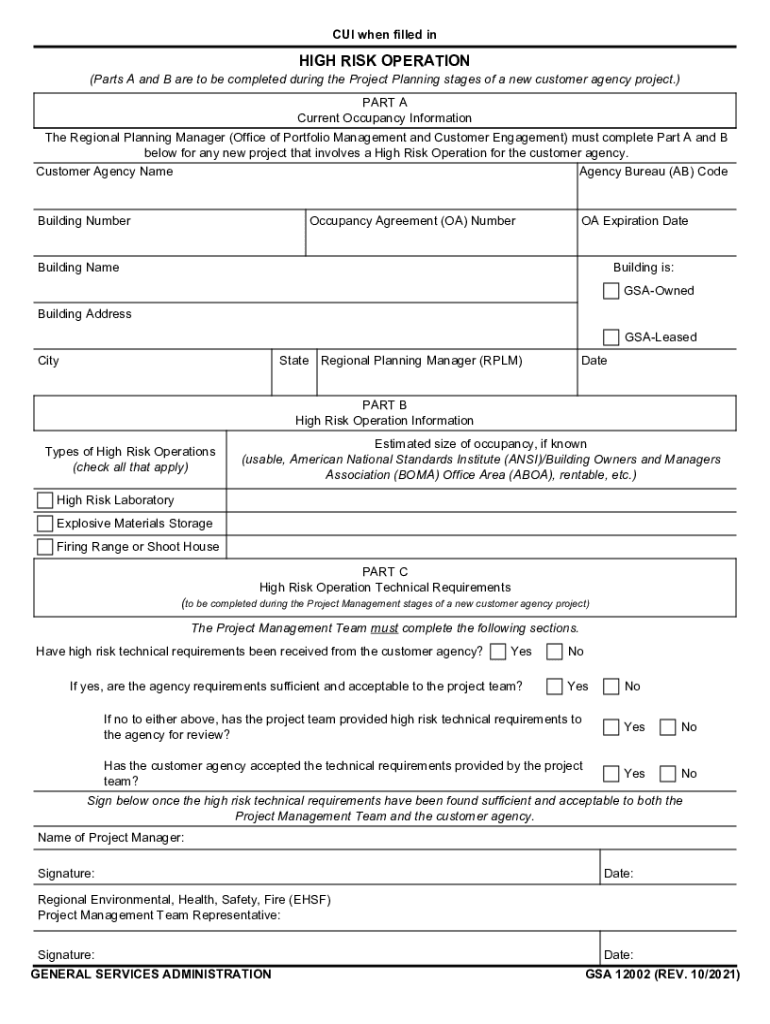
Www Cisa Govsitesdefaultthe Risk Management Process For Federal Facilities Form
Use a Www cisa govsitesdefaultThe Risk Management Process For Federal Facilities template to make your document workflow more streamlined.
What this federal facilities risk form does
The Www Cisa Govsitesdefaultthe Risk Management Process For Federal Facilities Form is identified here as a federal-facilities risk-management document, but its supplied name does not state an issuing agency, field definitions, filing deadline, or statutory retention period. In signNow, upload the source file, review auto-detected fillable fields, assign facility personnel as reviewers or signers, and send the completed workflow. The resulting record can include signer events, timestamps, document history, and a certificate of completion. Confirm program-specific requirements with the responsible federal authority before relying on the form.
Who benefits from this risk form
The supplied title points to federal facilities risk management, so the responsible agency must confirm the exact audience and approval chain.
Federal facility security teams can use the form to document risk assessments, route reviews, and preserve approval evidence when agency procedures identify this document as required. Contractors supporting federal facilities can prepare assigned sections, obtain designated signatures, and maintain the completed record without assuming authority to approve facility risk decisions. Centralized agency administrators can standardize templates, permissions, authentication, and audit-trail export after confirming the responsible program office’s field and retention requirements.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How this federal facilities form works
The workflow converts the supplied federal-facilities risk form into a controlled electronic review without assuming fields or authorities not stated in its name.
Upload: Upload the identified form Check fields: Review detected fillable fields Assign roles: Assign facility reviewers and signers Archive: Store the signed record and audit trail
Quick steps for this risk form
Use this sequence for the supplied federal facilities risk form, then verify agency-specific requirements before final approval.
Upload:
Upload the source PDF Review:
Review auto-detected fields Assign:
Add authorized reviewers Send:
Send for signatures Store:
Export the audit trail
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail documents evidence surrounding the federal facilities risk form rather than replacing the agency’s substantive review or records policy.
Authenticate:
Timestamp:
Hash:
Seal:
Certify:
Export:
Platform requirements for this risk form
Use signNow through Chrome, Firefox, Safari, or Edge on Windows or macOS; iOS and Android users can use the signNow mobile apps.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile apps iOS and Android signNow apps
Agency administrators should validate managed-device controls, identity-provider provisioning, and network policies before deployment. If the form contains facility-sensitive information, configure access, authentication, certificate handling, and audit-trail export according to the responsible agency’s security policy.
Recommended setup for this risk form
Configure the workflow around agency identity controls, signature evidence, encryption, and the records schedule assigned to this federal facilities document.
| Setting | Recommendation |
|---|---|
| Authentication method | Two-factor authentication for facility reviewers |
| Signature type | Electronic signature under ESIGN and UETA |
| Audit trail | Retain signer events and completion certificate |
| Document retention | Follow the agency records schedule |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
Security controls for this federal facilities form
Transport encryption:
Stored encryption:
SOC 2 Type II:
ISO 27001:
HIPAA safeguards:
ESIGN and UETA:
Best practices for completing this risk form
Accurate document identification and controlled approvals matter because the supplied form name does not state its agency, fields, deadline, or retention schedule.
Confirm the issuing authority and fields
Map signers to approval roles
Preserve the complete record
Match authentication to agency policy
Challenges when processing this risk form
Uploading an unidentified source file can produce incorrect fields, missing approval roles, or a workflow that does not match the responsible federal program. Sending facility-sensitive information to unauthorized recipients can expose operational details and weaken the access controls required by agency policy. Capturing a signature without documented electronic consent, signer attribution, or an accessible copy can complicate later evidentiary review under ESIGN and UETA. Applying a generic retention period can conflict with the agency records schedule because this form’s governing authority is not stated in its supplied name.
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting this federal facilities risk form
These answers address signNow workflow questions while separating platform operation from requirements that only the responsible federal authority can establish.
signNow’s Business plan includes templates, audit trails, mobile apps, and legally binding eSignatures at $8 per user per month when billed annually. Confirm the form’s agency rules separately because platform availability does not establish that this specific federal document may be electronically filed.
Upload the source file, then inspect every field signNow detects before sending. The supplied form name does not identify required fields or signers, so compare the generated document with the agency-issued source and correct omissions manually.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are demonstrated. They do not override an agency rule requiring a specific submission method, signature type, or controlled government system.
Use two-factor authentication, SMS OTP, or identity verification when agency policy requires stronger signer attribution. Advanced signer authentication is associated with higher-tier configurations, so confirm the selected plan and tenant settings before sending.
SignNow encrypts data in transit with TLS 1.2 or 1.3 and data at rest with AES-256. For facility-sensitive content, encryption does not replace agency access controls, approved hosting requirements, or records-management procedures.
Export the signed form, certificate of completion, and audit trail together, then apply the responsible agency’s records schedule. No retention period can be assigned from the supplied form name alone without risking an unsupported records-management claim.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.