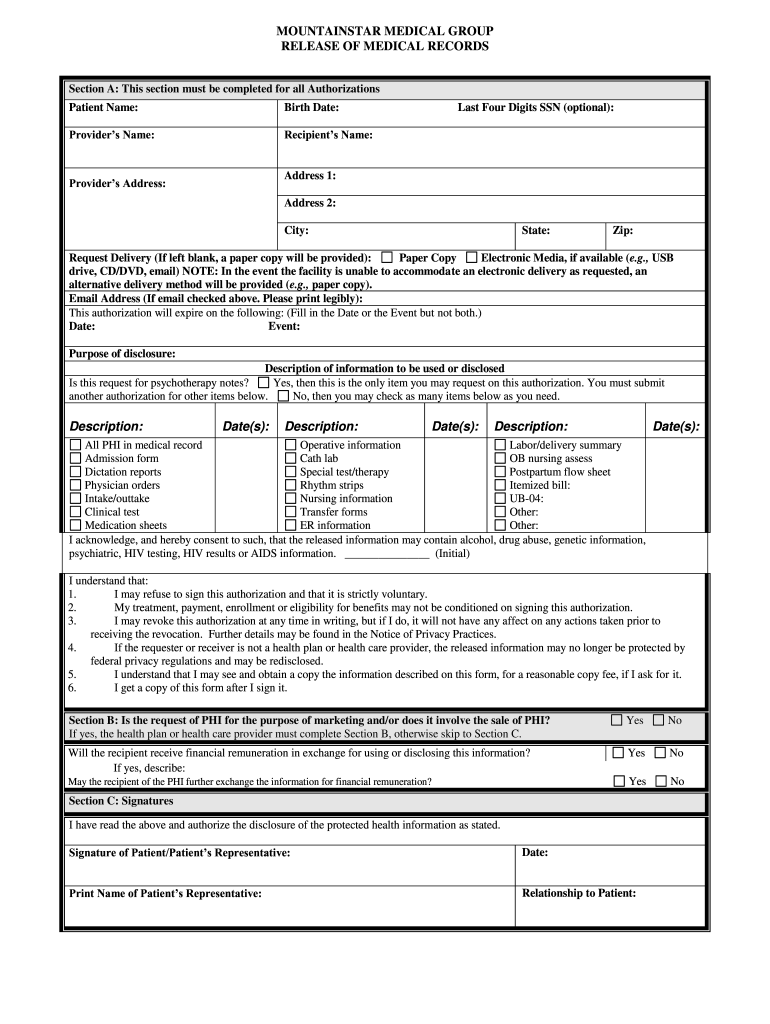
Authorization For Release Of Phi Individual Form
Create a custom Authorization For Release Of Phi Individual 0 that meets your industry’s specifications.
What this PHI authorization does
An Authorization For Release Of Phi Individual Form gives a person written permission for a specified recipient to obtain or disclose protected health information. The signer identifies the individual, names the records or information covered, identifies the recipient, states the purpose, and provides an expiration or revocation condition when required by the form. In a U.S. healthcare workflow, the authorization should be reviewed for HIPAA requirements, signed by the individual or valid personal representative, and retained with evidence of consent. signNow can route the form for electronic signature and preserve its audit trail.
Which healthcare businesses benefit most
The form is most useful where staff must document a patient’s permission before sharing defined PHI with an identified recipient.
A solo behavioral-health practice can use the form to obtain a patient’s authorization before releasing records to a lawyer, insurer, school, or another treating provider, while keeping a consistent template for every request. A regional clinic can route patient authorizations to staff, verify recipient and purpose fields, and retain signed copies alongside release requests without repeatedly rebuilding the document. An enterprise health system can standardize Authorization For Release Of Phi Individual Form templates across departments, assign delegated senders, and apply HIPAA-aware access controls to sensitive authorization records.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Manage access for authorization teams
Practice administrators can maintain a shared Authorization For Release Of Phi Individual Form template, control who edits PHI-related fields, and delegate sending to trained staff. signNow user roles and permissions help separate template ownership from day-to-day delivery while preserving centralized oversight. Healthcare operations teams can assign delegated senders for patient authorizations, keep approved templates available to departments, and limit administrative changes. signNow supports reusable templates and role-based access so staff can send the correct Authorization For Release Of Phi Individual Form without altering required language.
Complete the authorization in signNow
Use this workflow to prepare the Authorization For Release Of Phi Individual Form, collect the required consent, and preserve the signed record.
Upload form:
Upload the completed Authorization For Release Of Phi Individual Form PDF. Check fields:
Let signNow detect fillable fields, then verify names, dates, and authorization details. Add signers:
Assign the individual and any required organization representative as signers. Complete signing:
Send the form, collect signatures, and download the completed record.
How the authorization workflow works
The electronic process follows the form’s substantive consent requirements instead of replacing them: identify the information, recipient, purpose, and signer before routing.
Prepare document: Upload the form and confirm its PHI release fields. Assign signers: Add the patient and recipient-side signer in the required order. Capture authorization: Collect consent and record the signing event. Archive record: Store the signed form with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Privacy and disclosure pitfalls
Listing a recipient or purpose too broadly can make the authorization difficult for a healthcare organization to accept for the requested disclosure. Sending a completed form to the wrong email address can expose PHI and create an avoidable access-control incident. Missing the signer’s date, expiration language, or defined information scope can delay a records request until the form is corrected. Giving every staff member template-editing rights can allow unauthorized changes to the release language or required consent fields.
Recommended authorization workflow setup
Configure the Authorization For Release Of Phi Individual Form around signer identity, consent evidence, secure handling, and the organization’s applicable retention rule.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enabled with certificate of completion |
| Document retention | 6 years for HIPAA records (45 CFR 164.530(j)) |
| Encryption | TLS in transit and AES-256 at rest |
Protect authorization records and PHI
Encryption controls:
HIPAA safeguards:
Independent assurance:
Security certification:
Privacy controls:
Electronic signing:
What the audit trail records
For this PHI authorization, the audit trail helps connect the signer, consent event, completed document, and later record retrieval.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Export evidence:
Archive securely:
Features for PHI release authorizations
signNow combines form preparation, signer routing, consent evidence, and record handling for Authorization For Release Of Phi Individual Form workflows.
Field detection
Upload the Authorization For Release Of Phi Individual Form and let signNow detect fillable fields, reducing manual placement before staff reviews each patient, recipient, purpose, and expiration field.
Signer routing
Assign signing roles so the individual receives the authorization request and designated staff can manage routing without changing the approved form language.
Audit trail
Capture the signer’s consent event with timestamps, action history, and a certificate of completion that can accompany the signed authorization record.
Reusable templates
Use reusable templates for recurring PHI-release requests while keeping the authorization’s recipient, purpose, and scope specific to each individual request.
HIPAA controls
Support HIPAA workflows when a business associate agreement is required, with access controls and encrypted data handling for authorization records containing PHI.
Mobile signing
Use browser or mobile signing so patients and authorized representatives can review and sign without requiring an in-person document exchange.



Use mobile devices for signing
The signNow mobile apps for iOS and Android support reviewing and signing the Authorization For Release Of Phi Individual Form away from a desktop. Browser access can support staff preparation and patient completion, subject to the organization’s device and privacy controls.
Mobile apps iOS and Android apps Offline mode Offline signing available Document capture Camera document capture
Healthcare organizations should use managed devices, screen-lock policies, and approved storage locations when handling PHI. Offline signing and camera capture may be useful operationally, but staff should confirm synchronization, identity, and authorization completeness before treating the record as ready for disclosure.
Best practices for retaining PHI authorizations
A reliable recordkeeping process preserves the authorization’s exact scope, signer evidence, audit trail, and applicable retention period.
Review every release detail before sending
Export the audit trail with the signed form
Apply the six-year HIPAA retention rule
Separate template control from delegated sending
Legal standing of the authorization
An electronic Authorization For Release Of Phi Individual Form can support a U.S. consent record when the signer demonstrates intent, consents to electronic records, can access and retain the document, and the record remains reproducible under ESIGN and applicable state law. HIPAA requirements still govern PHI disclosures, and ESIGN excludes wills, court orders, and certain family-law documents.

Authorization workflows in practice
Healthcare and legal teams use this form when a documented patient decision must accompany a PHI release request.
Fertility care
Fertility Centers of Illinois can use a defined authorization workflow when patients request release of records to another provider, attorney, or insurer.
- Patient identifies recipient and purpose
- Staff routes signature request securely
The signNow customer story identifies Fertility Centers of Illinois and highlights its positive experience with the signNow API. Applied to this form, an API-connected workflow can help staff generate, route, and track patient authorizations while keeping the release request tied to the appropriate record-management process.
Legal records
A legal-services team requesting medical records can send the authorization to a client, then preserve the completed form with the related matter.
- Client reviews the specific release scope
- Signed copy supports the request file
The workflow should identify exactly what information may be disclosed, to whom, and for what purpose. Using a signNow template and audit trail gives the legal team a consistent electronic record of the client’s signing event, but the recipient organization should still confirm that the authorization satisfies its own release procedures.
Troubleshoot authorization workflows
Resolve field, consent, access, and retention questions before disclosing PHI through an electronic authorization workflow.
If the detected fields do not match the form, review every patient, recipient, purpose, scope, expiration, date, and signature field before sending. signNow’s field editor lets the sender correct placement and assign each field to the appropriate signer.
A Business plan includes templates and audit trails for routine authorization workflows. Business Premium adds bulk send and quick invite links, while Enterprise adds advanced signer authentication. Select the plan according to volume and identity-verification requirements.
HIPAA compliance requires a business associate agreement when signNow handles PHI for a covered entity or business associate. Confirm the BAA and configure organizational access controls before placing patient information into an electronic workflow.
Under ESIGN, consumer-facing electronic records require disclosure of the right to receive paper records, electronic-access capability, and withdrawal procedures. Healthcare organizations should provide the required disclosure before collecting electronic consent.
If a signer cannot access the request, verify the email address, resend the invitation, or use a controlled signing link. For sensitive PHI, avoid forwarding an unrestricted link and confirm the recipient’s identity first.
A completed authorization should include the signed document and its audit trail. Export both from signNow, then store them under the organization’s HIPAA record policy; 45 CFR 164.530(j) requires six-year documentation retention.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.