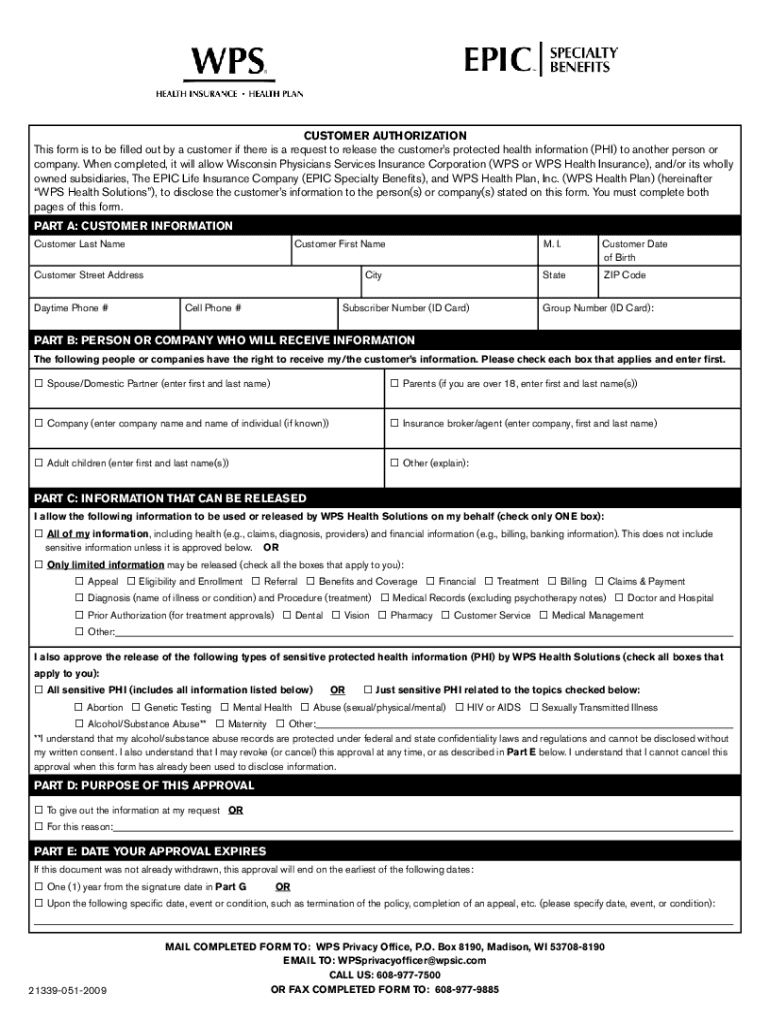
This Form Is To Be Filled Out By A Customer If There Is A Request To Release The Customers Protected Health Information Phi To A
Use a This Form Is To Be Filled Out By A Customer If There Is A Request To Release The Customers Protected Health Information PHI To A template to make your document workflow more streamlined.
What this PHI release authorization does
This form records a customer’s authorization to release specified protected health information to a named recipient. It should identify the information covered, the person or organization receiving it, the purpose of disclosure, and an expiration date or event. The customer reviews the authorization, provides informed consent, and signs it. A healthcare provider or other covered entity can then use the signed record to document the requested disclosure. HIPAA governs authorization content and handling; 45 CFR §164.530(j) requires covered entities to retain related policies, procedures, and records for six years.
How the PHI release workflow works
The workflow moves from document preparation to consent capture and controlled record storage without changing the authorization’s stated disclosure scope.
Upload form: Upload the PHI release PDF to signNow. Check fields: Review detected fields for patient and recipient roles. Send request: Send the authorization to the designated signer. Archive record: Store the signed release with its audit trail.
How the signNow audit trail records consent
The audit trail documents the technical history behind this PHI release authorization without replacing the authorization’s substantive HIPAA requirements.
Authenticate signer:
Capture timestamps:
Protect document:
Seal history:
Retrieve records:
Export evidence:
Recommended PHI release workflow setup
Configure this authorization around documented patient consent, restricted access, auditability, and HIPAA record-retention obligations.
| Setting | Recommendation |
|---|---|
| Authentication method | Two-factor authentication with SMS OTP |
| Signature type | Electronic signature with documented consent |
| Audit trail | Export the completed audit trail |
| Document retention | Retain six years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for PHI release records
HIPAA compliance:
Transport encryption:
Stored encryption:
Security certification:
Information security:
Signature framework:
Browser and system requirements
Complete this PHI release authorization using a current browser with an encrypted connection and a supported desktop or mobile operating system.
Windows browsers Chrome and Edge on Windows 10 or Windows 11 Mac browsers Safari and Chrome on macOS 12 or later Mobile browsers Safari on iOS 16 or later; Chrome on Android 12 or later
Use a managed device when the authorization contains protected health information. Healthcare organizations should confirm their signNow Business Associate Agreement, access controls, retention policy, and staff permissions before sending or storing completed releases.



Privacy and disclosure challenges
Leaving the recipient or disclosure purpose blank can make the authorization incomplete and prevent staff from confirming the permitted release scope. Attaching unrelated clinical information to the signed form increases exposure beyond the patient’s documented authorization and minimum-necessary workflow. Sending a PHI authorization without verifying signer identity can weaken attribution and create uncertainty about who gave consent. Saving the signed authorization without its audit trail makes later review of consent, timestamps, and document history more difficult.
Best practices for PHI release forms
Accurate authorization terms, controlled access, signer verification, and complete record preservation reduce disclosure ambiguity for healthcare staff and patients.
Define every disclosure term
Review detected fields carefully
Match authentication to sensitivity
Archive the complete record
PHI release record retention schedule
Use the HIPAA six-year rule as the federal baseline for covered-entity records, then compare the schedule with applicable state privacy requirements.
Six years: HIPAA records
Six years: release authorizations
Six years: disclosure policies
Six years: procedures
Longer period: state law
Legal value of a signed PHI authorization
A signed PHI release authorization documents patient intent, recipient, purpose, scope, and expiration for a requested disclosure. Electronic execution may satisfy ESIGN and applicable UETA rules when consent, attribution, and record retention requirements are met, but HIPAA authorization content and state privacy law still govern the release.

PHI release troubleshooting questions
Use these answers to resolve field, authentication, compliance, audit-trail, and plan questions before releasing protected health information.
Upload the authorization as a PDF, then review signNow’s detected fields before adding the patient, recipient, and provider roles. If a field is missing, place it manually and confirm required status before sending. The Business plan includes templates and audit trails for repeat releases.
A HIPAA workflow requires a Business Associate Agreement with signNow and appropriate administrative controls. signNow states that HIPAA compliance requires a BAA. Confirm the BAA, role permissions, authentication settings, and minimum-necessary disclosure before transmitting protected health information.
A signer can use an email invitation or a configured SMS OTP step. Verify the signer’s mobile number, resend the invitation, and check spam filtering. Business Premium adds quick invite links, while Enterprise adds advanced signer authentication capabilities.
The authorization should identify the information released, recipient, purpose, expiration or event, and patient signature. If any required term is absent, correct the template before sending. HIPAA’s authorization requirements remain the governing legal standard, not the software configuration.
After signing, signNow records the signing event and provides an audit trail associated with the completed document. Export both files, restrict access, and place them in the organization’s approved HIPAA archive. HIPAA requires records to remain available for six years.
The Business plan is listed at $8 per user per month with annual billing and includes 100 signature invites per user per year. Business Premium is $15 and includes bulk send. Confirm current plan limits and the required HIPAA add-on terms before deployment.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.