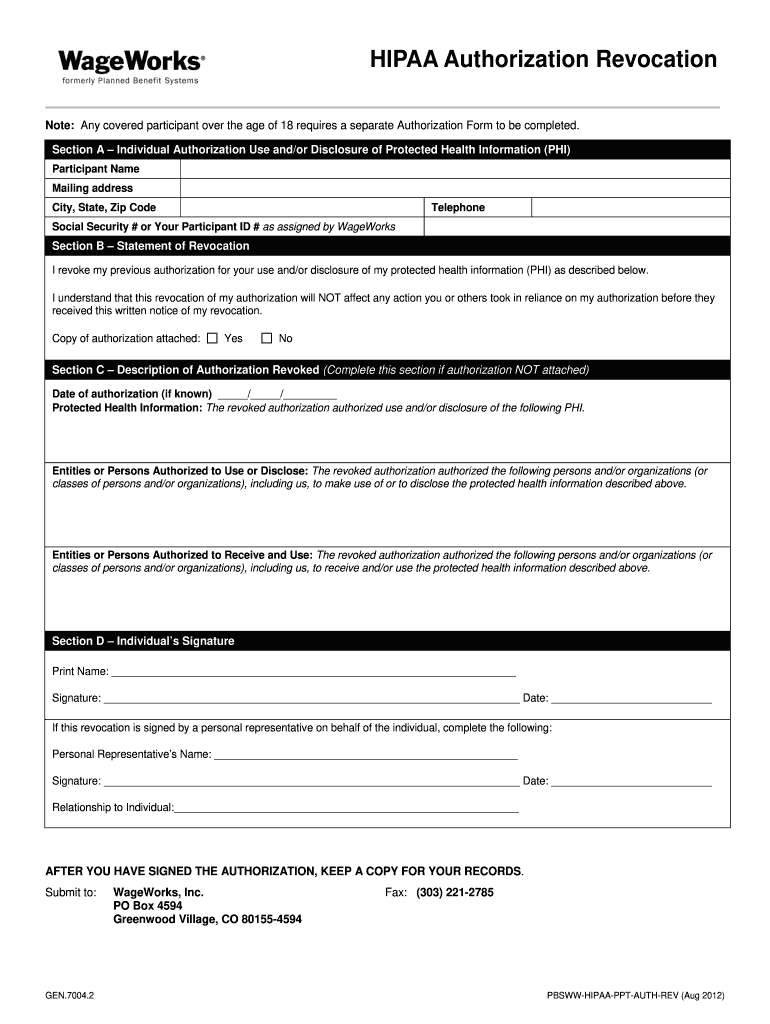
HIPAA Disclosure Revocation Form
Use a Hipaa Disclosure Revocation Form template to make your document workflow more streamlined.
What the revocation form does
A HIPAA Disclosure Revocation Form withdraws a person’s permission for a covered entity or business associate to disclose protected health information under an earlier authorization. The individual identifies the authorization, recipient, information scope, and effective revocation, then signs and dates the form. HIPAA does not require a single federal template, so organizations should follow their authorization language and applicable policy. Revocation generally applies going forward and does not undo disclosures already made in reliance on the authorization. Keep the signed form and evidence of delivery with the relevant privacy records.
Who uses this revocation form
Patients
Patients use the form to withdraw a prior permission allowing a provider, health plan, or business associate to disclose specified protected health information.
Privacy teams
Privacy offices use the signed record to document the requested change, notify affected personnel, and maintain evidence of delivery and processing.
Organizations that use the form
The form is most useful where a patient’s disclosure decision must be recorded, routed, and preserved across a defined HIPAA privacy workflow.
Solo healthcare practitioners can document a patient’s withdrawal of a prior disclosure permission and send the signed record to their privacy contact without paper handling. Behavioral health and specialty clinics can route revocations to designated privacy staff, preserving authorization details, signer evidence, and delivery records in one controlled workflow. Enterprise health systems can use templates, access controls, and audit trails to process patient revocations consistently across departments while requiring a HIPAA business associate agreement.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How to complete the revocation form
Complete the HIPAA Disclosure Revocation Form by identifying the authorization, signing the revocation, and preserving the completed record.
Upload form:
Upload the completed HIPAA Disclosure Revocation Form to signNow. Check fields:
Review detected fields and add missing signer, date, or initials fields. Add signer:
Enter the authorized recipient’s email address and send the form. Complete form:
Review, sign, and download the completed revocation record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the signNow audit trail records
The audit trail separates signer evidence from the form’s substantive content and preserves the events needed to review a completed HIPAA revocation.
Authenticate signer:
Capture timestamp:
Protect document:
Seal history:
Track actions:
Export trail:
Recommended workflow setup
Use a controlled signing workflow that ties the patient’s revocation, authorization details, delivery evidence, and retention record together.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS authentication |
| Signature type | Electronic signature with intent |
| Audit trail | Export with the completed PDF |
| Document retention | Six years under 45 CFR §164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 at rest |
Security controls for PHI workflows
HIPAA protection:
Transit encryption:
Stored encryption:
Security certification:
Management standard:
Access controls:
Privacy and disclosure pitfalls
Including diagnoses, treatment details, or unrelated medical information exposes more protected health information than the revocation requires. Failing to identify the authorization or recipient precisely can leave the covered entity unable to determine which disclosure permission is withdrawn. Using an outdated signer email or weak authentication can make attribution of the revocation difficult during an audit or dispute. Sending the signed record through an uncontrolled channel can expose protected health information after the revocation is completed.
Legal value of a signed revocation
A signed revocation creates evidence of the individual’s intent, the authorization affected, and the date notice was provided. ESIGN and UETA generally support electronic records and signatures when intent, consent, attribution, and record retention are established. Wills, court orders, and family-law decrees remain outside those statutes’ general scope.

Retention and record-keeping practices
Preserve the revocation, authorization context, delivery evidence, and audit history together so the privacy decision remains understandable later.
Apply the six-year HIPAA documentation period
Export the audit trail with the form
Match the revocation to its authorization
Archive records with controlled access
Platform requirements for signing
Use the HIPAA Disclosure Revocation Form in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile apps for iOS and Android, supporting review and signing away from a desk.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktops Mobile access iOS and Android mobile apps
Organizations handling protected health information should use managed devices, current operating-system security updates, and controlled user access. Confirm that the selected signNow plan and business associate agreement meet the organization’s HIPAA workflow requirements before sending the form.



Key performance indicators that demonstrate SignNow's proven track record.
HIPAA revocation form troubleshooting
Resolve field, signer, retention, and compliance questions before treating a HIPAA Disclosure Revocation Form as complete.
Upload the HIPAA Disclosure Revocation Form as a PDF, then use signNow’s field detection and editor to check every authorization, recipient, signature, and date field before sending. If detection misses a field, place it manually and confirm the signer role.
The Business plan includes legally binding eSignatures, audit trails, templates, mobile apps, ISO 27001, SOC 2, and GDPR features. A HIPAA workflow requires a business associate agreement, so confirm the applicable plan and BAA before processing PHI.
If a patient cannot access the email link, resend the invitation or create a controlled signing link. For stronger attribution, use SMS authentication where configured, then retain the completed form and audit trail together.
A revocation does not erase disclosures already made in reliance on the authorization. Record the effective date, notify the covered entity or business associate, and preserve delivery evidence so future disclosure handling can be reviewed.
HIPAA documentation must generally be retained six years from creation or the last effective date under 45 CFR §164.530(j). Export the signNow audit trail and retain it with the final revocation, subject to longer state or organizational rules.
The signNow Business Premium plan includes bulk send and kiosk mode, while Enterprise adds advanced signer authentication. Use only the features appropriate to the patient workflow, and verify identity, consent, access, and retention controls before deployment.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.