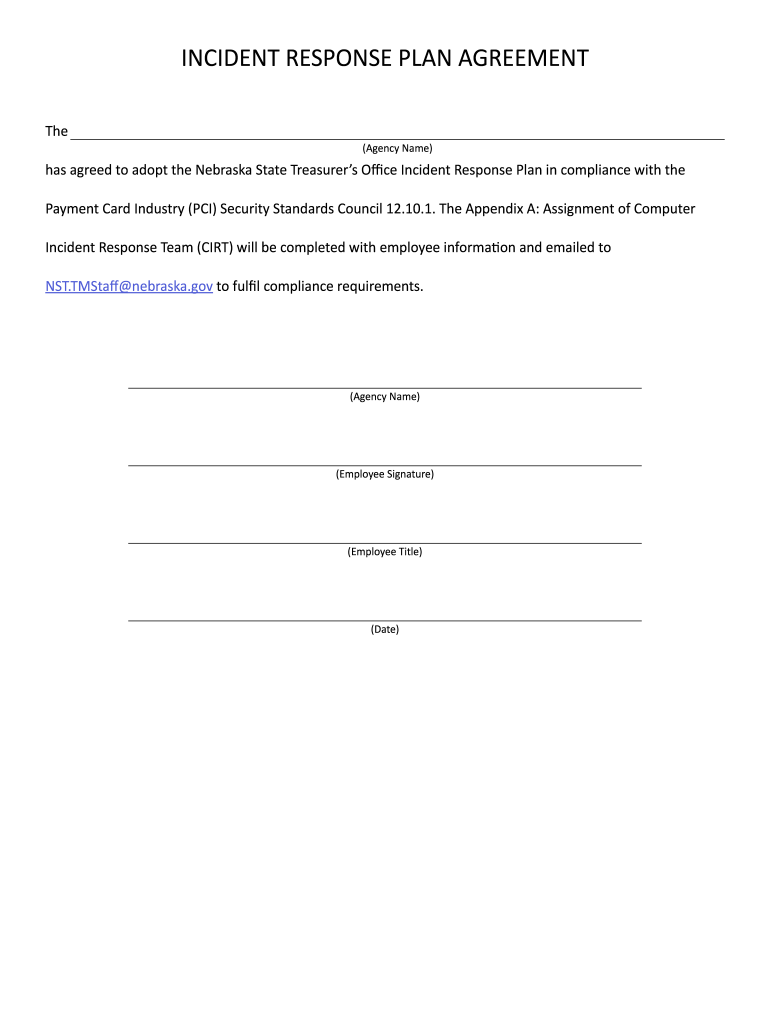
Incident Response Plan Agreement Form
Use a INCIDENT RESPONSE PLAN AGREEMENT template to make your document workflow more streamlined.
What this incident response agreement does
The Incident Response Plan Agreement Form records who accepts incident-response responsibilities and how the parties acknowledge the agreed process. In plain terms, it turns response roles, escalation contacts, approval expectations, and related acknowledgments into a document that can be completed and signed. With signNow, upload the form, review automatically detected fillable fields, assign signers, send it for completion, and retain the signed copy with its audit trail. ESIGN and UETA generally recognize qualifying electronic signatures, but exclusions and state requirements still require separate review.
Who uses this incident agreement
Security teams
Security teams use this agreement to document incident-response responsibilities, escalation contacts, acknowledgment requirements, and handling expectations before an event occurs.
Service providers
Managed service providers and business administrators use it to coordinate response obligations with vendors, employees, contractors, and affected departments.
Business types that use this agreement
The Incident Response Plan Agreement Form is most useful wherever response responsibilities must be acknowledged, assigned, and preserved as an auditable record.
Solo security consultants can use the Incident Response Plan Agreement Form to record client contacts, response duties, and approval evidence without maintaining paper packets. Managed service providers can send standardized incident agreements to customer contacts, assign role-based signers, and retain completed records for contract administration. Enterprise security departments can standardize acknowledgments across business units, preserve audit trails, and connect signed agreements with existing operational systems.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How the agreement workflow works
The workflow moves from document preparation to controlled signing and then preserves the completed Incident Response Plan Agreement Form with its transaction history.
Upload: Upload the Incident Response Plan Agreement Form to signNow. Prepare: Review detected fields and add missing signer, date, or acknowledgment fields. Send: Assign participants and send the agreement through email or a signing link. Store: Collect signatures and preserve the completed file with its audit trail.
How the agreement audit trail works
The signNow audit trail records identity, timing, document integrity, and retrieval events around the completed Incident Response Plan Agreement Form.
Authentication:
Authentication record:
Timestamp capture:
Document hashing:
Sealing:
Audit export:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Ways to send and sign the agreement
- Use the signNow web app when administrators need to upload the Incident Response Plan Agreement Form, review detected fields, assign signers, and monitor completion centrally.
- Use the signNow mobile app when incident coordinators or managers must review and sign the agreement from an approved iOS or Android device.
- Use kiosk mode for supervised, shared-device signing when staff members complete the Incident Response Plan Agreement Form at a controlled office or response location.
- Use a shareable signing link when authorized participants need access without a separate email invitation, while preserving the agreement’s signer and audit-trail records.
Key features for incident agreements
signNow provides a structured way to prepare, route, sign, and preserve the Incident Response Plan Agreement Form without separating the signed document from its transaction evidence.
Field detection
Upload the Incident Response Plan Agreement Form and review automatically detected fields before sending it for completion.
Signer routing
Assign incident-response participants to specific signature, acknowledgment, or date fields before delivery.
Audit trail
Capture signing actions, timestamps, and document history in an accessible audit trail.
Flexible signing
Use email delivery, mobile signing, kiosk mode, or shareable links for controlled completion.
Signer verification
Apply authentication controls such as SMS OTP or identity verification when agreement sensitivity requires stronger attribution.
Record preservation
Store the signed agreement with its completion evidence for later operational or legal review.
Privacy and disclosure pitfalls
Personal details in incident agreements may be exposed when completed documents are emailed broadly or stored without role-based access controls. A signed agreement may lack documented consent for electronic records, weakening evidence that participants accepted digital delivery and signing. Incorrect permissions can let unauthorized employees view response contacts, escalation details, or confidential incident information in completed agreements. Reusable templates may retain prior incident data, causing personal or confidential information to appear in a new agreement.
Signer authentication and document security
PKI support:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Audit evidence:
Mobile options for signing
Use the signNow mobile app on iOS 16 or later and Android 11 or later. Signers can review the Incident Response Plan Agreement Form, capture supporting pages with a device camera, and continue approved offline signing workflows when connectivity is unavailable.
iPhone iOS 16 and later Android Android 11 and later Mobile tools Camera capture and offline signing
Organizations should manage mobile access through approved devices and identity policies. For regulated deployments, confirm required authentication, SSO provisioning, API controls, and certificate or long-term-validation settings before distributing incident agreements through mobile workflows.



Best practices for completing the agreement
Accurate fields, controlled signer access, documented consent, and preserved audit evidence make the Incident Response Plan Agreement Form easier to administer and review.
Define response duties before sending
Review fields and signer routing
Preserve the audit trail securely
Check consent and legal scope
Risks of incomplete agreements
Electronic consent
Attribution gap
Permission failure
Version dispute
Response ambiguity
Troubleshooting the incident agreement workflow
Use these answers to resolve field, signer, consent, plan, and legal-scope questions before relying on a completed Incident Response Plan Agreement Form.
Upload the source document again as a supported file and inspect signNow’s detected fields before adding or correcting fields manually. The Business plan includes templates and audit trails, which can preserve the corrected Incident Response Plan Agreement Form workflow after preparation.
Confirm that every required participant has a valid email address or signing link, then verify routing and field assignments. signNow supports sequential or assigned signing workflows; an unassigned field can prevent completion even when the document itself is valid.
For consumer-facing records, provide the ESIGN disclosure, explain the right to receive paper records, confirm electronic access, and explain withdrawal procedures under 15 U.S.C. §7001(c). signNow can capture the resulting signature workflow, but the business remains responsible for lawful disclosure.
Use signNow authentication controls appropriate to the agreement’s sensitivity, such as SMS OTP or stronger identity verification. Two-factor authentication and identity evidence support attribution, but they do not replace organizational access policies or required incident-response approvals.
The Business plan is listed at $8 per user per month with annual billing and includes 100 signature invites per user per year. Business Premium adds bulk send, while Enterprise adds advanced signer authentication and integrations.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention requirements are met. They do not override exclusions such as wills, certain court filings, and family-law decrees, which require separate legal handling.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.