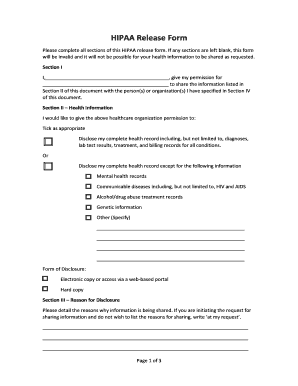
HIPAA Release Form Information
Use a Hipaa Release Form Information Pdf template to make your document workflow more streamlined.
What HIPAA Release Form Information does
HIPAA Release Form Information authorizes a covered entity or business associate to disclose specified protected health information to a named person or organization. The form should identify the information covered, the disclosing party, the recipient, the purpose, and an expiration date or event. A patient signs to show authorization, and signNow can route the document, capture the electronic signature, and preserve an audit trail. HIPAA documentation generally must be retained six years from creation or the last effective date under 45 CFR §164.530(j).
Business types using HIPAA releases
Healthcare teams use the form when a patient authorizes disclosure of specified protected health information to a defined recipient and purpose.
Solo practitioners can use an approved HIPAA release template to collect patient authorizations, identify disclosure recipients, and preserve signed evidence without exchanging paper forms during each request. Multi-location clinics can centralize templates, assign administrative permissions, and delegate sending while maintaining separate access to patient-specific release records and audit trails. Enterprise healthcare organizations can connect signNow with systems such as Salesforce, Microsoft 365, NetSuite, or cloud storage while enforcing authentication, retention, and security policies across departments.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Complete a HIPAA release in signNow
Use the approved authorization template, verify every disclosure detail, then route and archive the signed record through signNow.
Upload document:
Upload the approved HIPAA release template. Check fields:
Review auto-detected fields and add authorization fields. Add signers:
Enter the patient and authorized recipient. Send request:
Send the release for electronic signature. Archive record:
Store the completed release with its audit trail.
How the HIPAA release audit trail works
signNow records identity, timing, document integrity, and retrieval details as each HIPAA release moves through completion.
Authenticate signer:
Capture timestamp:
Hash document:
Seal record:
Log activity:
Retrieve evidence:
Recommended HIPAA release configuration
Configure the release workflow around authorization details, signer identity, audit evidence, encryption, and HIPAA’s six-year retention rule.
| Setting | Recommendation |
|---|---|
| Authentication method | Email authentication with SMS OTP |
| Signature type | Legally binding electronic signature |
| Audit trail | Enable certificate of completion |
| Document retention | Retain six years from creation or last effective date |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for HIPAA release data
HIPAA protection:
Transport encryption:
Stored encryption:
Security certification:
Information security:
Transaction evidence:
Platform requirements for HIPAA releases
Complete HIPAA Release Form Information in signNow using a current desktop browser or the signNow mobile app on supported operating systems.
Supported browsers Chrome, Firefox, Safari, and Edge on Windows or macOS Mobile apps signNow mobile apps for iOS and Android Connection security TLS 1.2 or newer with JavaScript enabled
Healthcare organizations should use managed Windows, macOS, iOS, or Android devices and approved network controls when handling protected health information. Administrators should also confirm browser updates, TLS support, mobile-app permissions, and organizational access policies before sending release forms to patients or authorized recipients.
Key features for HIPAA releases
signNow combines structured authorization templates, signer controls, audit evidence, and retention workflows for patient-directed disclosure records.
Electronic signature
The approved HIPAA release can be completed electronically, with signer intent and completion details preserved for later review under ESIGN and applicable UETA principles.
Audit trail
SignNow records timestamps, actions, IP information, and document history so the completed authorization has supporting transaction evidence.
Reusable template
Templates help staff consistently request the patient, recipient, purpose, information scope, and expiration details required by the organization’s authorization process.
Signer authentication
SMS authentication and other configured signer controls can add identity evidence before a patient signs the release.
Mobile signing
Mobile apps allow authorized staff and patients to review and sign HIPAA release documents on supported devices.
Secure retention
Completed releases can be exported and archived with access restrictions, supporting the six-year HIPAA documentation period.



Best practices for signed HIPAA releases
Accurate authorization language, complete audit evidence, secure archival, and documented retention help keep each HIPAA release usable and reviewable.
Include every required authorization detail
Export the audit trail with each release
Apply the six-year federal retention rule
Archive releases with restricted access
Rollout and retention for HIPAA releases
A controlled rollout links template preparation, recipient verification, staff training, signed-record export, and the HIPAA documentation retention period.
Prepare template:
First send:
Team onboarding:
Seven-day trial:
Complete record:
Six-year rule:
Policy review:
Secure archive:
Privacy pitfalls in HIPAA releases
A patient’s diagnosis, treatment details, or identifiers may appear in a completed release and require restricted access throughout sending, signing, and archival. A recipient may be named without a sufficiently clear disclosure purpose, making the authorization difficult to apply to the intended request. Staff may grant broad template or download permissions, allowing users to view protected health information unrelated to their assigned disclosure. Electronic consent evidence may be separated from the authorization document, weakening the record needed to demonstrate who signed and when.
Risks of improper HIPAA releases
Disclosure challenge
Privacy exposure
Proof weakness
Documentation violation
HIPAA release troubleshooting questions
Use these answers to resolve authorization, access, plan, audit-trail, and retention questions before distributing protected health information.
Business includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2 Type II, and GDPR support. HIPAA use requires the appropriate Business Associate Agreement, organizational safeguards, and a workflow configured for protected health information. Confirm contractual requirements before sending patient releases.
A signed release does not automatically satisfy HIPAA authorization requirements. The document should identify the information disclosed, the person or class authorized to disclose it, the recipient, purpose, and expiration or event. Have privacy counsel review the template and use signNow for controlled completion and evidence.
Business Premium adds bulk send, kiosk mode, request payments, and quick invite links. For one patient-specific HIPAA release, Business may provide the needed audit trail and templates, while plan selection should reflect authentication, user administration, BAA, retention, and integration requirements.
If a patient cannot open the document, verify the email address, resend the invitation, and check browser or mobile-app access. signNow supports mobile apps, while administrators should avoid sending protected health information through an unapproved channel or to an unverified recipient.
The signNow audit trail records signing events, timestamps, IP information, and document history. Export the completed release with its certificate of completion, then store both under the organization’s HIPAA records policy. The platform record supports evidence but does not replace required privacy procedures.
HIPAA requires covered-entity policies and procedures to retain required documentation for six years from creation or the last effective date under 45 CFR §164.530(j). Configure retention and archival controls to meet that rule and any longer state or healthcare-record requirement.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.