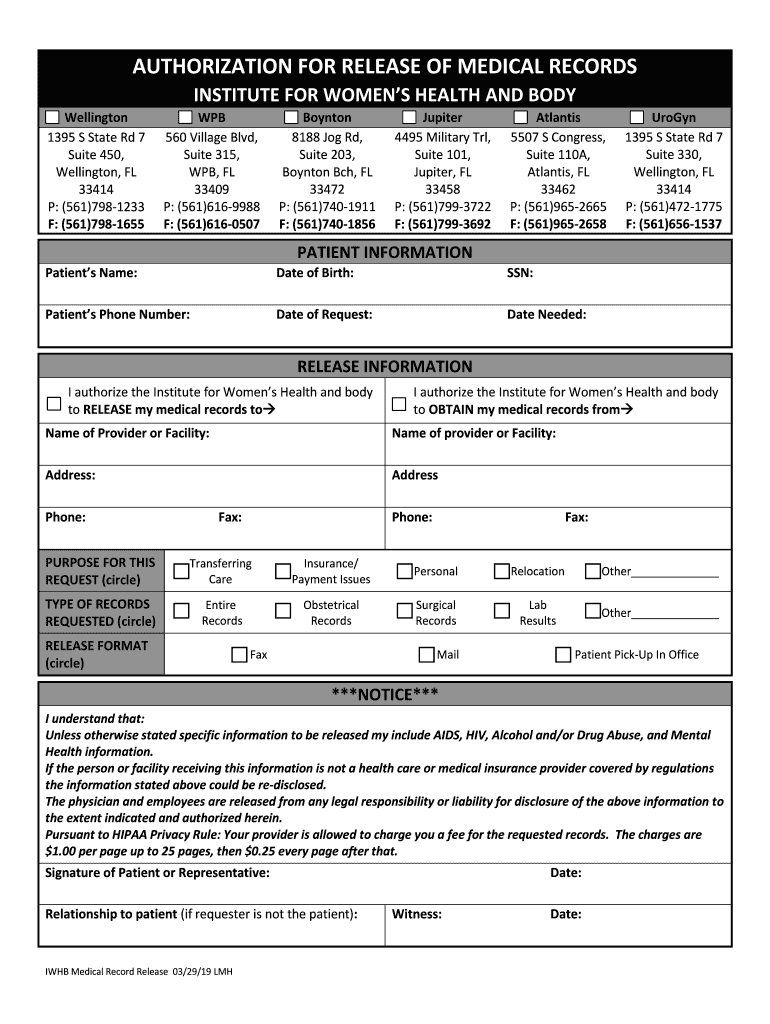
Authorization Release Medical Records Form
Use a Authorization Release Medical Records Form template to make your document workflow more streamlined.
What this medical records form does
An Authorization Release Medical Records Form gives a healthcare provider written permission to disclose specified medical records to a named person or organization. The form usually identifies the patient, records covered, recipient, purpose, expiration, and patient or representative signature. With signNow, upload the form, review detected fillable fields, assign each signer, send it for electronic signature, and retain the completed document with its audit trail. HIPAA documentation is generally retained for six years from creation or the last effective date under 45 CFR §164.530(j).
Who uses this medical records authorization
Healthcare providers
Healthcare providers use the form to identify the patient, permitted records, recipient, purpose, and expiration before disclosing protected health information. SignNow can route the authorization to the patient or representative, preserve consent evidence, and support HIPAA workflows when the organization has the required BAA.
Patients and representatives
Patients and authorized representatives review the requested disclosure, confirm the named recipient and purpose, and sign the authorization. Clear role assignments reduce uncertainty about who approved release and help the provider retain a complete record of the transaction.
Key features for medical record authorization
The form captures permission to disclose specified medical records while signNow organizes fields, signatures, consent evidence, and secure document history.
Field detection
Upload the Authorization Release Medical Records Form and let signNow identify fillable areas, reducing manual placement work before the patient or authorized representative reviews the document.
Role-based fields
Assign patient, provider, and representative fields clearly so every required authorization detail is completed by the correct signer before release.
Flexible signing
Send the medical-records authorization by email or signing link, allowing recipients to review and sign without creating a signNow account.
Audit trail
Capture consent, timestamps, signer activity, and document history in one audit trail that helps demonstrate how authorization was completed.
Protected records
Keep sensitive authorization records protected with encryption in transit and at rest, supporting HIPAA workflows when a BAA is required.
Reusable template
Reuse a prepared authorization template for recurring record requests while preserving the specific patient, provider, recipient, and disclosure details for each transaction.
How the authorization form works
The signNow workflow moves the medical-record authorization from preparation through consent and secure recordkeeping.
Upload: Upload form Detect: Detect fields Assign: Assign signers Store: Store evidence
Choose the right signing method
- Use the signNow web app when staff need to upload the authorization, place patient and recipient fields, review the completed PDF, and manage the audit trail centrally.
- Use the signNow mobile app when a patient or representative must review and sign the medical-record authorization from an iOS or Android device.
- Use kiosk mode for supervised intake when several patients complete authorizations at a clinic desk using one managed workstation; Business Premium includes kiosk mode.
- Generate a signing link when a provider needs to distribute the same authorization entry point through a patient portal, message, or controlled communication channel.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization workflow setup
Configure the Authorization Release Medical Records Form around patient identity, disclosure scope, consent evidence, and protected record retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture IP, timestamps, and action history |
| Document retention | Keep six years under HIPAA 45 CFR 164.530(j) |
| Encryption method | TLS 1.2/1.3 and AES-256 encryption |
Security for medical record authorizations
HIPAA protection:
Transit encryption:
At-rest encryption:
Security certification:
ISO certification:
Activity records:
Platform requirements for signing
The Authorization Release Medical Records Form can be prepared in Chrome, Firefox, Safari, or Edge on Windows 10/11 and macOS. signNow mobile apps support iOS and Android for recipients reviewing and signing from a phone or tablet.
Web browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows 10/11 and macOS Mobile apps iOS and Android signNow apps
Healthcare organizations should use managed Windows, macOS, iOS, or Android devices when handling protected health information. Enterprise deployments can connect API workflows, SSO provisioning, and controlled storage; confirm certificate, long-term validation, and access policies with the organization’s compliance team before production use.
Teams that manage authorization workflows
Clinic administrators can create a controlled Authorization Release Medical Records Form template, assign patient and provider roles, and delegate sending without allowing every staff member to change disclosure language. Shared templates keep recurring fields consistent while preserving transaction-specific patient and recipient information for each request. Health information management teams can manage completed authorizations through role-based access, audit trails, and delegated sending. They can review who sent, signed, or accessed each form and retain the evidence with the authorization, supporting internal privacy procedures for protected health information.
What the audit trail records
The audit trail separates consent evidence from the form’s medical content, documenting who acted, when they acted, and how the completed authorization was handled.
Authenticate signer:
Capture timestamps:
Record document history:
Seal activity:
Track session details:
Export evidence:
Best practices for this authorization
Accurate scope, verified recipients, documented consent, and controlled retention reduce disclosure errors when preparing this medical-record authorization.
Specify every disclosure detail
Confirm identity and electronic consent
Preserve the authorization record
Restrict access and protect storage
Medical authorization record retention
Retention depends on the record’s legal category; HIPAA documentation uses a six-year period, while unrelated records follow their own governing rules.
Six years: HIPAA records
Three years: tax records
Six years: tax exception
Three years: payroll records
Five years: injury records
Privacy pitfalls to check before sending
Listing a broad record category can disclose more protected health information than the patient intended, creating an avoidable privacy and authorization-scope issue. A missing expiration date or purpose can make the provider’s authorization review difficult and delay disclosure until the request is clarified. Sending the signed form to an unintended recipient can expose protected health information, especially when email addresses or signing links are entered incorrectly. Allowing unauthorized staff to access templates or completed forms can weaken internal controls over patient identifiers and medical-record disclosures.
Troubleshooting medical record authorizations
Resolve field, signer, privacy, compliance, and retention questions before releasing any protected medical information.
Upload the Authorization Release Medical Records Form as a PDF, then use signNow’s editor to place or adjust patient, representative, provider, date, and signature fields. Confirm every disclosure-specific field before sending because automatic detection does not determine the legally correct scope of records.
A signNow Business plan includes templates, audit trails, mobile apps, and legally binding eSignatures at $8 per user per month when billed annually. Business Premium adds bulk send and kiosk mode at $15 per user per month annually; plan limits and overage terms should be reviewed before rollout.
HIPAA compliance is available with a business associate agreement, or BAA, where required. Configure access controls, limit recipients, and confirm the organization’s privacy procedures separately; signNow’s HIPAA status does not replace the healthcare provider’s obligations under HIPAA.
Under ESIGN and UETA, an electronic signature can support enforceability when intent, consent, attribution, and record retention are established. For consumer-facing electronic records, 15 U.S.C. §7001(c) also addresses disclosure, access, and withdrawal of consent requirements.
If the wrong recipient receives a signing link, cancel or correct the transaction before disclosure, document the incident internally, and send a new authorization to the verified address. The completed audit trail records signing activity but cannot cure an authorization sent to an unintended recipient.
Export the completed authorization and audit trail from signNow, then store them in the organization’s controlled records system. HIPAA documentation must generally be retained for six years from creation or the last effective date under 45 CFR §164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.