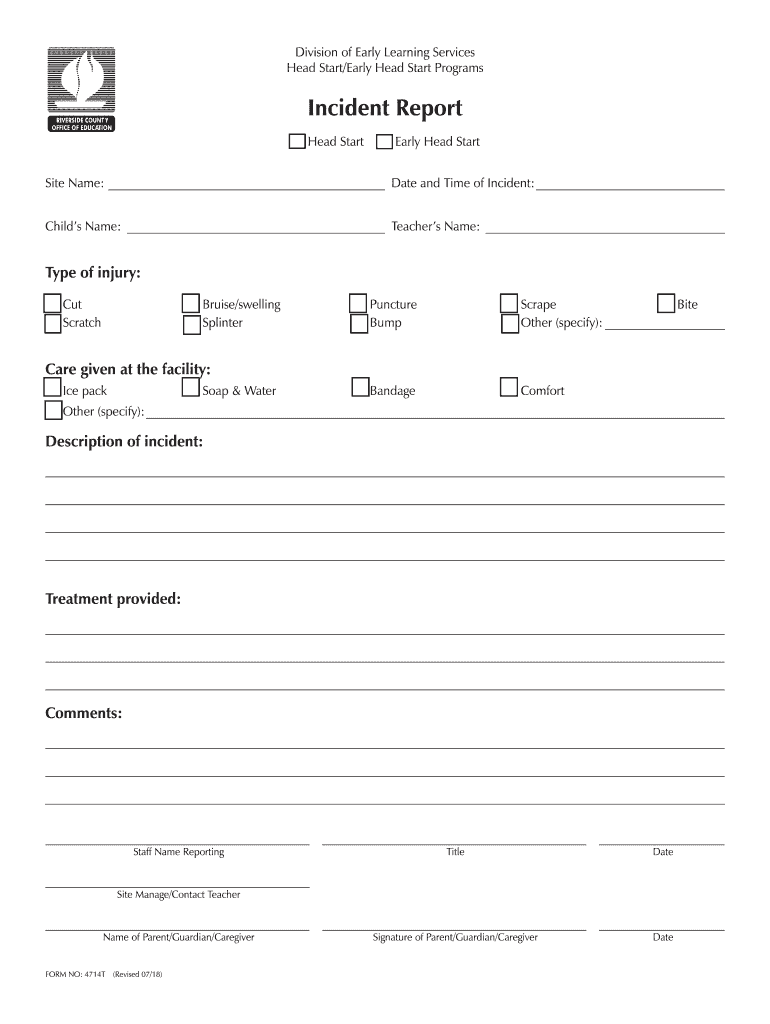
Hs Els Incident Report Form
Use a HS ELS Incident Report template to make your document workflow more streamlined.
What the Hs Els Incident Report Form does
Hs Els Incident Report Form is a structured record for documenting an incident, the people involved, relevant facts, and follow-up actions. Complete the report by entering the event details, reviewing the narrative for accuracy, and obtaining the required acknowledgment or signature. With signNow, upload the form, let the platform detect fillable areas, add or correct fields, send it to the assigned signer, and retain the completed PDF with its audit trail. ESIGN and applicable state electronic-transaction law can support an electronic signature when intent, consent, attribution, and record reproduction are established.
Who uses this incident report form
Workplace safety
Safety coordinators can collect an incident description, date, location, witness details, and corrective-action acknowledgment from employees or contractors. Role-based access helps limit sensitive reports to investigators, supervisors, and authorized administrators while preserving a completed audit trail.
Regulated operations
Healthcare and public-service teams can route reports involving protected or sensitive information through controlled signing workflows. A HIPAA-covered organization must evaluate whether the report contains PHI and use a BAA-supported signNow configuration when required.
How to complete the incident report
Use this sequence to prepare Hs Els Incident Report Form, capture the required acknowledgment, and preserve evidence of completion.
Upload form:
Upload the Hs Els Incident Report Form PDF to signNow. Check fields:
Review detected fields and add missing incident fields. Add signer:
Assign the report to the responsible signer or reviewer. Send report:
Send the report through signNow’s signing workflow. Store evidence:
Review and store the completed PDF with its audit trail.



 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Security for incident reports
Data in transit:
Data at rest:
Independent assurance:
Security certification:
Health information:
Electronic signatures:
How the incident report audit trail works
signNow records the signing evidence separately from the incident narrative, helping reviewers verify who acted, when, and whether the completed file changed.
Authenticate signer:
Capture timestamp:
Record document hash:
Seal document:
Create certificate:
Export audit trail:
Privacy controls for incident reports
Incident narratives may expose names, medical details, or contact information when access permissions are broader than the investigation requires. A signer may complete the report without a recorded consent disclosure when the document is used in a consumer-facing electronic workflow. Shared links can expose signed incident reports if recipients forward them or access controls do not restrict intended participants. Exported reports may retain sensitive attachments in unsecured folders, creating disclosure risk after the investigation closes.
Risks from incomplete incident reporting
Missing factual detail
Unclear signer identity
Uncontrolled document access
Late internal escalation
Retention rules for related records
Hs Els Incident Report Form does not establish one universal retention period. Apply the rule governing the records and industry connected to each incident, then document the policy used.
Six years for HIPAA records
Three years for tax records
Six years for major understatement
Three years for payroll records
Five years for OSHA records
Best practices for incident reports
Accurate fields, controlled access, preserved audit evidence, and a documented retention rule make Hs Els Incident Report Form more useful during review or investigation.
Complete factual fields before signing
Restrict access to authorized reviewers
Preserve the audit trail with the report
Apply the governing retention rule
Platform requirements for incident reports
Hs Els Incident Report Form can be prepared in a browser using TLS 1.2 or 1.3 and accessed through Chrome, Firefox, Safari, or Edge. signNow mobile apps support iOS and Android for reviewing and signing assigned reports.
Browser support Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS desktops Mobile access iOS and Android apps
Organizations should use managed Windows, macOS, iOS, or Android devices when reports contain sensitive information. Administrators can also evaluate API access, SSO provisioning, and certificate or long-term-validation requirements before connecting incident reporting with internal systems.
Incident report troubleshooting questions
These answers address field detection, signer identity, electronic-signature validity, privacy controls, plan scope, and retention for Hs Els Incident Report Form workflows.
Upload the original Hs Els Incident Report Form as a PDF or supported document, then inspect signNow’s detected fields. Add missing date, narrative, acknowledgment, or signature fields manually before sending the report to a signer.
The signNow Business plan is listed at $8 per user per month with annual billing. It includes templates, audit trails, and mobile apps. Confirm current plan terms before relying on bulk send, kiosk mode, or advanced authentication features.
A signed report can support attribution and integrity evidence when the signer intends to sign, consents to electronic records, and the record remains reproducible. ESIGN and UETA provide the legal framework; they do not replace incident-specific policy requirements.
If an incident report contains protected health information, the organization must assess HIPAA obligations and require a business associate agreement where applicable. signNow identifies HIPAA compliance as requiring a BAA; configure access and retention separately.
Use signNow authentication appropriate to the report’s sensitivity, such as an email-controlled workflow or stronger verification where policy requires it. Check the audit trail for signer identity, timestamps, and recorded actions before closing the investigation.
Export the completed report and audit trail through the organization’s approved records process. Retention depends on the underlying record category; HIPAA records generally require six years under 45 CFR §164.530(j), while OSHA injury records require five years under 29 CFR §1904.33.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.