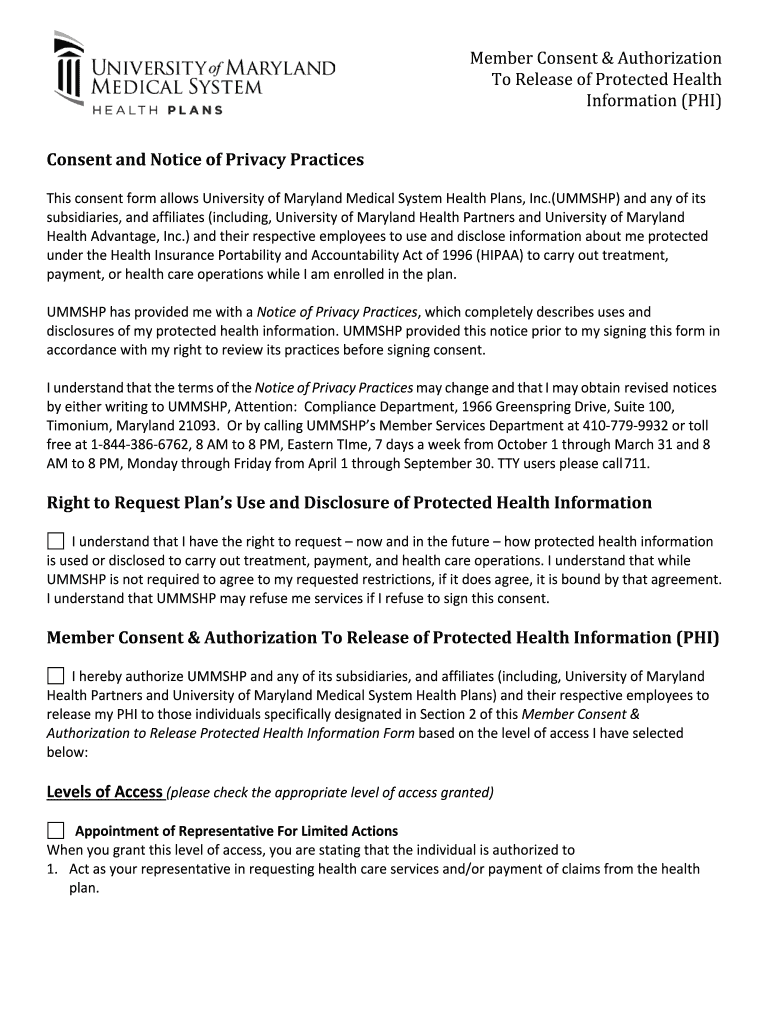
Consent And Notice Of Privacy Practices Form
Use a Consent And Notice Of Privacy Practices template to make your document workflow more streamlined.
What this privacy practices form does
The Consent And Notice Of Privacy Practices Form records that a patient or authorized person received and acknowledged an organization’s privacy notice. It commonly identifies the patient, describes permitted uses and disclosures of protected health information, documents consent or acknowledgment, and captures a signature and date. With signNow, an organization uploads its approved form, reviews detected fillable fields, sends it to the signer, and stores the completed document with an audit trail. HIPAA requirements and organizational policies still determine the notice content and retention period.
Who uses this privacy form
Healthcare providers
Healthcare providers use the form to document delivery of their current Notice of Privacy Practices and capture a patient’s acknowledgment before or during care. The completed record can be linked to the patient file, while signNow’s audit trail preserves signing activity for authorized compliance review.
Medical practices
Medical practices, fertility centers, and specialty clinics use structured templates to collect consistent acknowledgments from patients or personal representatives. When protected health information is involved, the organization must configure access, retention, and its HIPAA obligations separately from the electronic-signature workflow.
Legal standing of privacy acknowledgments
A signed Consent And Notice Of Privacy Practices Form can provide evidence that a person received and acknowledged a privacy notice when intent, consent, attribution, and reliable record retention are documented under ESIGN and applicable state law. Electronic rules do not replace HIPAA duties, and they exclude wills, codicils, certain court orders, and family law decrees.

Features for privacy acknowledgments
signNow combines field preparation, signer routing, audit evidence, and protected storage workflows for Consent And Notice Of Privacy Practices Form records.
Field detection
Upload the organization’s Consent And Notice Of Privacy Practices Form and review signNow’s detected fields before sending, reducing manual placement work while preserving the approved notice language.
Remote signing
Route the form directly to the patient or authorized representative by email, so the recipient can review the privacy notice and sign without an in-person paper exchange.
Audit trail
Capture signature, date, signer activity, and completion details in a connected audit trail that supports later review of the specific privacy acknowledgment.
Reusable templates
Use reusable templates for the approved notice and acknowledgment fields, helping healthcare teams present consistent documents across patient intake workflows.
Data protection
Protect privacy-form data with TLS 1.2/1.3 in transit and AES-256 at rest, subject to the organization’s configuration and HIPAA obligations.
Secure archival
Export completed records and completion evidence for controlled storage with the applicable patient record, retention schedule, and access permissions.
Complete the privacy form online
Use this sequence to prepare, send, sign, and retain a Consent And Notice Of Privacy Practices Form with signNow.
Upload form:
Upload the organization’s current privacy notice and consent form. Review fields:
Confirm detected fields and add required signer information. Send securely:
Send the notice to the patient or authorized recipient. Archive copy:
Collect the signature and download the completed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended privacy-form workflow
Configure the Consent And Notice Of Privacy Practices Form around signer identity, evidence preservation, protected data, and the applicable HIPAA retention rule.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture timestamps, signer activity, and completion evidence |
| Document retention | Six years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 protection |
Platform requirements for privacy forms
Complete the Consent And Notice Of Privacy Practices Form in Chrome, Firefox, Safari, or Edge on Windows 10, Windows 11, or macOS. signNow uses TLS 1.2/1.3 for data in transit, and its iOS and Android apps support mobile review and signing.
Browser support Chrome, Firefox, Safari, Edge Desktop systems Windows 10, Windows 11, macOS Mobile access iOS and Android signNow apps
Organizations should manage access on approved Windows, macOS, iOS, or Android devices, especially when privacy forms contain protected health information. Confirm browser updates, identity controls, SSO provisioning, API access, and retention settings with the organization’s security and compliance administrators before deployment.
Security controls for privacy forms
Protect privacy data:
Support HIPAA workflows:
Document control assurance:
Use ISO 27001:
Encrypt transmitted records:
Support electronic signatures:
Best practices for privacy records
Accurate templates, documented retention, exported audit evidence, and controlled access help organizations manage signed privacy acknowledgments responsibly.
Use the approved notice version
Apply the six-year HIPAA period
Export the audit trail
Archive with controlled access
Privacy and disclosure pitfalls
Uploading an outdated Notice of Privacy Practices can produce a signed record that does not reflect the organization’s current disclosures or effective date. Sending unnecessary protected health information in email notifications can expose more patient data than the signer needs to review. Allowing broad workspace access can expose completed privacy acknowledgments to staff who lack a treatment, payment, operations, or administrative need. Treating a signature alone as HIPAA compliance can overlook notice content, BAA requirements, state privacy rules, and the organization’s retention policy.
Risks of incomplete privacy forms
Evidence gap
Consent dispute
Privacy breach
Attribution failure
Privacy form retention schedule
Retain signed privacy acknowledgments according to HIPAA and any longer state or organizational requirements that apply to the patient record.
Six years for HIPAA records
Six years from creation
Six years from last effective date
Six-year compliance record
Longer period if required



Troubleshooting privacy form workflows
Resolve field, signer-access, retention, plan, and electronic-consent questions before relying on a completed privacy acknowledgment.
Upload the current approved notice again and confirm that the PDF opens correctly before sending. signNow’s field detection can identify fillable areas, but the organization must verify every patient, representative, signature, and date field against its HIPAA workflow.
A signed form does not by itself establish HIPAA compliance. Use a signNow HIPAA workflow with a required BAA, restrict access to authorized users, and confirm that notice content and disclosures satisfy the covered entity’s obligations.
Business includes legally binding eSignatures, templates, and audit trails at $8/user/month with annual billing. It does not include every advanced control; confirm the plan’s authentication and integration requirements before deployment.
If the signer cannot open the request, verify the email address, resend the invitation, or provide an approved signing link. The signer can use a supported browser or signNow mobile app without changing the privacy notice itself.
HIPAA requires retaining privacy documentation for six years from creation or the last effective date under 45 CFR 164.530(j). Store the completed form and audit evidence with controlled access, then check state law for longer periods.
For consumer-facing electronic records, ESIGN 15 U.S.C. §7001(c) requires disclosure of the right to paper, electronic-access capability, and withdrawal procedures. Add those disclosures where applicable before requesting an electronic acknowledgment.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.