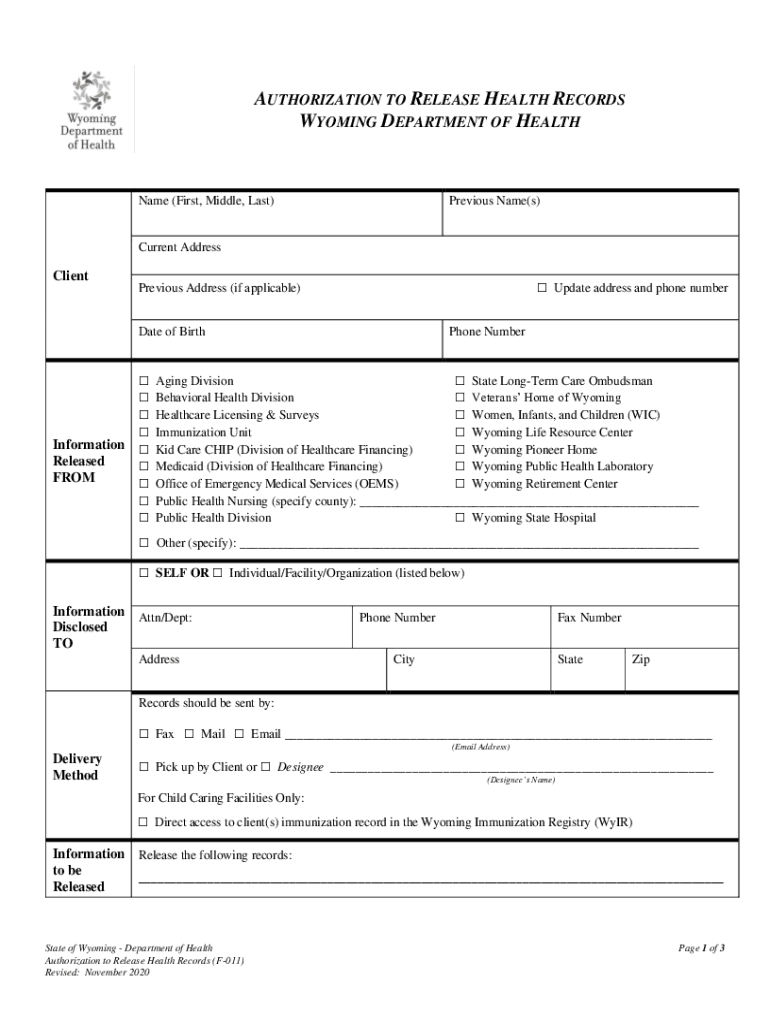
Authorization To Release Health Records Form
Use a AUTHORIZATION TO RELEASE HEALTH RECORDS template to make your document workflow more streamlined.
What this health-record authorization does
An Authorization To Release Health Records Form gives a named person or organization permission to obtain specified health information for a stated purpose. The signer identifies the patient, recipient, records, scope, expiration, and consent, then signs the authorization. Healthcare organizations should apply HIPAA’s 6-year documentation retention period when applicable under 45 CFR 164.530(j). signNow can upload the form, detect fillable fields, send it for signature, capture an audit trail, and store the completed record. State privacy law or a provider’s policy may impose additional requirements.
Who handles health-record authorizations
The form serves patients, authorized representatives, clinical organizations, and release-of-information teams that must document a specific health-information disclosure.
A private medical practice uses the form to document a patient’s permission before sending specified records to another provider, attorney, insurer, or named family representative, while preserving the recipient, purpose, expiration, and signature in one file. A hospital release-of-information team uses structured templates to collect patient or representative signatures, route requests to authorized staff, and retain the completed authorization with an audit trail for later disclosure review. A healthcare network uses role-based signNow access and shared templates so centralized administrators control the release language while clinic staff send the same approved authorization to patients across locations.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Features that fit health-record releases
A structured signNow workflow keeps the requested records, recipient, purpose, consent, and evidence connected throughout the Authorization To Release Health Records Form process.
Defined scope
Place the patient’s name, authorized recipient, purpose, record categories, expiration date, and signature fields in one controlled electronic workflow. This reduces omissions that could make the requested disclosure scope difficult to interpret.
Flexible signing
Send the authorization to the patient or authorized representative by email, mobile workflow, kiosk mode, or controlled signing link. signNow records the signing event rather than relying on an email footer or informal consent.
Audit evidence
Capture timestamps, signer actions, authentication events, and the completed document in an audit trail. The resulting evidence helps staff demonstrate how the authorization was executed and preserved.
Controlled access
Use role-based access and delegated sending so intake staff can send the approved authorization without changing its legal or clinical language. Administrators can manage templates and permissions centrally.
Secure retention
Keep the signed authorization and audit trail in an encrypted repository. signNow identifies HIPAA compliance as requiring a business associate agreement for workflows involving protected health information.
System connections
Route completed authorizations to connected systems such as Google Drive, Box, Egnyte, Salesforce, or Microsoft 365. This reduces duplicate downloads while keeping the record available to authorized teams.
How this authorization workflow works
The signNow process connects the authorization’s fields, signer request, completed signature, and audit evidence in a defined sequence.
Upload document: Upload the health-record authorization PDF. Detect fields: Auto-detect fields and verify required entries. Request signature: Send the request to the named signer. Store evidence: Store the signed form with its audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Complete the authorization in signNow
Use this sequence to prepare, sign, and retain an Authorization To Release Health Records Form without losing its scope or signature evidence.
Upload form:
Upload the completed authorization PDF to signNow. Check fields:
Review detected fields and add missing signature, date, and initials fields. Send request:
Enter the authorized recipient’s email and send the request. Review authorization:
Confirm the signer reviews scope, purpose, and expiration before signing. Store records:
Download the signed form and audit trail for secure records storage.
Recommended authorization workflow setup
Configure the Authorization To Release Health Records Form around signer identity, protected health information, audit evidence, and controlled access.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Export certificate of completion |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption and user provisioning | AES-256 storage with role-based admin access |
Review the authorization audit trail
The signNow audit trail separates signer authentication, event capture, document integrity, and evidence retrieval from the form’s clinical or administrative content.
Authenticate signer:
Timestamp actions:
Log activity:
Hash document:
Seal record:
Retrieve evidence:
Choose how the authorization gets signed
- Use the signNow web app when staff need to upload the Authorization To Release Health Records Form, map fields, and send it from a desktop workflow.
- Use the signNow mobile app when clinicians or patients need to review and sign the authorization on an iOS or Android device.
- Use kiosk mode for an in-person intake desk where a patient completes the health-record authorization on a managed shared device.
- Generate a shareable signing link when a clinic needs to place the same authorization request in a patient portal or controlled message.
Protect the authorization record
Retention, audit-trail export, and controlled archival keep this health-record authorization usable and reviewable after signing.
Apply the HIPAA six-year retention rule
Export the audit trail after completion
Archive protected health information securely
Track scope and revocation status
Avoid privacy and disclosure mistakes
Listing a broad category such as “all records” can disclose more protected health information than the patient intended to authorize. Leaving the recipient, purpose, expiration date, or signature date blank can make the release scope unclear during later review. Sending the completed authorization through an unapproved shared mailbox can expose patient information to unintended recipients. Allowing unrestricted template access can let staff alter the authorized recipient or disclosure scope before signing.
Risks from incomplete authorization
Disclosure authorization challenged
HIPAA documentation deficiency
Unauthorized disclosure exposure
Audit evidence weakened



Troubleshoot health-record authorization workflows
These answers address field detection, signer identity, HIPAA controls, consumer consent, plan capabilities, and retention for this authorization workflow.
Upload the original Authorization To Release Health Records Form again and check whether the PDF is readable. signNow’s field-detection step may need manual correction when labels, checkboxes, or signature areas are flattened into an image. Confirm every required field before sending.
A completed signature does not by itself establish HIPAA compliance. signNow identifies HIPAA compliance as requiring a business associate agreement, and the healthcare organization must also apply its own access, disclosure, and retention procedures under 45 CFR 164.530(j).
Business includes legally binding eSignatures, audit trails, templates, mobile apps, ISO 27001, and SOC 2. Business Premium adds bulk send and kiosk mode. Select a plan based on the authorization volume, signing method, and required controls.
Use SMS OTP or another available signer-authentication control when email-only attribution is insufficient for the organization’s release policy. Enterprise adds advanced signer authentication, while the final control choice should reflect the sensitivity of the records and applicable policy.
A consumer-facing electronic record may require disclosure of the right to receive paper records, proof that the consumer can access the electronic format, and a withdrawal procedure under 15 U.S.C. §7001(c). Review the workflow with counsel before sending to consumers.
Export the completed PDF and audit trail after signing, then store them in the approved health-record repository. When HIPAA applies, retain required documentation for 6 years from creation or the last effective date under 45 CFR 164.530(j).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.