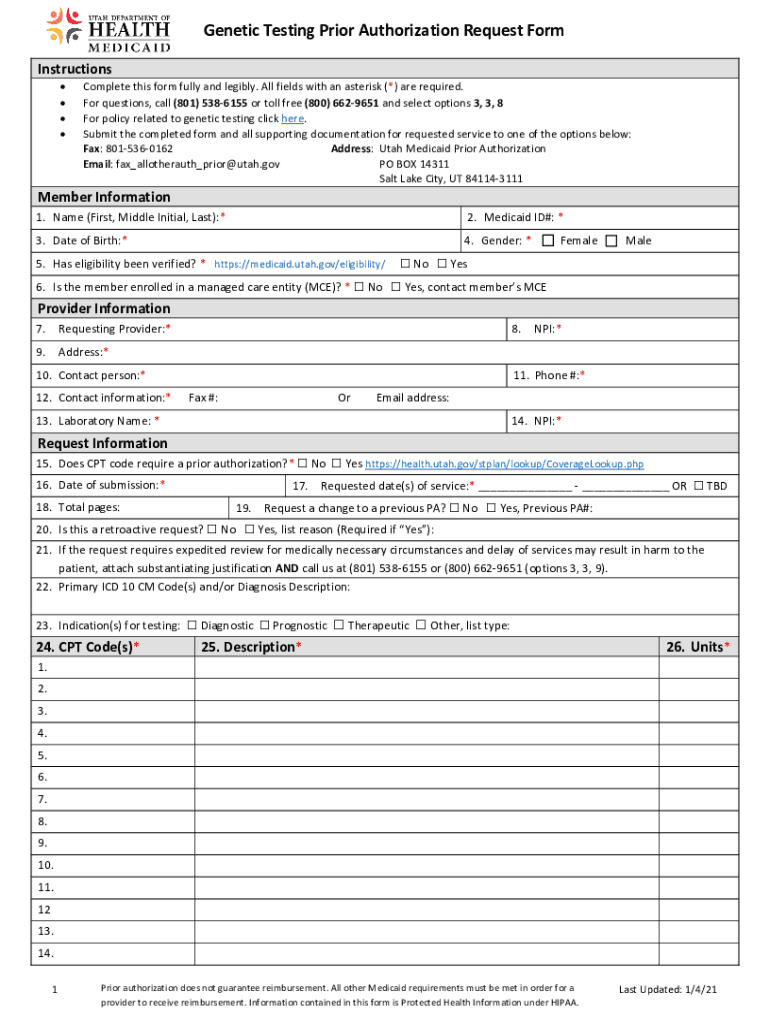
Genetic Testing Authorization Form Fax Completed Form To
Use a Genetic Testing Authorization Form Fax Completed Form To template to make your document workflow more streamlined.
What this authorization form does
The Genetic Testing Authorization Form Fax Completed Form To records a person’s permission for specified genetic testing or related disclosure and identifies where the completed form should be sent. It typically connects the individual, testing purpose, authorized recipient, signature, and date in one record. With signNow, a sender uploads the faxed or scanned document, reviews detected fillable fields, sends it to the signer, and stores the completed copy with an audit trail. Healthcare organizations must still use authorization language and safeguards required by HIPAA and applicable state law.
Who uses this genetic testing form
Healthcare providers
Healthcare providers use the form to document patient authorization before genetic testing or disclosure of related information.
Testing laboratories
Genetic testing laboratories use it to capture authorized recipient details and preserve completed consent records.
How the authorization form works
A clear workflow helps healthcare teams complete, sign, and retain this genetic testing authorization accurately.
Upload the form: Upload the fax-ready authorization form and identify its required fields. Check the details: Review patient details, authorization scope, recipient information, and signature fields. Request signature: Send the completed form to the authorized signer for electronic signature. Store the record: Download or retain the signed authorization with its audit trail.
Recommended authorization workflow settings
Use controlled signer verification, documented consent, and retention aligned with the records handled by the testing organization.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS verification for external signers |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Retain completion certificate and action history |
| Document retention | 6 years for HIPAA records (45 CFR 164.530(j)) |
| Encryption | TLS 1.2/1.3 and AES-256 at rest |
Features for genetic testing authorizations
signNow combines field preparation, signer delivery, audit evidence, and protected storage for teams handling genetic testing authorization forms.
Structured fields
Separate fields for patient details, authorization purpose, recipient information, signature, and date help reduce incomplete genetic testing authorizations before sending.
Field detection
Automatic field detection can accelerate preparation of a faxed or scanned authorization, while sender review confirms that each field aligns with the original document.
Flexible delivery
Email delivery or signing links let authorized individuals review the genetic testing authorization without exchanging repeated paper copies.
Audit trail
A completion certificate and action history preserve evidence of signing events, supporting review of who signed and when the authorization was completed.
HIPAA support
HIPAA compliance with a required BAA supports workflows involving protected health information when the organization configures its contractual and administrative safeguards.
Mobile access
Mobile apps allow staff and authorized signers to review the form when desktop access is unavailable, subject to the organization’s security controls.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Best practices for this authorization form
Accurate scope, signer verification, field review, and controlled retention reduce disclosure and consent errors in genetic testing workflows.
Define the testing authorization scope
Verify the authorized signer
Review each field placement
Preserve the completed record
Security for genetic testing records
Transport encryption:
Stored encryption:
HIPAA safeguards:
Control certification:
Security certification:
Signing evidence:
Retention schedule for signed records
Retain the completed genetic testing authorization according to the record category and the organization’s applicable privacy, healthcare, and records-management obligations.
6 years for HIPAA records
3 years for tax records
6 years for major understatement
3 years for payroll records
5 years for injury records
What the audit trail records
The audit trail documents the signing evidence behind this genetic testing authorization rather than merely tracking whether a form was sent.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log actions:
Retrieve evidence:
Platform requirements for this form
Complete the Genetic Testing Authorization Form Fax Completed Form To through supported browsers including Chrome, Firefox, Safari, and Edge on Windows or macOS. signNow protects connections using TLS 1.2/1.3, and its mobile applications support iOS and Android access.
Browsers Chrome, Firefox, Safari, and Edge Desktop systems Windows and macOS desktop access Mobile systems iOS and Android mobile applications
Healthcare organizations should use managed devices, approved identity controls, and restricted storage for this authorization. Enterprise deployments may also configure SSO provisioning, API access, and retention controls so completed forms and audit trails remain available only to authorized personnel handling genetic testing information.



Businesses that benefit from this workflow
The form is most useful where genetic testing requires documented consent, controlled disclosure, and a retrievable signed record.
Independent genetic counselors can send a patient-specific authorization, collect the signature, and retain the completed form without coordinating repeated fax exchanges. The workflow keeps the testing purpose and recipient information attached to the signed record for later review. Healthcare clinics can route genetic testing authorizations to patients or representatives, apply SMS verification, and preserve audit evidence. A HIPAA-compliant configuration with a BAA supports handling protected health information within the clinic’s broader privacy program. Testing laboratories and enterprise health systems can standardize templates, delegate sending, and connect completed forms to approved storage. Role-based access and documented audit trails help administrators review authorization status across multiple testing workflows.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Legal standing of the authorization
A signed genetic testing authorization can support evidence of consent when the signer’s intent, identity, electronic consent, and record integrity are documented. ESIGN and UETA generally recognize qualifying electronic signatures, but wills, certain court orders, and family law decrees remain excluded. HIPAA authorization requirements still apply where protected health information is disclosed.

Pricing and plan features
signNow pricing and verified plan details are shown first; unavailable competitor details are marked Not verified.
| Features | signNow | DocuSign | Adobe Sign | PandaDoc | Dropbox Sign |
|---|---|---|---|---|---|
| Annual Business price | $8/user/month billed annually | Not verified | Not verified | Not verified | Not verified |
| Free trial | 7 days, no card required | Not verified | Not verified | Not verified | Not verified |
| Bulk send | Business Premium includes it | Not verified | Not verified | Not verified | Not verified |
| HIPAA support | HIPAA compliant, BAA required | Not verified | Not verified | Not verified | Not verified |
Examples of authorization workflows
Healthcare and enterprise customer stories illustrate workflow patterns, while the authorization’s clinical and privacy requirements remain organization-specific.
Fertility healthcare
Fertility Centers of Illinois uses signNow for patient-facing workflows where clear authorization and responsive digital signing are important.
- Healthcare authorization workflow
The organization’s named customer story identifies the signNow API as effective and the team as responsive. For a genetic testing authorization, a comparable workflow would still require the clinic to define the testing purpose, recipient, privacy disclosures, and signer authority before sending. The platform handles the signing record, not the clinical determination.
Enterprise operations
Tech Data uses airSlate SignNow to improve internal and external customer service and increase speed to revenue.
- Enterprise document workflow
Tech Data’s customer story demonstrates an enterprise document workflow, but it does not identify genetic testing forms specifically. Healthcare teams should therefore use the example only as an operational reference and independently validate HIPAA safeguards, authorization language, access permissions, and retention requirements for this form.
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting genetic testing authorizations
Resolve field, signer, privacy, plan, and retention questions before treating the completed authorization as the final record.
Business includes legally binding eSignatures, templates, audit trails, mobile apps, ISO 27001, SOC 2 Type II, and GDPR support. For genetic testing information, HIPAA compliance requires a BAA and appropriate organizational safeguards beyond selecting a plan.
Use signNow’s field review after upload to correct detected placement. Faxed or scanned forms can produce imperfect field alignment, so confirm patient details, authorization scope, recipient fields, signature, and date before sending.
A signer can receive an email or signing link without creating an account in many workflows. If the clinic requires stronger identity evidence, configure SMS verification or another available authentication method before sending the authorization.
HIPAA compliance is available with a required BAA, but the organization remains responsible for access controls, minimum-necessary disclosure, consent language, and retention. Configure the workflow so the completed authorization and audit trail remain restricted.
Business Premium is listed at $15 per user per month when billed annually and includes bulk send. Business is $8 per user per month annually; competitor prices and comparable limits are Not verified here.
The signed authorization can be downloaded with its completion evidence and stored in an approved repository. HIPAA records generally require six years from creation or the last effective date under 45 CFR 164.530(j).
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.