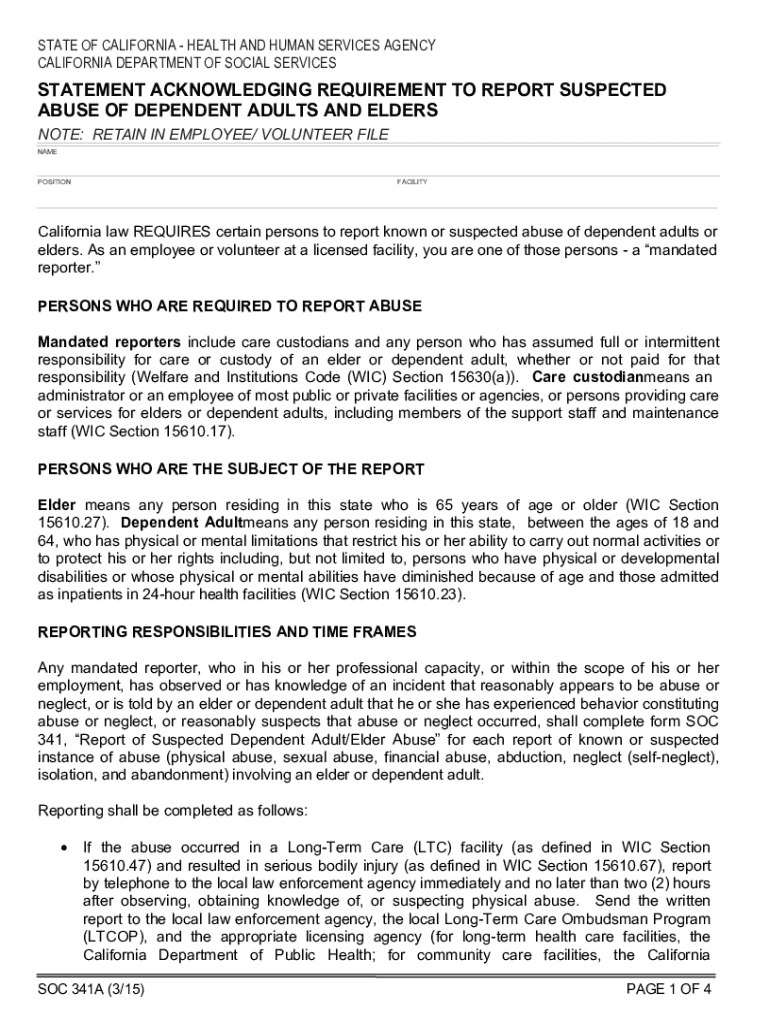
SOC341A Statement Acknowledging Requirement To Report Suspected Abuse Of Dependent Adults And Elders Form
Use a SOC341A pdf STATEMENT ACKNOWLEDGING REQUIREMENT TO REPORT SUSPECTED ABUSE OF DEPENDENT ADULTS AND ELDERS template to make your document workflow more streamlined.
What the SOC341A form records
The SOC341A Statement Acknowledging Requirement To Report Suspected Abuse Of Dependent Adults And Elders Form records a person’s acknowledgment of the duty to report suspected abuse involving a dependent adult or elder. In practice, the authorized organization completes the identifying and acknowledgment fields, assigns the responsible signer, and preserves the signed record. signNow can receive the SOC341A PDF, detect or accept fillable fields, route it for electronic signature, and retain the completed document with an audit trail. State reporting rules and agency instructions still control the underlying duty, timing, and submission process.
Who uses the SOC341A form
Adult protective services
Adult protective services teams use the SOC341A to document required reporting acknowledgments and route completed records through controlled signNow workflows.
Care organizations
Healthcare and residential-care organizations use the SOC341A when authorized staff acknowledge reporting duties involving dependent adults or elders.
Recommended SOC341A workflow setup
Configure the SOC341A workflow around signer identity, evidentiary records, protected information, and the retention rule applicable to the completed document.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Electronic signature with clear signer intent |
| Audit trail | Enabled for every SOC341A transaction |
| Document retention | Six years if HIPAA applies |
| Encryption | TLS 1.2/1.3 and AES-256 |
Complete SOC341A in signNow
Use this sequence to prepare the SOC341A, route it to the correct signer, and preserve evidence of the completed acknowledgment.
Upload form:
Upload the SOC341A PDF. Check fields:
Review detected fields and add missing acknowledgment, date, and signature fields. Assign roles:
Assign every field to the authorized reporter or signer. Send form:
Send the SOC341A through signNow’s email or signing-link workflow. Store evidence:
Download the completed record and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Ways to send and sign SOC341A
- Use the signNow web app when preparing the SOC341A, placing required acknowledgment, reporter, and signature fields before sending the completed form.
- Use the signNow mobile app when authorized staff need to review or sign the SOC341A from an iOS or Android device.
- Use kiosk mode when a facility employee assists an individual who must acknowledge the SOC341A on a managed shared device.
- Use a shareable signing link when distributing the SOC341A to a defined group, while confirming each signer’s identity and access.
How the SOC341A audit trail works
The audit trail records technical events around the SOC341A acknowledgment, helping reviewers connect the signer, document, timing, and completed record.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Log actions:
Export evidence:
Platform requirements for SOC341A
The SOC341A workflow runs through signNow in supported desktop browsers and mobile applications. Use an internet connection protected by TLS, and confirm that the device can display the complete form before signing.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS desktop access Mobile apps iOS and Android mobile apps
Organizations handling sensitive SOC341A records should use managed Windows, macOS, iOS, or Android devices, controlled accounts, and restricted storage. Enterprise deployments may also configure SSO, API access, and certificate or long-term-validation requirements according to their compliance policy.
Security controls for SOC341A records
Transport encryption:
Storage encryption:
Control assurance:
Security certification:
Health information:
Signer authentication:
Best practices for SOC341A records
Accurate field mapping, controlled access, complete audit evidence, and a documented retention decision help organizations manage this sensitive acknowledgment responsibly.
Verify the SOC341A source before sending
Export the audit trail with the form
Match retention to the governing rule
Restrict access to sensitive disclosures
Privacy pitfalls for SOC341A records
Completed SOC341A records can expose names, allegations, and identifying details when recipients or storage permissions are configured too broadly. A signer may acknowledge the reporting duty without the workflow capturing clear electronic consent and intent to sign. Forwarding a completed SOC341A through personal email can create uncontrolled copies outside the organization’s access policy. Using the wrong state procedure can cause disclosure, retention, or reporting steps to conflict with local elder-abuse requirements.
SOC341A rollout and retention
Prepare, route, complete, and archive the SOC341A while applying the retention rule connected to the record’s actual contents and use.
Prepare the form:
Start the trial:
Complete signing:
Retain six years:
Export evidence:
Review access:
Check state law:
Archive securely:
Legal standing of SOC341A signatures
A completed SOC341A may provide evidence of acknowledgment when the signer intended to sign, consented to electronic records, can be attributed to the transaction, and the record remains reproducible. ESIGN and UETA support electronic signatures, but they do not override exclusions such as wills, court orders, or family-law decrees.

Troubleshooting SOC341A workflows
These answers address field assignment, signer access, audit evidence, sensitive information, plan selection, and legal limits affecting SOC341A processing.
Upload the original SOC341A PDF again and confirm that required fields are assigned to the intended signer. signNow Business supports templates and audit trails for correcting field placement before sending.
Review the recipient email address, spam filtering, and signing-link settings. signNow Business provides email delivery and shareable links; resend only after confirming the authorized recipient for this sensitive form.
Use signNow’s audit trail to review signer identity, timestamps, and actions. ESIGN and UETA focus on intent, consent, attribution, and record reproducibility rather than a specific signature image.
A HIPAA workflow is relevant only when the SOC341A record contains protected health information. signNow states HIPAA compliance requires a business associate agreement, so confirm that requirement before processing PHI.
Business includes legally binding eSignatures, templates, audit trails, and mobile apps at $8/user/month with annual billing. Business Premium adds bulk send and kiosk mode at $15/user/month annually.
Do not use electronic signing to replace a legally required notarial act, court filing, or excluded document. ESIGN’s exceptions include wills, court orders, and family-law decrees; verify the applicable state rule.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.