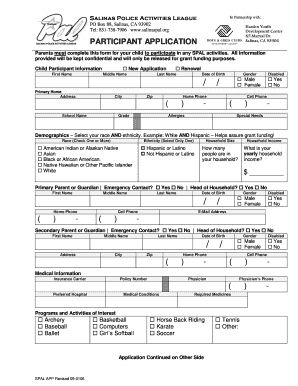
Participant Application Salinas Police Activities League Form
Use a Participant Application Salinas Police Activities League template to make your document workflow more streamlined.
What this participant application does
The Participant Application Salinas Police Activities League Form records an individual’s request to participate in a Salinas Police Activities League program and captures the information needed for review, consent, and enrollment. The exact fields depend on the official form version supplied by the program. With signNow, an authorized sender uploads that document, reviews detected fillable fields, assigns the participant or responsible adult, and sends it for electronic signature. The completed PDF and Audit Trail can then be downloaded and retained with the application record.
How the participant application workflow works
The signNow workflow keeps the official application intact while moving it from preparation through signature and documented storage.
Upload: Upload the official application PDF. Prepare: Auto-detect and verify fillable fields. Route: Send assigned fields to the signer. Archive: Store the signed PDF and Audit Trail.
Complete the participant application in signNow
Use this sequence to prepare, route, sign, and preserve the Participant Application Salinas Police Activities League Form.
Upload form:
Upload the official participant application PDF to signNow. Review fields:
Let signNow detect fillable fields, then review them. Send application:
Add the participant or parent signer and send. Store records:
Download the completed PDF and audit trail.
Platform requirements for signing
Complete the Participant Application Salinas Police Activities League Form through Chrome, Firefox, Safari, or Edge on Windows 10, macOS, iOS, or Android. signNow protects data in transit with TLS 1.2/1.3 and provides mobile apps for reviewing and signing applications.
Browsers Chrome, Firefox, Safari, and Edge Operating systems Windows 10, macOS, iOS, and Android Secure access TLS 1.2/1.3 and signNow mobile apps
Organizations should manage access through approved devices and role-based accounts. Where participant information is sensitive, configure stronger signer authentication, restrict downloads, and preserve the signed PDF with its Audit Trail. Enterprise deployments can evaluate API access, SSO provisioning, and certificate requirements against their internal security policy.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Key features for this participant application
signNow supports the specific handling sequence for this form: prepare the official PDF, assign the signer, capture evidence, and preserve the completed application.
Field preparation
Upload the official participant application and let signNow detect likely fillable areas before staff verify each field and assign the correct signer.
Signer routing
Route the application by email or signing link so the participant or responsible adult can review and sign without exchanging printed copies.
Audit evidence
Capture timestamps, signer actions, and completion evidence in an Audit Trail connected to the finished application record.
Mobile signing
Review and sign from supported desktop or mobile environments while keeping the official application layout intact.
Controlled access
Apply role-based access and controlled storage when participant details, consent information, or health information appear in the signed document.
System connections
Connect completed applications with Google Drive, Box, Microsoft 365, or another supported system for organized record handling.



Recommended participant application setup
Configure the application workflow around signer identity, evidence preservation, controlled access, and the retention rule applicable to the completed record.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Electronic signature with signer intent |
| Audit trail | Enabled with exported completion evidence |
| Document retention | 6 years for HIPAA records (45 CFR §164.530(j)) |
| Encryption | TLS 1.2/1.3 and AES-256 at rest |
What the participant application audit trail records
The Audit Trail separates the signed Participant Application Salinas Police Activities League Form from evidence showing who acted, when they acted, and how the record was completed.
Authenticate signer:
Timestamp action:
Track events:
Seal record:
Create certificate:
Export evidence:
Signer authentication and digital evidence
PKI signatures:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Signer evidence:
Retention practices for participant applications
Retain the signed application, audit evidence, and sensitive participant information according to the record category and applicable U.S. rule.
Apply the correct retention period
Export the complete audit trail
Restrict access to sensitive records
Archive signed applications securely
Retention schedule for application records
Choose the record class before archiving the signed application; the form name alone does not establish a universal retention period.
Six years: HIPAA-covered records
Three to six years: tax records
Three years: payroll records
Five years: injury records
Thirty years: exposure records
Privacy pitfalls in participant applications
Including unnecessary participant details in the signed PDF can expose personal information to every recipient and stored-copy viewer. Failing to capture electronic consent before signing can weaken evidence that the participant understood and agreed to the digital process. Sending the application from a shared account can make signer attribution and staff accountability harder to establish. Leaving completed applications in broad-access folders can expose addresses, emergency contacts, or health information beyond authorized personnel.
Key performance indicators that demonstrate SignNow's proven track record.
Troubleshooting participant applications
These answers address field preparation, signer delivery, legal evidence, privacy controls, and retention for the Participant Application Salinas Police Activities League Form.
Upload the official PDF again and check that it is readable before using auto-detection. signNow lets the sender review and adjust detected fields before assigning the participant or responsible adult as signer.
Confirm the signer’s email address and resend the signing request from the signNow document. If stronger identity evidence is needed, configure SMS OTP or another available authentication method before delivery.
A Business subscription includes legally binding eSignatures, templates, Audit Trails, and mobile apps. Business Premium adds bulk send and kiosk mode, which may help when staff process repeated participant applications.
Electronic signing can support U.S. transactions under ESIGN and applicable state law when intent, consent, attribution, and record retention are established. For consumer-facing records, review the disclosure requirements in 15 U.S.C. §7001(c).
If the application contains protected health information, signNow identifies HIPAA compliance as requiring a BAA. The organization must still apply its own privacy, access, and retention controls under HIPAA, including 45 CFR §164.530(j).
Download the completed PDF and Audit Trail after signing, then place both in the authorized records repository. Preserve timestamps, signer details, and action history so the application can be reviewed without relying only on the live workflow.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.