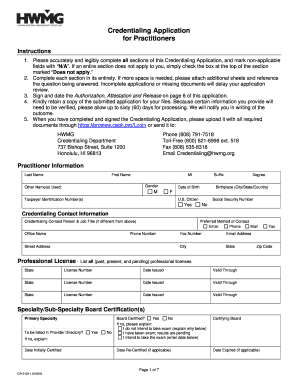
Cr E 03 1 010818 Application Practitioner Form
Use a CR E 03 1 010818 Application Practitioner doc template to make your document workflow more streamlined.
What this practitioner application form does
The Cr E 03 1 010818 Application Practitioner Form is a practitioner-facing application document used to collect information, acknowledgments, and signatures from an applicant. Because the supplied form name does not identify an issuing agency, filing deadline, statutory fee, or required fields, those details should be confirmed against the source instructions before submission. In signNow, upload the document, review auto-detected fillable fields, assign signer roles, send the application, and store the completed PDF with its audit trail. ESIGN and UETA generally recognize qualifying electronic signatures when intent, consent, attribution, and record reproduction are established.
Who uses this practitioner application form
Practitioners
Practitioners can use the form to collect applicant information, required acknowledgments, and signatures in one controlled workflow. The sender should verify that every field reflects the source document and that the applicant receives any disclosures required for the transaction.
Applicants
Applicants complete assigned fields and sign only after reviewing the application. Administrative reviewers can check the completed PDF, audit trail, and required attachments before storing the record under the organization’s retention policy.
Complete the practitioner application in signNow
Follow this document-specific sequence to prepare, route, sign, and retain the Cr E 03 1 010818 Application Practitioner Form.
Upload form:
Upload the practitioner application PDF. Check fields:
Review auto-detected fields and correct labels. Assign roles:
Assign practitioner and applicant roles. Send form:
Send the application through signNow. Retain evidence:
Review signatures and download records.
How the audit trail records each application
The audit trail separates signer identity, event timing, document integrity, and export evidence for the completed practitioner application.
Authenticate signer:
Capture timestamps:
Check document integrity:
Seal record:
Review events:
Export evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Platform requirements for this form
Complete the Cr E 03 1 010818 Application Practitioner Form in current Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides iOS and Android apps for mobile document access and signing. Use an internet connection that supports TLS 1.2 or TLS 1.3.
Browsers Chrome, Firefox, Safari, Edge Desktop systems Windows and macOS desktops Mobile apps iOS and Android signNow apps
Organizations should manage access through approved devices, role-based permissions, and controlled storage. Enterprise workflows may use API access and advanced signer authentication; confirm the selected signNow plan, identity controls, and retention policy before routing applications containing sensitive information.
Security for practitioner applications
Transport encryption:
Stored data:
Independent assurance:
Security management:
Electronic signatures:
Health information:



Recommended workflow setup
Configure the application workflow around signer attribution, evidence preservation, access control, and the retention rule that applies to this document.
| Setting | Recommendation |
|---|---|
| Authentication method | Email invitation with SMS OTP |
| Signature type | Electronic signature with recorded intent |
| Audit trail | Enabled for every completed application |
| Document retention | Organization policy and applicable law |
| Encryption | TLS 1.2/1.3 and AES-256 |
Processing stages for the application form
The form moves from preparation through delivery, signature collection, and controlled archival; no filing deadline is provided for this document name.
Prepare document
Deliver to signers
Await signatures
Archive completion
Best practices for completing this form
Use the source document, signer roles, audit trail, access controls, and applicable consent rules as one review checklist for this application.
Verify detected fields against the source
Retain the audit trail with the signed form
Limit access to sensitive application data
Document electronic consent before signing
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

Risks from improper form handling
Missing required fields
Weak attribution
Missing audit trail
Unproven consent
Troubleshooting the practitioner application form
Resolve field, signer, plan, authentication, and recordkeeping issues before completing the Cr E 03 1 010818 Application Practitioner Form.
Open the uploaded Cr E 03 1 010818 Application Practitioner Form in signNow and verify that each detected field has the correct role, location, and required status before sending. The Business plan includes templates and audit trails; field corrections do not alter the original source file.
Use signNow’s recipient-role assignment to place the practitioner, applicant, and reviewer fields with the correct signer. Send a test copy first, then use the audit trail to confirm each participant’s actions and timestamps.
The Business plan supports legally binding eSignatures and audit trails. For healthcare information, signNow identifies HIPAA compliance as requiring a Business Associate Agreement; confirm that agreement and your workflow before collecting protected health information.
A signer can open the signNow invitation without creating an account when the sender permits guest signing. If stronger attribution is required, configure SMS OTP or another available authentication method before sending this application.
Business and Business Premium subscriptions include 100 signature invites per user annually, with overage fees. Business Premium adds bulk send, while Enterprise adds advanced signer authentication and conditional or formula fields.
Export the completed PDF and its signNow audit trail together. The audit trail records signing actions, timestamps, and related event details, while ESIGN and UETA require intent, attribution, consent, and record reproducibility for electronic transactions.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.