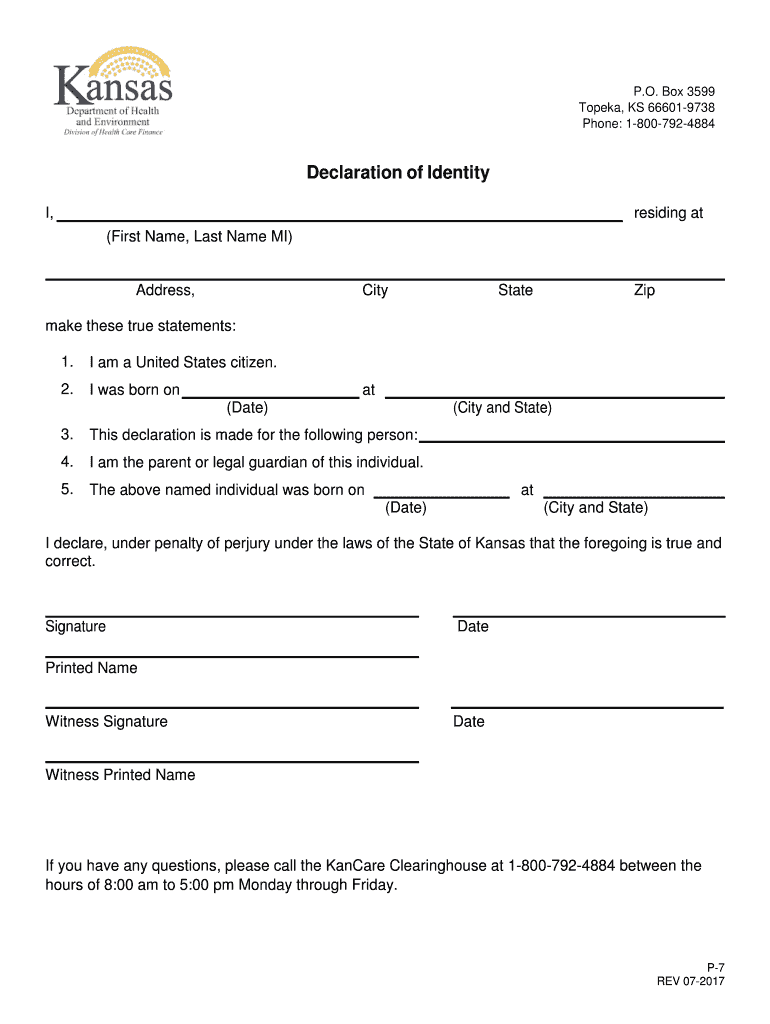
HIPAA Compliant Authorization To Disclose Information To Kdhe
Use a HIPAA Compliant Authorization To Disclose Information To KDHE template to make your document workflow more streamlined.
What the Kdhe authorization does
A HIPAA Compliant Authorization To Disclose Information To Kdhe is a written or electronic patient permission that allows a healthcare provider to release identified protected health information to Kdhe for a stated purpose. The form should identify the patient, recipient, information categories, purpose, expiration, signature, and date. A provider reviews those elements before disclosure and retains evidence of consent. signNow can upload the form, detect fillable fields, route it for signature, and preserve the completed document with an audit trail. HIPAA retention generally lasts six years under 45 CFR 164.530(j).
Privacy pitfalls in Kdhe disclosures
The signed authorization may expose diagnoses or treatment details if its recipient, transmission method, or stored copy is not access-controlled. A vague description of records or purpose can make the Kdhe disclosure broader than the patient intended. Missing expiration details can leave staff uncertain whether the authorization still permits release at the time of processing. Shared accounts or unprotected download links can weaken evidence that the authorized patient approved the specific disclosure.
How this authorization works
This authorization connects a patient’s consent to a defined disclosure, giving Kdhe a documented basis for receiving specified health information.
Identify the parties: The authorization identifies the patient, recipient, records, purpose, and expiration before disclosure occurs. Review and sign: The patient or personal representative reviews the completed authorization and signs with demonstrated intent. Verify authorization: The healthcare organization verifies scope, identity, and any required consent before releasing records. Disclose and retain: The recipient receives only the authorized information, while the signed record and audit trail remain available.
Complete the Kdhe authorization online
Use this sequence to prepare, sign, and retain the HIPAA authorization before Kdhe receives protected health information.
Upload form:
Upload the Kdhe authorization template to signNow. Add fields:
Place fields for patient, recipient, scope, signature, and date. Send request:
Send the authorization to the required signer. Archive record:
Store the signed PDF and audit trail securely.
Choose a signing method for Kdhe
- Use the signNow web app when staff prepare the Kdhe authorization, place fields, and monitor completion from a desktop browser.
- Use the signNow mobile app when a patient or representative needs to review and sign the authorization from an iOS or Android device.
- Use kiosk mode when staff and a patient complete the authorization together on a managed device, without transferring control between separate sessions.
- Use a shareable signing link when the organization distributes the same approved authorization entry point to an identified patient population.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended authorization setup
Configure the Kdhe authorization workflow around verified signer identity, limited disclosure scope, documented completion, and HIPAA retention requirements.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Certificate of completion with timestamps |
| Document retention | 6 years under HIPAA 45 CFR 164.530(j) |
| Encryption | TLS 1.2/1.3 and AES-256 |
What the audit trail records
For this Kdhe authorization, the audit trail connects the patient’s signing event with the final disclosure document and its completion evidence.
Authenticate signer:
Capture timestamps:
Hash document:
Seal evidence:
Retrieve records:
Export archive:
Retain and protect authorization records
A signed HIPAA authorization is useful only when its scope, evidence, and retention remain clear throughout the disclosure process.
Apply the six-year HIPAA retention rule
Export the signed record and audit trail
Restrict access to disclosure records
Check scope before releasing records
Retention schedule for Kdhe records
Retain the authorization and supporting documentation according to HIPAA’s six-year rule, while checking any longer state or organizational requirement.
Six years: Kdhe authorization records
Six years: disclosure documentation
Six years: privacy procedures
Six years: compliance evidence
Six years: related records
Risks of incomplete authorization
Invalid authorization
Excess disclosure
Identity dispute
Retention violation
Legal standing and business value
A complete Kdhe authorization documents patient intent, recipient, purpose, scope, and expiration, reducing uncertainty before protected information is released. Electronic execution may be recognized under ESIGN and UETA when consent, attribution, intent, and reproducible records are established; HIPAA privacy requirements still govern the disclosure itself.

Organizations that use this authorization
The Kdhe authorization is relevant to healthcare organizations that must document patient permission before releasing specified protected health information.
Solo medical practices use the authorization to collect a patient’s consent for a defined Kdhe disclosure without requiring an in-office paper exchange. Regional healthcare organizations use reusable signNow templates, role-based access, and audit trails to coordinate Kdhe authorizations across multiple departments and release teams. Enterprise health systems use centralized administration, delegated sending, and advanced signer authentication when Kdhe disclosures involve sensitive records and distributed patient populations.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.



Troubleshooting Kdhe authorization workflows
Resolve signature, scope, retention, and compliance questions before releasing protected health information through a Kdhe authorization workflow.
signNow’s Business plan includes templates, audit trails, and legally binding eSignatures. For HIPAA workflows, confirm that the required Business Associate Agreement is in place before uploading or transmitting protected health information.
The HIPAA authorization must identify the requested information and disclosure purpose. Use signNow’s fields to capture the patient, recipient, description, expiration, signature, and date; incomplete scope can prevent a defensible release.
The signer can open the signNow invitation, complete required fields, and sign from a browser or mobile app. If access fails, verify the invitation address, resend the request, or use a controlled signing link.
Business includes audit trails, while Business Premium adds bulk send and Enterprise adds advanced signer authentication. Select the plan according to volume and identity-verification requirements, then confirm HIPAA terms before processing PHI.
HIPAA requires covered entities to retain required documentation for six years from creation or the last effective date under 45 CFR 164.530(j). Export the signed authorization and signNow audit trail into your controlled archive.
Electronic signatures can satisfy ESIGN and UETA requirements when intent, consent, attribution, and record reproducibility are established. For consumer-facing records, provide the required electronic-record disclosure under 15 U.S.C. §7001(c).
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.