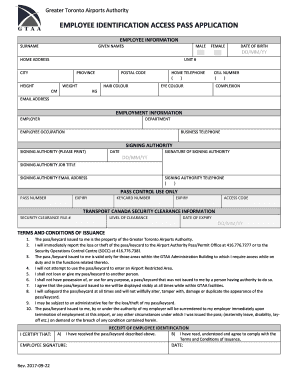
Application For Restricted Area Identity Card Form
Use a Application For Restricted Area Identity Card template to make your document workflow more streamlined.
What this identity-card application does
The Application For Restricted Area Identity Card Form is a facility-specific request for personal identification and authorization to access a controlled area. Its exact fields, supporting documents, approving authority, and issuance rules depend on the organization that provides the form. In signNow, a sender uploads the approved PDF, reviews or adds fillable fields, assigns applicant and approver roles, and sends the document for completion. Signatures, timestamps, recipient actions, and document history can be preserved with the completed application. SignNow routes evidence; it does not issue the identity card or decide eligibility.
Who benefits from this application workflow
The workflow fits organizations that issue, approve, or administer restricted-area identity credentials and need a traceable application record.
A small contractor can use the application to request controlled site access, route the form to a designated facility approver, and preserve a signed record without maintaining a paper circulation process. A healthcare or laboratory organization can coordinate applicant details and authorization across departments, while limiting completed identity-card applications and audit records to personnel with an access-related need. A large construction or infrastructure enterprise can standardize application routing across sites, use shared templates, and retain approval evidence for each restricted-area access request under its internal security policy.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses this identity-card application
Applicants and facility security
Applicants provide the identifying and access-related information requested by the facility, then sign the Application For Restricted Area Identity Card Form. Facility administrators or security personnel review the submitted application, confirm internal requirements, and approve or reject the request according to site policy. SignNow can route the document, capture signatures, and preserve an audit trail, but it does not issue the identity card.
Contractors and authorized personnel
Contractors, employees, vendors, and visitors may use this application when a site requires documented authorization for restricted-area access. The form is specific to the issuing organization’s process, so users should confirm required attachments, identity checks, approvals, expiration dates, and submission instructions before sending a completed copy.
How this application works in signNow
The signNow flow turns the facility’s Application For Restricted Area Identity Card Form into a controlled signature request without deciding who qualifies for access.
Upload form: Upload the facility’s application PDF Prepare fields: Review detected fields and add recipients Route application: Send applicant and approval requests Store record: Complete signatures and preserve evidence
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Steps to complete the application
Use this sequence to prepare, route, sign, and document the Application For Restricted Area Identity Card Form in signNow.
Upload form:
Upload the facility-approved PDF Prepare request:
Review fields and add recipients Send application:
Send for applicant and approval signatures Archive evidence:
Download signed PDF and audit trail
Recommended setup for this application
Configure the Application For Restricted Area Identity Card Form around facility approval, restricted access, signer authentication, and documented evidence.
| Setting | Recommendation |
|---|---|
| Authentication and provisioning | Use two-factor authentication with role-based access |
| Signature type | Use an electronic signature with clear intent |
| Audit trail | Enable detailed recipient and timestamp history |
| Document retention | Follow the issuing facility’s written retention policy |
| Encryption | Use TLS in transit and AES-256 at rest |
Security controls for this application
Two-factor authentication:
PKI signatures:
X.509 certificates:
ID verification:
Signer authentication:
Audit evidence:
Mobile options for this application
The signNow mobile apps support completing the Application For Restricted Area Identity Card Form on iOS and Android, including offline signing and camera capture.
Mobile apps iOS and Android apps Offline mode Offline signing available Camera capture Camera-based document capture
Use camera capture when the application exists on paper, then review every extracted value before signing. Offline work can support field access without connectivity; reconnect before sending the completed Application For Restricted Area Identity Card Form so its audit record can be finalized.
How the audit trail records this application
After the Application For Restricted Area Identity Card Form is sent, signNow records identity, timing, document-integrity, and retrieval events separately from the form’s visible fields.
Authenticate signer:
Capture timestamp:
Hash document:
Seal document:
Log activity:
Export audit trail:
Best practices for this application
Accurate field assignment, controlled authentication, and documented retention help organizations process this restricted-area identity application consistently.
Confirm the facility’s required information
Assign every field to the correct signer
Match authentication to access sensitivity
Archive the application and audit trail
Challenges when completing this application
Applicants may submit an outdated facility-specific version, leaving required access details or approving-authority fields unavailable during review. A signature request can reach the wrong recipient when applicant and facility approver roles are not assigned separately. Restricted-area identity information may be exposed when completed PDFs and audit trails are stored in uncontrolled email folders. A completed signature does not replace facility approval, identity verification, badge issuance, or any required in-person security screening.
Legal standing and limits
An electronically signed application may be admissible under the ESIGN Act, 15 U.S.C. chapter 96, and applicable UETA or New York ESRA rules when intent, consent, attribution, and record retention are established. Those laws do not replace facility approval, identity checks, notarization requirements, or access-card issuance rules.

Troubleshooting this application workflow
These answers address field detection, recipient routing, plan selection, legal effect, audit evidence, and protection of restricted-area application information.
Upload the facility-issued PDF again and inspect the detected fields before sending. signNow templates can standardize recurring applications, but the facility’s current form remains the authoritative source for required information and approvals.
Separate the applicant and facility approver as recipients, then assign each signature, date, and acknowledgment field to the correct person. A field-assignment error can produce a signed document without the approval the facility requires.
Business includes legally binding eSignatures, templates, and audit trails at $8 per user monthly when billed annually. Business Premium is $15 and adds bulk send, while Enterprise is $30 and adds advanced signer authentication.
SignNow supports ESIGN and UETA compliance for electronic signatures. The facility must still determine whether its security policy, state law, or issuing process requires identity proofing, notarization, an in-person check, or a paper submission.
Use signNow’s audit trail to review authentication, timestamps, recipient actions, and document history. Export the completed application and audit evidence together, then apply the issuing organization’s access-control and retention policy.
For identity or access information, use restricted recipient permissions and stronger authentication such as two-factor authentication or SMS OTP when configured. HIPAA, FERPA, or another privacy rule applies only when the application’s data and organization fall within that rule’s scope.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.