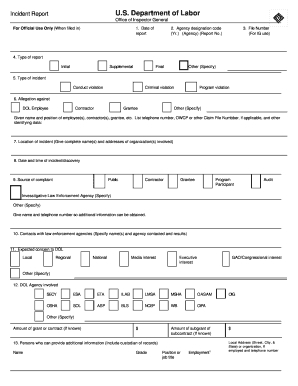
Attachment C Incident Report Form Oig 1 156 And Instructions Wdr Doleta
Use a Attachment C Incident Report Form OIG 1 156 And Instructions Wdr Doleta template to make your document workflow more streamlined.
What this incident report form does
Attachment C Incident Report Form Oig 1 156 And Instructions Wdr Doleta is an incident-reporting document used to capture a workforce-development event in a consistent record. Complete the form with the facts requested by its instructions, identify the people and program context involved, and route it to the responsible reviewer. With signNow, a sender uploads the document, checks detected fields, adds signers or reviewers, sends it electronically, and stores the completed form with its audit trail. The form’s instructions and program policy control what must be reported.
Who benefits from this incident report form
The form is most useful wherever workforce-development incidents require consistent facts, accountable review, and a retrievable signed record.
Solo workforce-development consultants can use the incident report form to document a participant or program event, add factual details, and route the completed record for review without rebuilding the document. Workforce program administrators can standardize incident submissions across offices by using one controlled form, assigning review responsibilities, and preserving completed records with an associated audit trail. Large workforce-development organizations can connect incident reporting with existing systems, apply role-based access, and retain consistent evidence for internal investigations, grant administration, and oversight reviews.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses the completed report
Program staff
Workforce-development staff can use Attachment C for incident narratives, participant or program details, acknowledgments, and internal review routing. Use the exact labels and instructions supplied with the source document, because this page does not establish additional reporting fields.
Review teams
Supervisors and administrators can review completed incident reports, add required approvals, and preserve the signed form with its audit trail. The workflow can be adapted to contracts, consent records, or related documents only when the governing program permits it.
How the signNow workflow works
The signNow process keeps the document itself, assigned actions, and completion evidence connected from upload through archival.
Upload: Upload the Attachment C document Prepare fields: Review detected fields and add missing fields Route: Assign reviewers and signers, then send Complete: Collect signatures and store the completed record
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended workflow configuration
Configure the incident-report workflow around controlled access, attributable signatures, and records that remain available for review.
| Setting | Recommendation |
|---|---|
| Authentication method | Email link with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enable completion certificate and action history |
| Document retention | Follow the applicable program record policy |
| Encryption | TLS 1.2 or 1.3 and AES-256 |
Signer authentication and certificate controls
PKI options:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Audit trail:
Ways to send and sign the report
- Use the signNow web app when staff need to upload Attachment C, place fields, assign reviewers, and monitor the report from a desktop workflow.
- Use the signNow mobile app when an authorized field worker must review or sign the incident report away from an office, subject to device policy.
- Use kiosk mode when supervised staff need to complete repeated incident-report signing on an organization-managed device with controlled access.
- Use a shareable signing link when approved recipients need direct access to the assigned Attachment C workflow without a separate account-creation step.
Incident report processing stages
Use these stages to separate preparation, review, signing, and archival for each completed incident report.
Prepare the report
Deliver to reviewers
Complete signatures
Archive the record



Challenges when completing Attachment C
Incident facts may be entered inconsistently when staff interpret Attachment C instructions differently, making later review harder and increasing the need for clarifying follow-up. Unassigned fields or incorrect signer roles can leave required explanations, acknowledgments, or approvals incomplete before the report reaches its designated reviewer. A scanned report without a controlled audit trail may make it harder to establish who reviewed each version and when the completed record was finalized. Storing the completed report separately from its audit trail can weaken the record’s context during an internal review or oversight request.
Best practices for completing Attachment C
Careful field review, controlled routing, and complete record preservation reduce avoidable issues when Attachment C is completed electronically.
Check the source document before sending
Assign every field deliberately
Separate facts from conclusions
Preserve the complete record
Platform requirements for Attachment C
Open the Attachment C workflow in Chrome, Firefox, Safari, or Edge on Windows or macOS. signNow also provides mobile applications for iOS and Android, allowing authorized users to review and sign from supported devices. Use an organization-approved connection and keep the device software current.
Browsers Chrome, Firefox, Safari, Edge Operating systems Windows, macOS, iOS, Android Mobile apps signNow mobile applications
Organizations handling incident reports should use managed devices, role-based access, and approved storage locations. Teams needing system-to-system routing can evaluate signNow API access and integrations such as Microsoft 365, Google Drive, Box, or Salesforce. Confirm accessibility, authentication, and retention requirements with the responsible program administrator before deployment.
Troubleshooting this incident report workflow
These answers address field detection, signer identity, electronic consent, plan capabilities, and secure record handling for Attachment C workflows.
Upload the original PDF again and confirm that each detected field is assigned to the correct signer. signNow templates can preserve field placement for repeated Attachment C workflows, while the sender remains responsible for checking the form against its instructions.
Use signNow’s audit trail and completion certificate to show the signing sequence, timestamps, and recorded actions. ESIGN and UETA focus on intent, consent, attribution, and record reproducibility; the platform does not replace the program’s substantive reporting requirements.
The Business plan includes audit trails and templates. Business Premium adds bulk send, which is useful for distributing repeated workflows, while Enterprise adds advanced signer authentication. Select the plan according to volume and authentication requirements rather than assuming every incident needs bulk delivery.
For consumer-facing electronic records, obtain the required electronic-record disclosure and confirm the signer can access the format. The consent process should also explain how to withdraw consent, as required by ESIGN, 15 U.S.C. §7001(c).
Enable SMS OTP or another approved verification method before sending when the organization needs stronger signer attribution. Advanced authentication availability depends on the selected signNow plan and configured workflow, so document the chosen control in program procedures.
Use signNow’s encryption controls and access permissions, then export the completed document and audit trail to the organization’s approved repository. signNow states TLS 1.2/1.3 in transit, AES-256 at rest, SOC 2 Type II certification, and ISO 27001 certification.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.