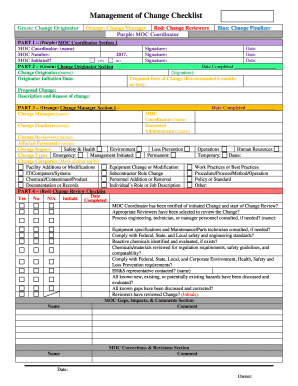
Management Of Change Checklist Form
Use a Management Of Change Checklist template to make your document workflow more streamlined.
What the change checklist records
A Management Of Change Checklist Form documents how a proposed operational, technical, or process change is evaluated, approved, implemented, and reviewed. The person initiating the change records its scope, affected areas, risks, controls, responsible owner, planned timing, and required approvals. Reviewers then sign the checklist to confirm their assigned assessment. With signNow, a sender uploads the form, places or confirms fillable fields, routes them in the required order, and retains the completed document with an audit trail. The exact checklist fields and approval rules remain controlled by the organization using it.
Who uses this change checklist
Operations and engineering
Operations and engineering teams use the checklist to document equipment, software, procedure, or process changes, assign risk reviews, and obtain approvals before implementation. Safety, quality, maintenance, and management reviewers can sign their assigned sections electronically, creating a consolidated change-control record.
Regulated project teams
Regulated facilities, construction teams, and service organizations use the form when a change affects documented procedures, personnel, equipment, or customer delivery. The checklist helps coordinate technical review, safety controls, training evidence, and management authorization without relying on paper circulation.
Complete the change checklist online
Use signNow to prepare, route, and complete the Management Of Change Checklist Form with a traceable electronic signing workflow.
Upload the form:
Upload the Management Of Change Checklist Form to signNow and review detected fields. Review fields:
Confirm names, dates, descriptions, approvals, and signature fields match the change record. Assign participants:
Assign each approval and signature field to the responsible change participant. Send for signature:
Send the completed request and monitor outstanding signatures from the dashboard.
How the audit trail protects approvals
The signNow audit trail records technical events that connect each approval to the completed Management Of Change Checklist Form.
Authenticate signers:
Capture timestamps:
Hash the document:
Seal the record:
Log document actions:
Export evidence:
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Configure the checklist workflow
Configure access, signing, audit, retention, encryption, and user controls before routing change approvals.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS two-factor authentication |
| Signature type | Electronic signature with signer intent |
| Audit trail | Capture timestamps, IP addresses, and actions |
| Document retention | Follow the organization’s approved retention schedule |
| Encryption and provisioning | TLS 1.2/1.3, AES-256, role-based access |
Best practices for change control
A disciplined checklist process connects the proposed change, risk review, approvals, implementation evidence, and signed record.
Record the change scope before routing
Create a controlled approval template
Attach evidence for each approval
Archive the completed record securely
Security for change approvals
Transport encryption:
Stored encryption:
SOC 2 Type II:
ISO 27001:
Signer authentication:
HIPAA safeguards:



Privacy and disclosure pitfalls
Including personal data, credentials, or health information in the change description can expose unnecessary information to every signer and stored-record viewer. Failing to capture electronic consent or signer intent may weaken the evidence supporting a reviewer’s approval under ESIGN and UETA. Assigning every recipient broad access can expose unrelated change records, supporting documents, or restricted operational information. Leaving implementation evidence or required reviewer fields blank can make the completed checklist difficult to interpret during an internal investigation.
Risks of incomplete change records
Approval dispute
Control gap
Evidence challenge
Proof limitation
Business types that use change checklists
The form fits organizations that must document review and authorization before changing controlled work, systems, facilities, or procedures.
Construction contractors use the checklist to route changes to site supervision, safety personnel, and project management before modifying work methods, equipment, or sequencing. Signed approvals help connect field implementation with the project’s documented controls and responsibilities. Healthcare operations teams use it to review changes affecting clinical procedures, systems, facilities, or patient-service workflows. Assigned reviewers can document safeguards, training needs, and authorization while maintaining a searchable electronic record for internal governance. Enterprise manufacturers and technology organizations use the form for cross-functional changes involving engineering, operations, security, quality, and management. Reusable signNow templates and delegated sending help coordinate approvals across locations without recreating the checklist each time.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Troubleshooting the change checklist
Resolve field, routing, authentication, compliance, and recordkeeping questions before relying on a signed Management Of Change Checklist Form.
Upload the Management Of Change Checklist Form to signNow, then use the editor to place or confirm fields for change description, risk review, approvals, implementation evidence, and signatures. Auto-detection can assist, but the sender remains responsible for verifying every field.
The Business plan includes templates, audit trails, mobile apps, and legally binding eSignatures at $8/user/month with annual billing. Bulk send is listed for Business Premium at $15/user/month annually, so repeated distribution may require that plan.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are established. Configure signer authentication, capture the audit trail, and preserve a reproducible copy; state or organizational rules may impose additional requirements.
Use signNow’s audit trail to review signer identity, timestamps, actions, and completion evidence. Export the audit trail with the signed checklist and store both under the organization’s approved change-control retention policy.
For healthcare changes involving protected health information, signNow identifies HIPAA compliance as requiring a business associate agreement. Confirm that the organization has the required BAA and configure access controls before routing the form.
SignNow’s listed Business plan includes legally binding eSignatures, audit trails, templates, mobile apps, ISO 27001, SOC 2, and GDPR support. Advanced signer authentication is listed with Enterprise at $30/user/month annually.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.