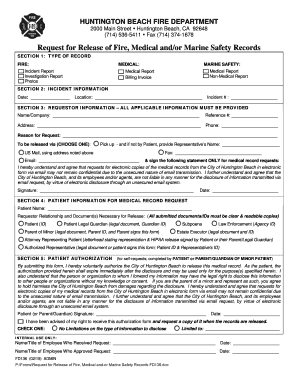
Request For Release Of Fire, Medical Andor Marine Safety Records Form
Use a Request For Release Of Fire, Medical Andor Marine Safety Records template to make your document workflow more streamlined.
What this records release form does
The Request For Release Of Fire, Medical Andor Marine Safety Records Form records a person’s authorization to obtain specified fire, medical, or marine-safety records. It identifies the record subject, requested materials, recipient, purpose, and signer consent so a custodian can evaluate disclosure. Upload the form to signNow, review or place its fields, send it to the authorized signer, and retain the completed document with its audit trail. Medical-record workflows may require HIPAA controls, including a business associate agreement where applicable. ESIGN and UETA generally support electronic signatures when consent, intent, attribution, and reproducible records are established.
Business users for this records release
This form serves organizations that disclose controlled fire, medical, or marine-safety records after confirming authorization and recipient details.
A county fire-records office can use the form to capture a requester’s identity, incident details, authorized recipient, and narrow disclosure purpose before releasing reports. A healthcare records department can route a patient authorization for signature, restrict access to designated staff, and retain evidence supporting the requested medical disclosure. A marine-safety investigation team can collect a signed authorization for incident records, coordinate custodians, and preserve the completed release with its audit history.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
Who uses this records release form
Records custodians
Fire departments, marine-safety offices, medical providers, insurers, attorneys, and authorized representatives use the release to document permission before disclosing identified records. The form should identify the requester, record subject, requested record category, permitted recipient, purpose, and signature evidence.
Authorized requesters
Individuals, estates, employers, insurers, and counsel may request copies of fire, medical, or marine-safety records. Use the form to limit disclosure to the stated records, recipient, purpose, and authorization period.
Privacy and disclosure pitfalls
Broad wording can authorize disclosure of unrelated medical, fire, or marine-safety records beyond the requester’s intended scope. Missing recipient details can prevent a custodian from determining who is authorized to receive the released records. A signature without clear consent language may weaken evidence that the subject understood the requested disclosure. Unrestricted access to signed releases can expose medical details, identity information, or incident data to unauthorized staff.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Choose a sending and signing method
- Use the signNow web app to upload the Request For Release Of Fire, Medical Andor Marine Safety Records Form, review detected fields, and route it to the named signer.
- Use the signNow mobile app when a requester or custodian needs to review, complete, or sign the records release from an iOS or Android device.
- Use kiosk mode for an in-person records counter or office where an authorized individual signs on a managed device without receiving an email invitation.
- Generate a shareable signing link when a department repeatedly receives this release request through a controlled portal or approved intake channel.
Authenticate records-release signers
PKI signatures:
X.509 certificates:
Two-factor authentication:
SMS OTP verification:
ID verification:
Audit trail evidence:
Recommended records-release workflow setup
Configure the release around signer identity, narrow authorization, audit evidence, and the retention rule governing the requested records.
| Setting | Recommendation |
|---|---|
| Authentication method | SMS OTP for external requesters |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Retain completed audit trail with release |
| Document retention | Six years for HIPAA records (45 CFR 164.530(j)) |
| Encryption | TLS 1.2/1.3 in transit and AES-256 at rest |
How signNow records the signing event
The audit trail documents the evidence surrounding this release rather than changing the authorization or expanding the records requested.
Signer authentication:
Timestamp capture:
Document history:
Tamper evidence:
Access events:
Audit export:
Retention periods for released safety records
Retention depends on the information released and the rule governing the underlying record, not solely on the signature date.
Six years: medical records
Five years: injury records
Thirty years: exposure records
Three years: tax records
Policy-defined: release evidence
Best practices for records-release evidence
Precise scope, controlled access, and an exportable signing record help custodians show what was authorized and how the release was completed.
Name every requested record category
Preserve the audit trail with the release
Apply the governing retention rule
Restrict access by disclosure role
Why teams look for DocuSign alternatives
Organizations seek alternatives when they need different pricing models, stronger native automation, simpler bulk affidavit workflows, or more flexible identity-verification options than those available in a legacy envelope-based vendor.

Troubleshooting this records release workflow
These answers address field placement, authorization scope, signer identity, plan limits, electronic-signature evidence, and retention for this records release.
Upload the completed release as a PDF or supported document, then use signNow’s field tools to place signature, date, initials, and consent fields. Business includes templates and audit trails; auto-detection should still be reviewed against every authorization field.
For medical records, signNow identifies HIPAA compliance as requiring a business associate agreement. Configure the workflow with the appropriate BAA and limit recipients, fields, and access to the records-release process.
ESIGN and UETA generally recognize electronic signatures when intent, consent, attribution, and record retention are established. For consumer-facing releases, provide the ESIGN paper-record disclosure required by 15 U.S.C. §7001(c).
Use signNow SMS OTP or another available authentication method when email-only attribution is insufficient. Enterprise adds advanced signer authentication; record the selected method in the completed audit trail.
Business Premium includes bulk send, while Business does not. A single records release can use Business, but repeated individualized requests may require Business Premium or a higher plan.
Healthcare records require a retention policy aligned with HIPAA 45 CFR 164.530(j), which specifies six years from creation or the last effective date. Confirm longer state or program requirements before deletion.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.