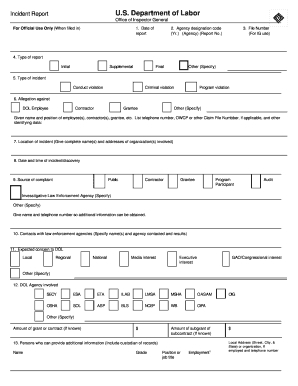
Attachment C Incident Report Form Oig 1 156 And Instructions
Use a Attachment C Incident Report Form OIG 1 156 And Instructions template to make your document workflow more streamlined.
What Attachment C records and why
Attachment C Incident Report Form Oig 1 156 And Instructions is an incident-reporting document used to capture facts, circumstances, and supporting details about a reported event. Its instructions guide the preparer through identifying the incident, documenting relevant observations, and confirming the report for review. With signNow, an organization can upload the form, detect or place fillable fields, route it to assigned participants, and preserve the completed document with an audit trail. The form’s issuing authority, filing deadline, and required attachments should be confirmed from the accompanying instructions or agency guidance before submission.
Who works with Attachment C
Incident investigators
Investigators and program staff use Attachment C to document an incident’s date, location, people involved, observed facts, and follow-up information before internal or agency review.
Compliance administrators
Compliance and records teams use the completed report, attachments, and audit trail to support review, controlled disclosure, and consistent retention without changing the original submission.
Business types using Attachment C
Attachment C is most useful where incident facts must move through defined reviewers and remain reproducible after completion.
A small compliance office can replace handwritten circulation with one controlled Attachment C workflow, keeping assigned reviewers, signatures, and the completion record together. A healthcare organization can route incident details to authorized staff while applying HIPAA controls when the report contains protected health information and a BAA is required. A government or enterprise program can standardize multiple Attachment C submissions with templates, role-based routing, audit trails, and controlled archival across departments.
These tasks are executed by both individual contributors and centralized administrators depending on organizational policy and required controls.
How Attachment C works in signNow
The signNow workflow keeps the original report identifiable while adding controlled fields, signer routing, and completion evidence.
Upload form: Upload the original Attachment C PDF. Add fields: Detect or place fields for report data. Send workflow: Route assigned sections to recipients. Preserve record: Store the signed report and audit trail.
Quick steps for Attachment C
Use the original Attachment C file, verify every assigned field, and preserve the completed report with its audit evidence.
Upload form:
Upload the official PDF into signNow. Check fields:
Review detected fields and add missing ones. Assign roles:
Assign each field to the right participant. Send report:
Send the report for completion and signature. Archive records:
Download the signed PDF and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
How the Attachment C audit trail works
signNow records each signing event around Attachment C, creating a chronological evidence record separate from the form’s visible content.
Authenticate signer:
Capture timestamps:
Hash document:
Seal record:
Link events:
Export trail:
Recommended Attachment C setup
Configure the report workflow around signer identity, evidence preservation, controlled access, and the issuing agency’s records schedule.
| Setting | Recommendation |
|---|---|
| Authentication method | Email plus SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Enabled with completion certificate |
| Document retention | Issuing agency schedule |
| Encryption | TLS 1.2/1.3 and AES-256 |
Signer authentication for Attachment C
Email authentication:
Two-factor authentication:
ID verification:
PKI signatures:
X.509 certificates:
Evidence capture:
Technical requirements for Attachment C
Attachment C can be prepared in signNow through Chrome, Firefox, Safari, or Edge on Windows or macOS. Mobile access is available through iOS and Android applications, while encrypted connections use TLS 1.2 or TLS 1.3.
Browsers Chrome, Firefox, Safari, Edge Operating systems Windows 10+, macOS, iOS, Android Connection TLS 1.2 or newer
Organizations should use managed devices when reports contain sensitive incident details. Configure user provisioning, access permissions, and any API or single sign-on controls according to internal policy. Confirm that recipients can open, complete, review, and download the final PDF before routing the report.



Retention practices for Attachment C records
Retention depends on the issuing agency, record category, and applicable U.S. records schedule; preserve the report and its signing evidence as one controlled file set.
Apply the issuing agency’s retention schedule
Export the signed record promptly
Limit access to incident records
Separate drafts from final reports
Privacy challenges when completing Attachment C
Entering incident facts into the wrong field can change meaning and require a corrected report or reviewer follow-up. Sharing the completed PDF without its audit trail can weaken evidence of signer identity, timing, and document integrity. Including unnecessary personal details can expose sensitive information beyond the personnel assigned to the incident. Using a draft instead of the official Attachment C version can omit required instructions, fields, or supporting sections.
Risks from incomplete Attachment C records
Signer dispute
Record integrity
Privacy exposure
Submission rejection
Legal standing of a completed report
A completed Attachment C may provide business evidence when the signer’s intent, consent, attribution, and reliable record retention are shown under ESIGN, 15 U.S.C. ch. 96, and applicable UETA law. Those frameworks do not override exclusions for wills, certain court orders, or family-law decrees; agency and state requirements still control this form’s filing.

Key features for Attachment C
signNow combines form preparation, recipient routing, authentication, and evidence preservation for organizations handling Attachment C incident reports.
Original form
Upload the official Attachment C PDF and prepare its existing structure without recreating the report manually.
Role routing
Assign fields and signatures to named participants before sending the incident report.
Audit trail
Capture authentication, timestamps, actions, and completion status for the signed record.
Signer security
Use SMS OTP or configured controls when the report requires stronger signer attribution.
Record control
Preserve the signed PDF, attachments, and audit evidence in a controlled record set.
Connected storage
Connect completed records with systems such as Box, Google Drive, or Microsoft 365.
Attachment C troubleshooting questions
These answers address field setup, signer routing, authentication, electronic-record rules, plan limits, and preservation for Attachment C.
Upload the official PDF again and inspect field placement before sending. signNow can detect fillable fields, but the sender remains responsible for confirming that every Attachment C field matches the printed instructions and has the correct recipient assignment.
Use signNow’s recipient routing and completion status to identify the unfinished participant. Resend the invitation or generate a permitted signing link, then retain the final completion certificate with the signed Attachment C report.
Business includes legally binding eSignatures, templates, and audit trails at $8/user/month when billed annually. The plan includes 100 signature invites per user per year; additional invite charges may apply.
For a consumer-facing electronic record, provide the ESIGN disclosure required by 15 U.S.C. §7001(c), including paper-record access and withdrawal procedures. Confirm the issuing agency accepts electronic completion before using a digital workflow.
Use SMS OTP or another configured authentication control when the incident record requires stronger signer attribution. signNow records authentication and signing events in the audit trail, but identity requirements may come from the organization or agency.
Export the completed PDF and audit trail from signNow, preserve the original and attachments, and apply the issuing agency’s retention schedule. ESIGN requires records to remain accessible and accurately reproducible, but it does not set one retention period for every report.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.