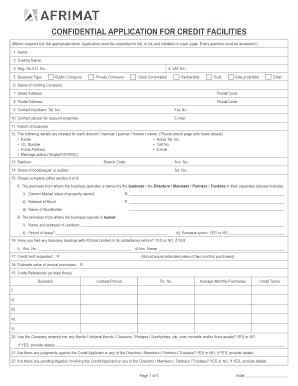
Credit Facility Application Form Stashfin
Use a Credit Facility Application Form Stashfin Pdf template to make your document workflow more streamlined.
What the Stashfin credit application is
The Credit Facility Application Form Stashfin is an application used to collect information from a person seeking a credit facility from Stashfin. It can contain identifying details, contact information, financial information, requested facility details, declarations, consent language, and signature fields. With signNow, an authorized sender uploads the form, reviews automatically detected fillable fields, assigns applicant and reviewer roles, sends the document, and receives the signed copy with an audit trail. The form’s exact lending requirements and approval decisions remain controlled by Stashfin and applicable U.S. law.
Who completes Stashfin application documents
Credit applicants
Stashfin applicants complete identity, contact, financial, and requested-credit sections before signing the application electronically.
Lending teams
Lending teams review submitted applications, request missing information, and preserve signed records with audit evidence.
Key features for Stashfin applications
signNow organizes the Credit Facility Application Form Stashfin from field preparation through signature collection and controlled record storage.
Field detection
Upload the Credit Facility Application Form Stashfin and review detected fields before assigning applicant, reviewer, and signature roles.
Role-based routing
Route the application electronically to applicants and authorized reviewers without printing or manually circulating multiple copies.
Audit trail
Capture signer actions, timestamps, and document history in an audit trail attached to the completed application.
Reusable template
Use reusable Stashfin templates to keep required lending fields and signature placements consistent across applications.
Connected storage
Store signed applications and completion records in connected systems such as Google Drive, Box, or NetSuite.
Mobile signing
Let applicants review and sign from supported mobile apps when the institution permits remote completion of this application.
How the Stashfin application workflow works
Complete the Credit Facility Application Form Stashfin through a controlled upload, field review, signing, and audit-trail workflow.
Upload form: Upload the Stashfin application PDF. Prepare fields: Review detected fields and add missing applicant fields. Send application: Send the application to the applicant and authorized reviewers. Store record: Collect signatures and retain the completed record.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
Recommended Stashfin workflow setup
Configure the Credit Facility Application Form Stashfin for verified applicants, controlled signatures, complete evidence, and institution-approved retention.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Typed or drawn electronic signature |
| Audit trail | Capture signer actions and timestamps |
| Document retention | Use the institution’s documented lending schedule |
| Encryption | TLS 1.2/1.3 and AES-256 protection |



What the Stashfin audit trail records
The audit trail documents the signing evidence surrounding a completed Credit Facility Application Form Stashfin rather than merely recording account setup.
Authenticate signer:
Record timestamp:
Track document history:
Seal completion:
Link evidence:
Export audit trail:
Record-keeping practices for Stashfin applications
Preserve the application, consent evidence, completed document, and audit trail under a documented financial-records policy.
Verify every Stashfin field
Limit access by lending role
Preserve the complete record
Test secure retrieval
Privacy controls for Stashfin applications
Applicant income, address, and identity details can remain visible in downloaded signed copies shared beyond the lending team. Missing consent language may weaken evidence that the applicant agreed to electronic records and credit-related disclosures. Unrestricted template access can let unauthorized staff alter lending fields before an applicant receives the application. Emailing completed applications without controlled permissions can expose financial information to unintended recipients or personal accounts.
Security controls for Stashfin data
Transport encryption:
Stored encryption:
Control assurance:
Security certification:
Electronic signatures:
Protected health information:
Risks from mishandling Stashfin applications
Electronic consent
Application dispute
Privacy exposure
Evidence gap
Troubleshooting Stashfin application workflows
Resolve field, consent, plan, security, and compliance questions before sending a Credit Facility Application Form Stashfin application.
Upload the original Credit Facility Application Form Stashfin as a readable PDF, then review signNow’s detected fields. Add or reposition fields manually when the source file contains flattened text, scanned sections, or unlabeled signature areas.
The Business plan includes legally binding eSignatures, audit trails, templates, and mobile apps at $8 per user per month with annual billing. Business Premium adds bulk send at $15 per user per month annually.
Use signNow’s audit trail to preserve the signer’s actions, timestamps, and document history. ESIGN and UETA recognize electronic signatures when intent, consent, attribution, and record retention requirements are satisfied.
For consumer-facing applications, provide the ESIGN Act electronic-record disclosure, explain the right to receive paper records, confirm electronic access, and explain withdrawal procedures under 15 U.S.C. §7001(c).
HIPAA compliance applies when the workflow handles protected health information and requires a business associate agreement. A credit application alone does not establish that HIPAA applies.
Use role-based access, approved templates, and controlled storage for applicant data. signNow encrypts data in transit with TLS 1.2/1.3 and at rest with AES-256; configure organizational retention separately.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.