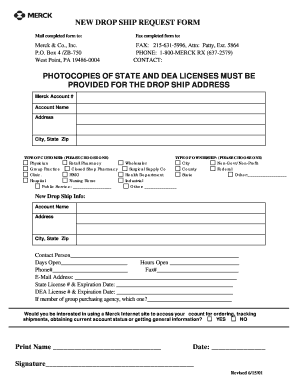
New Drop Ship Request Form Photocopies Of Merck
Use a NEW DROP SHIP REQUEST FORM PHOTOCOPIES OF Merck template to make your document workflow more streamlined.
What this Merck request form does
The New Drop Ship Request Form Photocopies Of Merck is a business request document for recording a photocopy drop shipment connected with Merck-related operations. The supplied form name does not identify an issuing agency, statutory filing deadline, required fields, or a special signature rule. In signNow, a sender uploads the approved source file, checks detected fillable fields, adds the responsible signer, and sends it for review. The completed PDF, signer activity, timestamps, and audit trail can then be stored together for fulfillment and later reference.
Who uses this drop ship request form
Procurement and logistics
Procurement and logistics teams can use this form to document a request for Merck-related drop shipment photocopies, confirm recipient details, and preserve approvals before fulfillment. Because the source does not identify an issuing agency or mandatory field list, users should compare every completed field with the organization’s approved template and shipment instructions.
Operations and compliance
Operations, compliance, and authorized business partners can review the completed request when a photocopy must be delivered, shared, or retained. Contracts, NDAs, HR forms, invoices, and consent forms may require separate workflows; do not substitute this request form for those documents unless the source template expressly includes them.
Recommended setup for this request
Configure the New Drop Ship Request Form Photocopies Of Merck around the approved source file, authorized recipients, and documented fulfillment controls.
| Setting | Recommendation |
|---|---|
| Authentication method | Email verification with SMS OTP |
| Signature type | Intent-based electronic signature |
| Audit trail | Exported completion certificate and history |
| Document retention | Records-owner-approved retention schedule |
| Encryption and provisioning | AES-256 storage with admin-managed roles |
Complete this form in signNow
Use the approved New Drop Ship Request Form Photocopies Of Merck file and verify every detected field before sending it to the authorized signer.
Upload:
Upload the approved source file. Check fields:
Review detected fields against the original. Assign signer:
Assign the authorized Merck request signer. Send:
Send for review and signature. Store:
Download the completed PDF and audit trail.
 Best ROI. Our customers achieve an average 7x ROI within the first six months.
 Scales with your use cases. From SMBs to mid-market, airSlate SignNow delivers results for businesses of all sizes.
 Intuitive UI and API. Sign and send documents from your apps in minutes.
What the audit trail records
The audit trail links the Merck request to signer activity, document events, and the completed file used for fulfillment review.
Authenticate signer:
Capture timestamps:
Track document history:
Seal completion:
Export evidence:
Retrieve record:
Signer authentication for this request
PKI certificates:
X.509 certificates:
Two-factor authentication:
SMS OTP:
ID verification:
Authentication evidence:
Privacy and disclosure pitfalls
Shipment addresses and contact details may remain visible in downloaded photocopies shared beyond the authorized Merck procurement or logistics group. A signer may complete the request without clearly recording consent for electronic delivery, creating uncertainty about the approved communication method. Broad folder permissions can expose completed drop ship requests, audit trails, or recipient information to unauthorized internal users. Forwarded email attachments can create uncontrolled duplicate copies after the signed request leaves the approved document workspace.
Record-keeping practices for this form
Retain the completed New Drop Ship Request Form Photocopies Of Merck according to its record category, contract obligations, and any applicable privacy rule.
Classify the completed form before retention
Export the audit trail with the PDF
Archive copies in controlled storage
Map retention to the governing rule
Retention periods depend on record class
The form name alone does not establish a retention period. Select a record class only when the completed request genuinely belongs to that regulated record set.
Tax records — 3 years after filing
HIPAA records — 6 years from creation
FLSA payroll — 3 years
OSHA injury records — 5 years
SOX audit records — 7 years
Risks from incomplete request records
Unapproved shipment
Delivery dispute
Evidence gap
Integrity challenge
Privacy incident



Troubleshooting this Merck request workflow
Resolve field, signer, plan, and compliance questions by checking the source form, recipient identity, and retained audit evidence.
Upload the approved source PDF again and compare its pages with the Merck request copy. signNow can auto-detect fillable fields, but the sender remains responsible for correcting misplaced or missing fields before assigning a signer.
Open the recipient details and resend the invitation after confirming the email address. If stronger attribution is required, enable SMS OTP or another available authentication method and retain the resulting event in the audit trail.
Business includes legally binding eSignatures, templates, audit trails, and mobile apps at $8 per user per month with annual billing. It includes 100 signature invites per user yearly; overages may apply.
Use Business Premium at $15 per user per month annually when this workflow requires bulk send. The plan adds bulk send, kiosk mode, request payments, and quick invite links; pricing is higher for month-to-month billing.
signNow is ESIGN and UETA compliant, but the form still needs signer intent, consent, attribution, and retained reproducible records. Review the source template and business policy before relying on an electronic signature.
For protected health information, HIPAA compliance requires a business associate agreement. Do not place PHI in the request unless the workflow, access controls, and retention policy have been approved for that use.
Key performance indicators that demonstrate SignNow's proven track record.
BE READY TO GET MORE
Get this form now!

If you believe that this page should be taken down, please follow our DMCA take-down process.